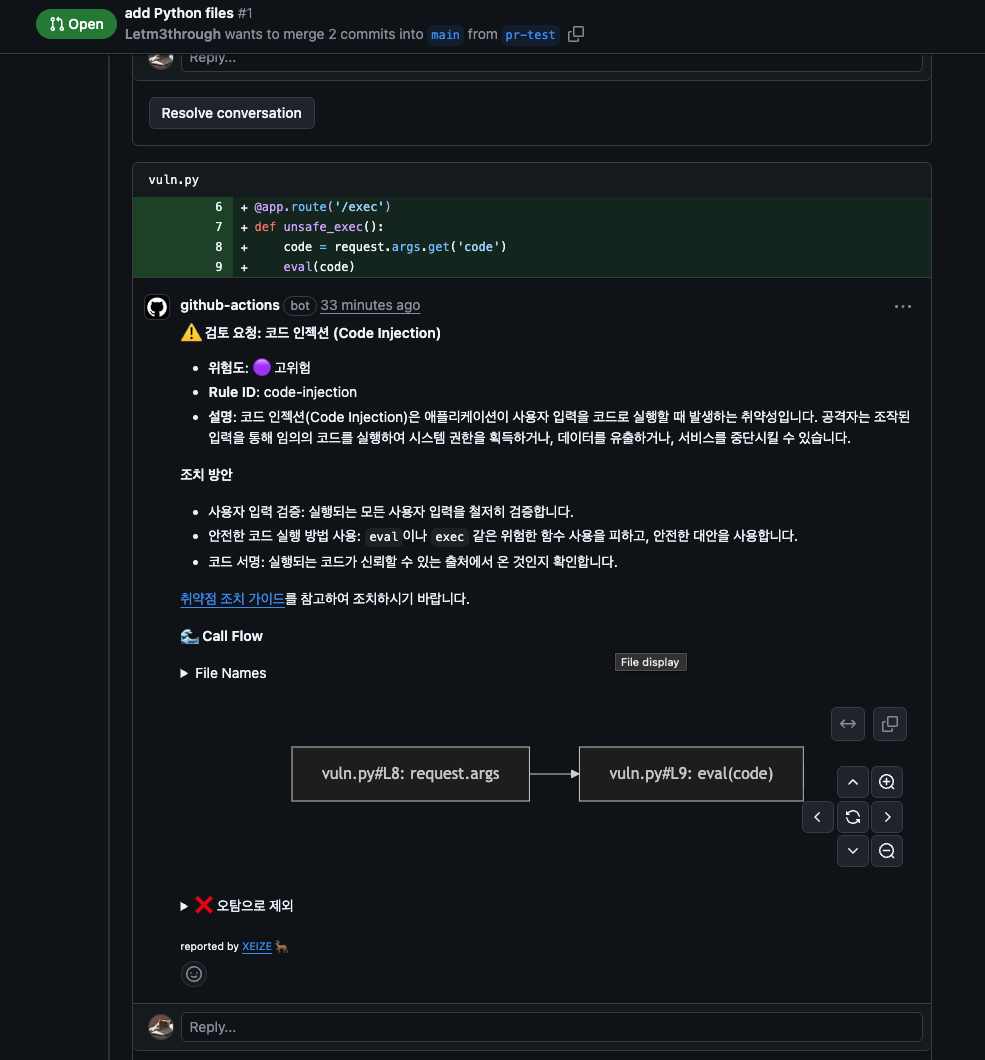
1. Add XEIZE_TOKEN
Add the XEIZE_TOKEN secret for GitHub Actions as shown below.
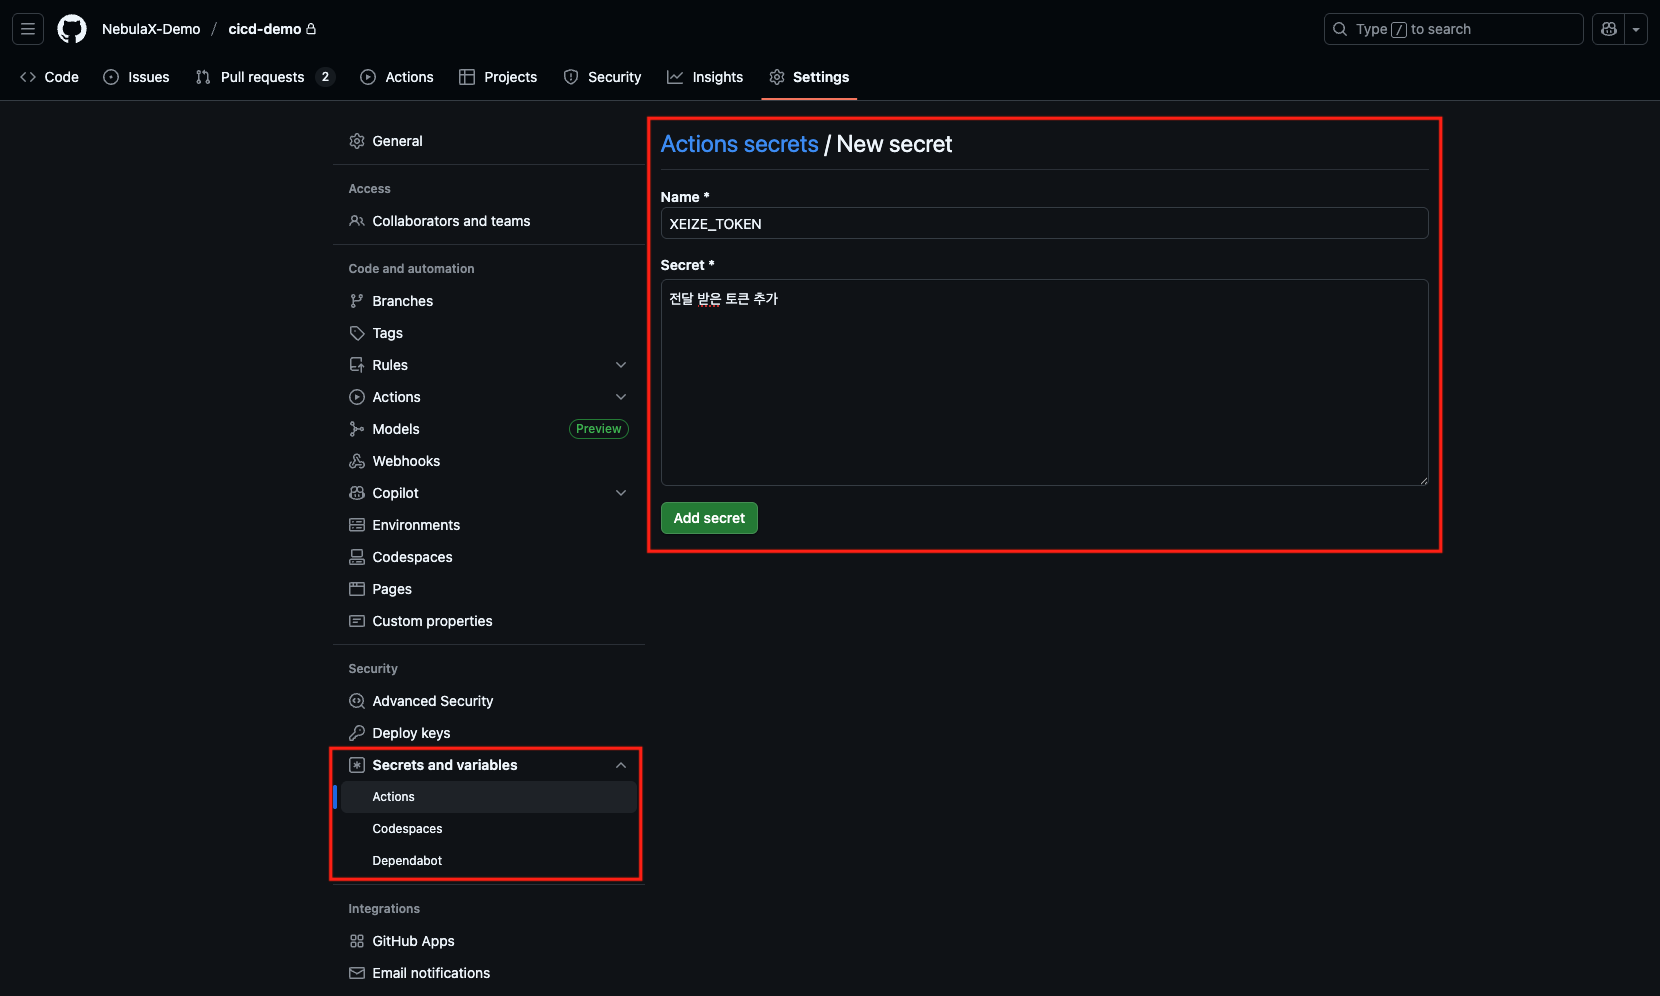
2. Add a GitHub Actions workflow
Click the + button to create a file.
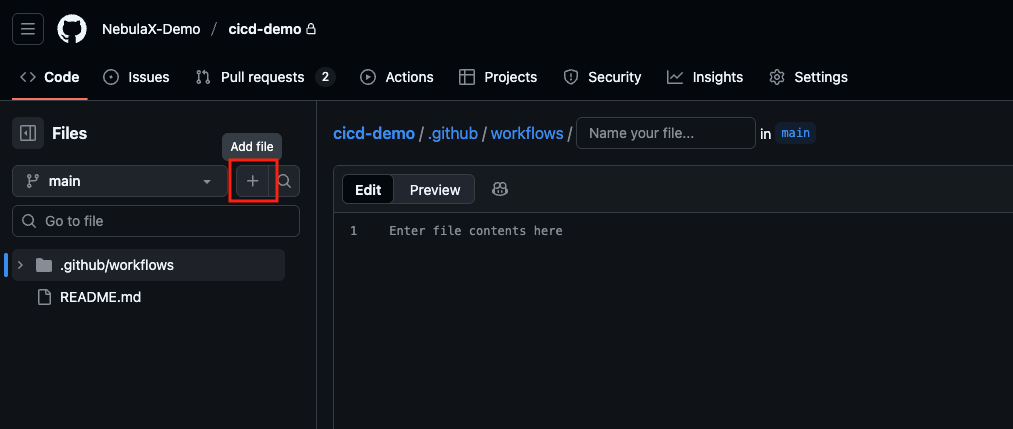
Add the workflow content, then select Commit changes to save and enable the workflow.
Use the configuration on the GitHub Actions page.
3. Verify with a PR
Clone the repository
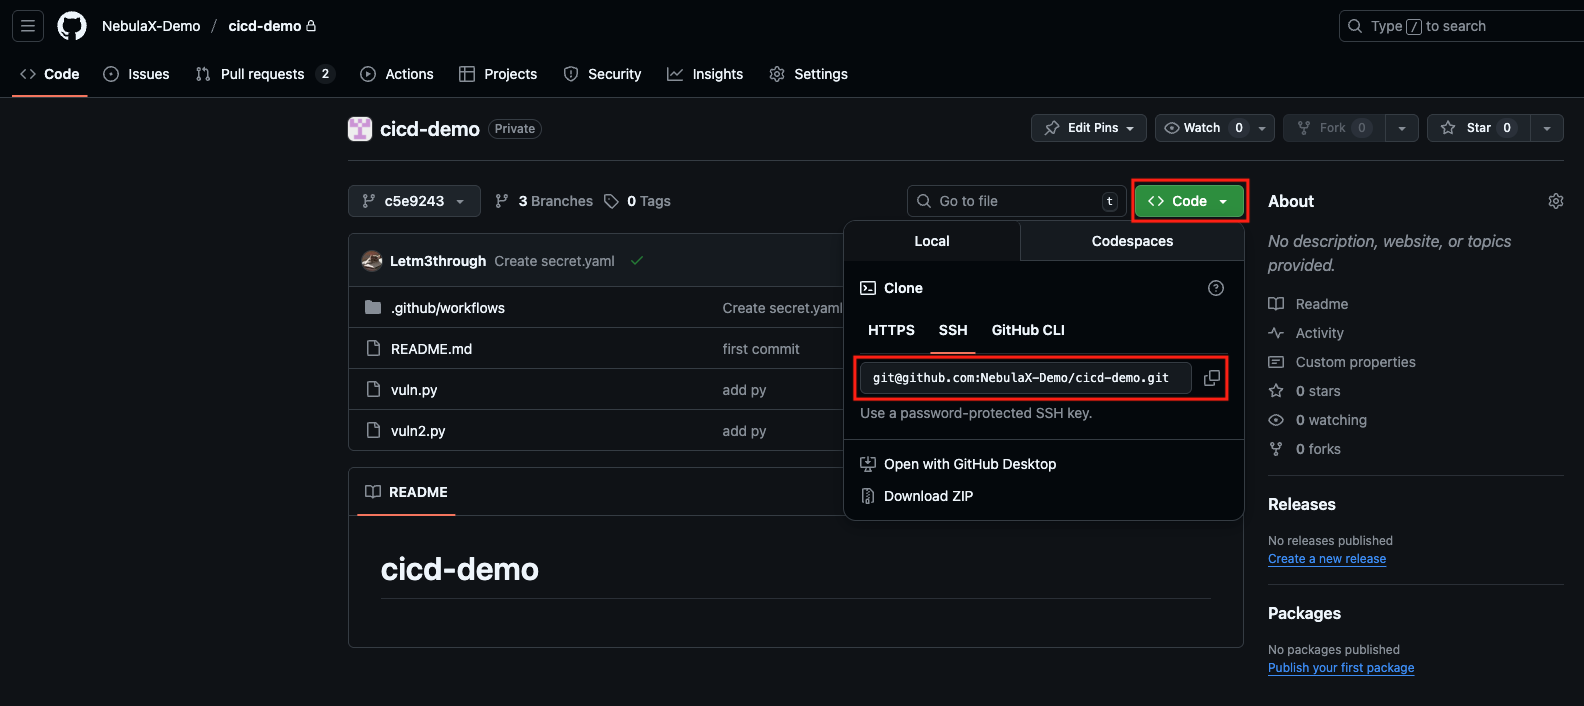
Clone the repository containing the GitHub Actions workflow. In git clone REPOSITORY_URL, replace REPOSITORY_URL with the copied repository URL.
Find the clone URL as shown below.
Create a branch
Prepare the pull request in your terminal.
- Run
cd repositoryto enter the cloned directory, replacingrepositorywith its actual name. - Run
git checkout -b pr-testto create thepr-testbranch. - Create the following intentionally vulnerable files in that directory.
vuln_crypto.py
python
# Unsafe Crypto Algorithm + Hardcoded key
from Crypto.Cipher import DES
ENCRYPTION_KEY = b"weak_key"
cipher = DES.new(ENCRYPTION_KEY, DES.MODE_ECB)
vuln_exec.py
python
# Unsafe Flask RCE
from flask import Flask, request

app = Flask(__name__)

@app.route('/exec')
def unsafe_exec():
    code = request.args.get('code')
    eval(code)
    return "Dangerous Code executed"
- After creating the files, run:
text
git add .
git commit -m "add tests"
git push origin pr-test
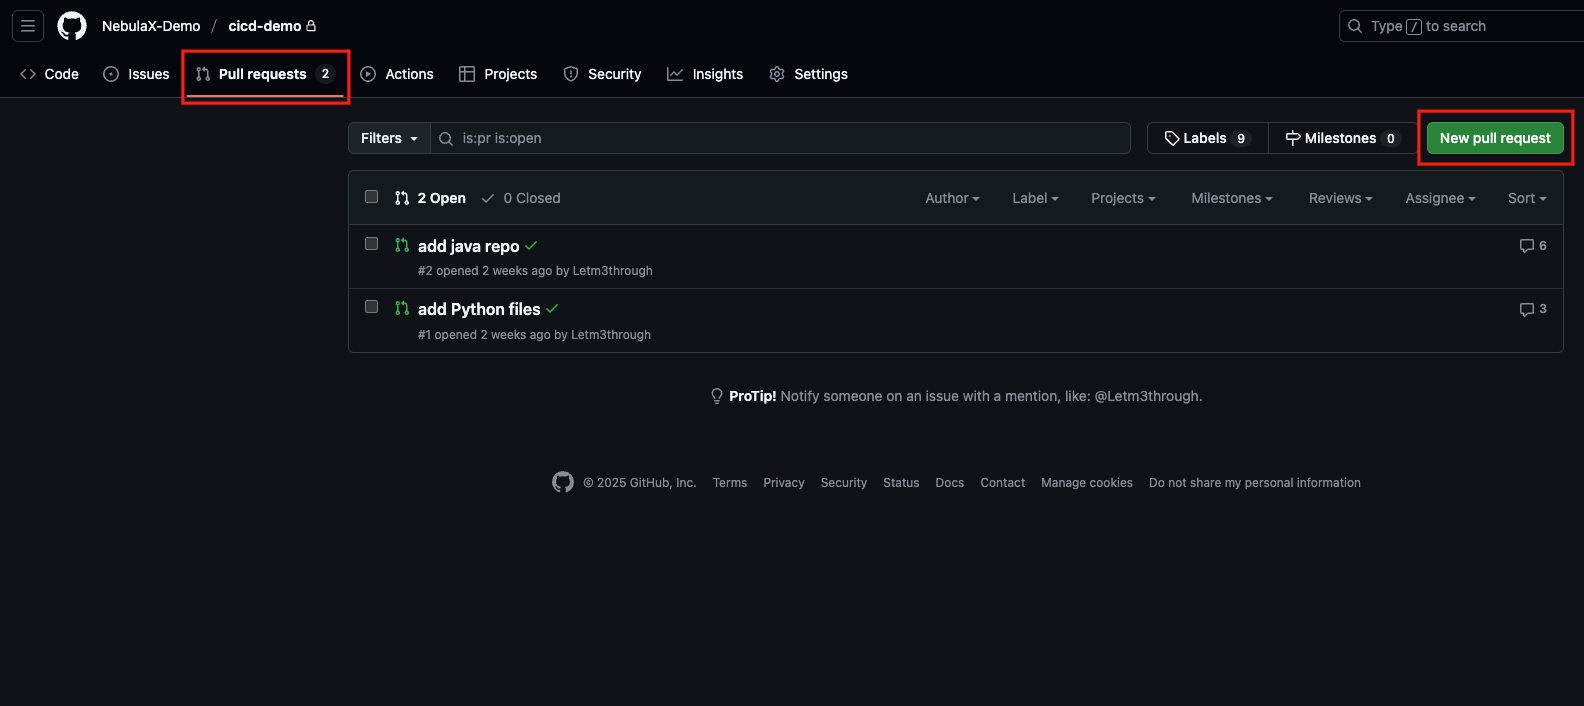
- Return to the repository, open
Pull requests, and selectNew pull request.
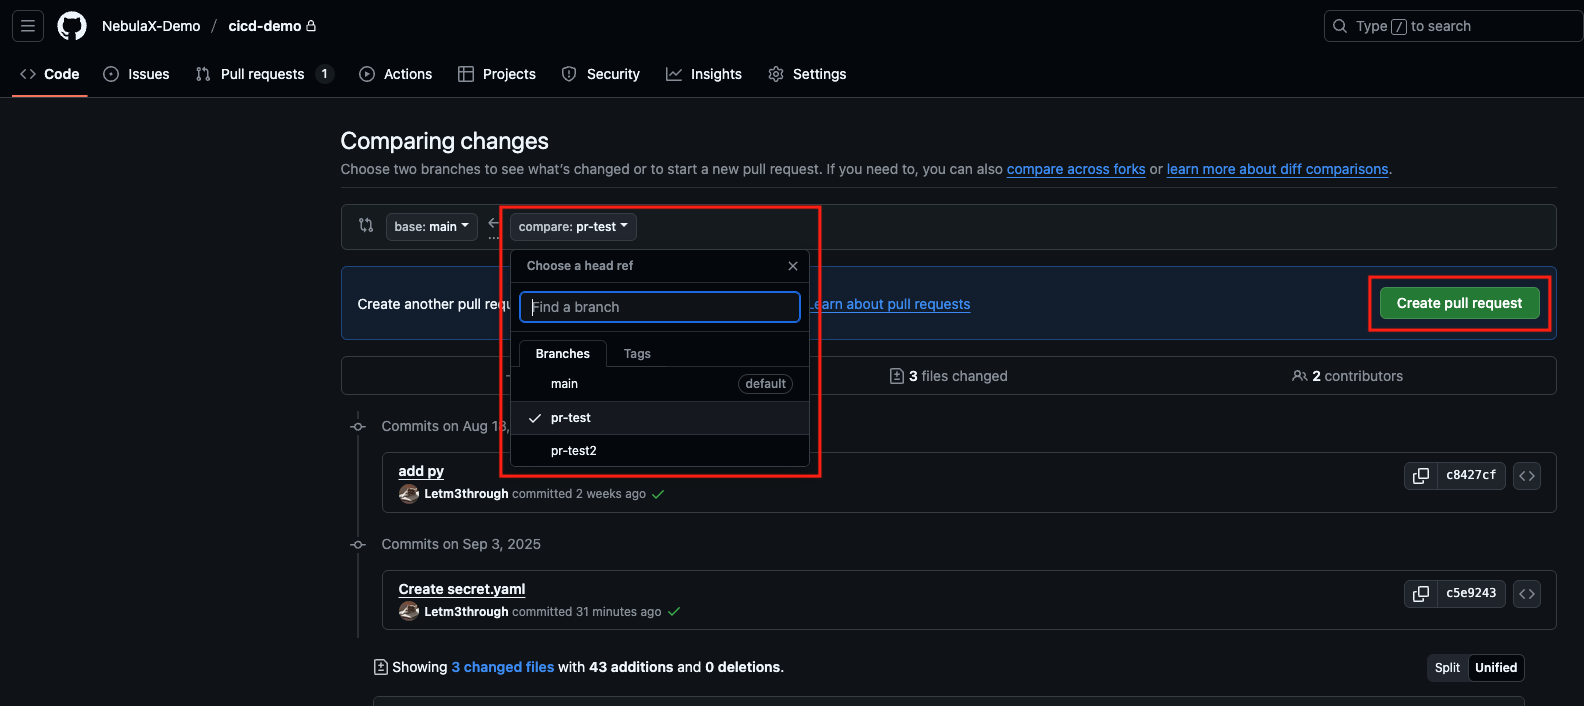
- Select
pr-test, then chooseCreate pull request.
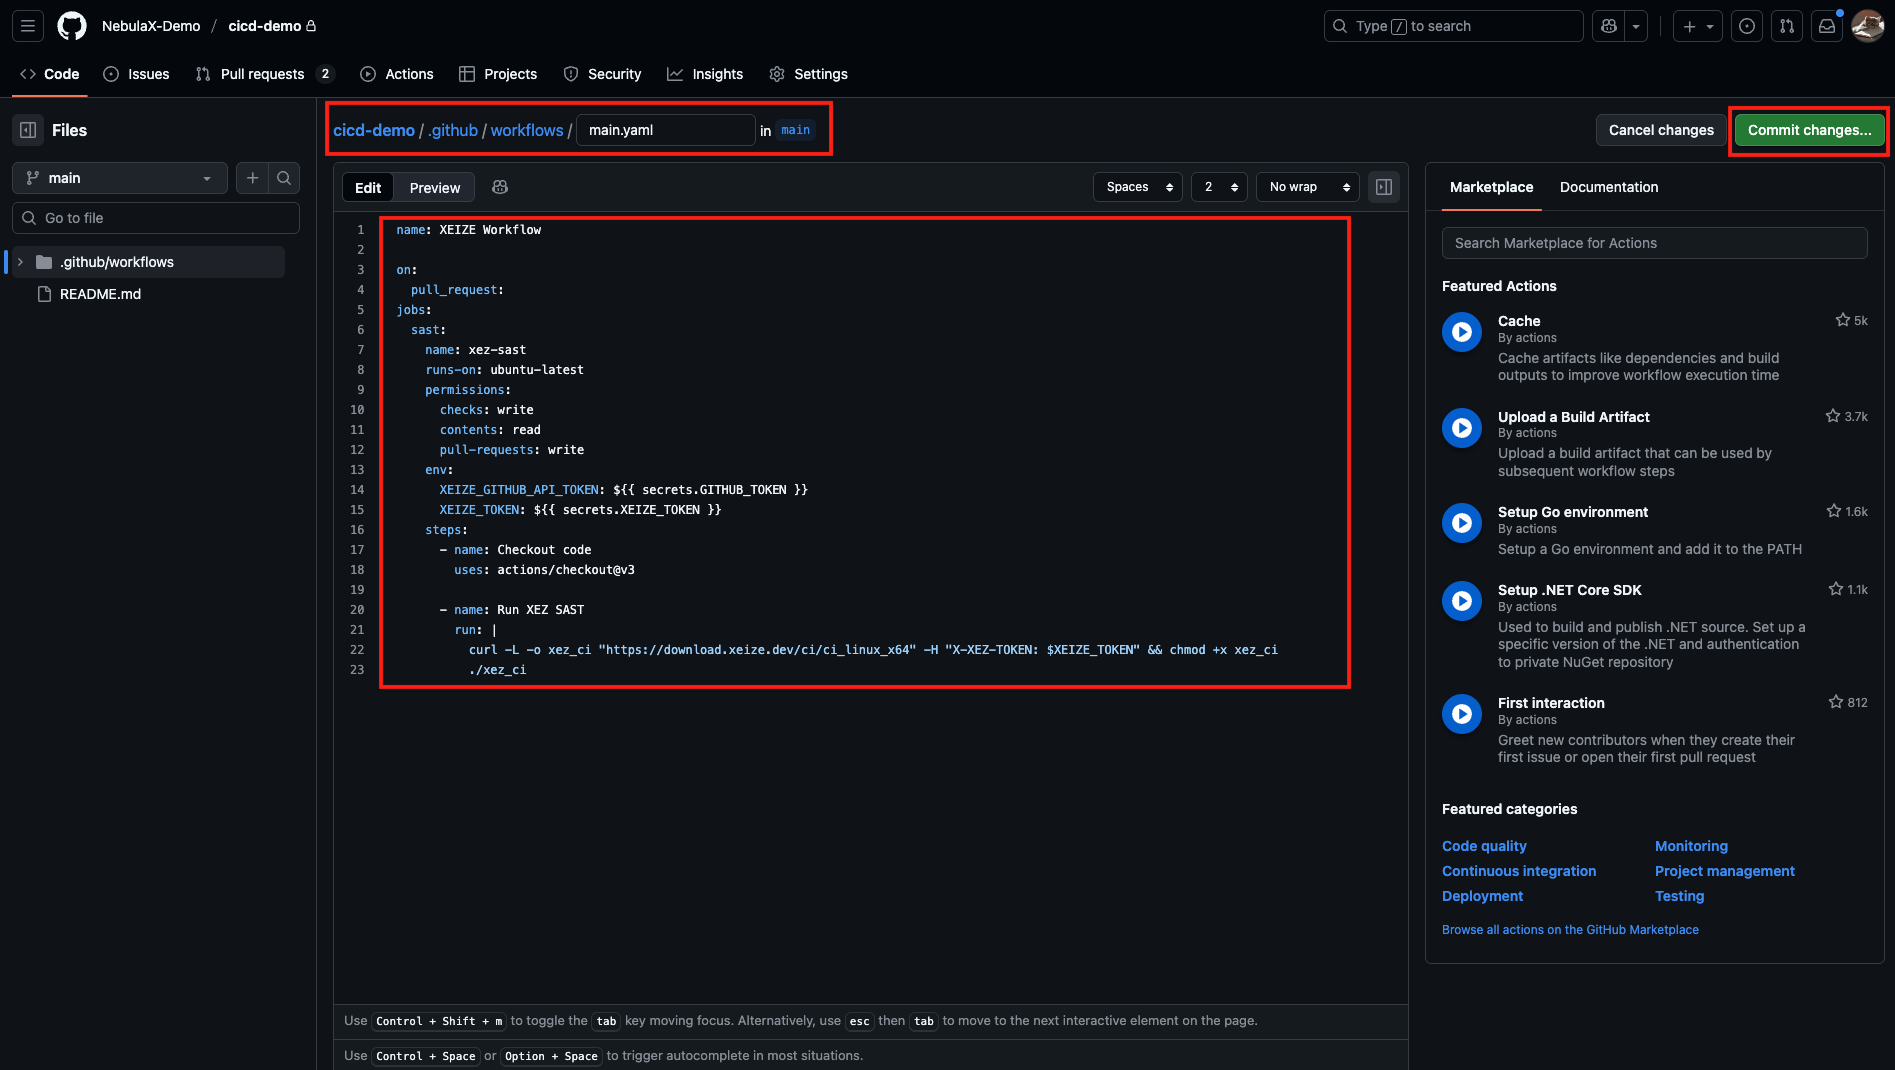
- Once GitHub Actions finishes, check that comments appear as shown below.