1. Add XEIZE_TOKEN
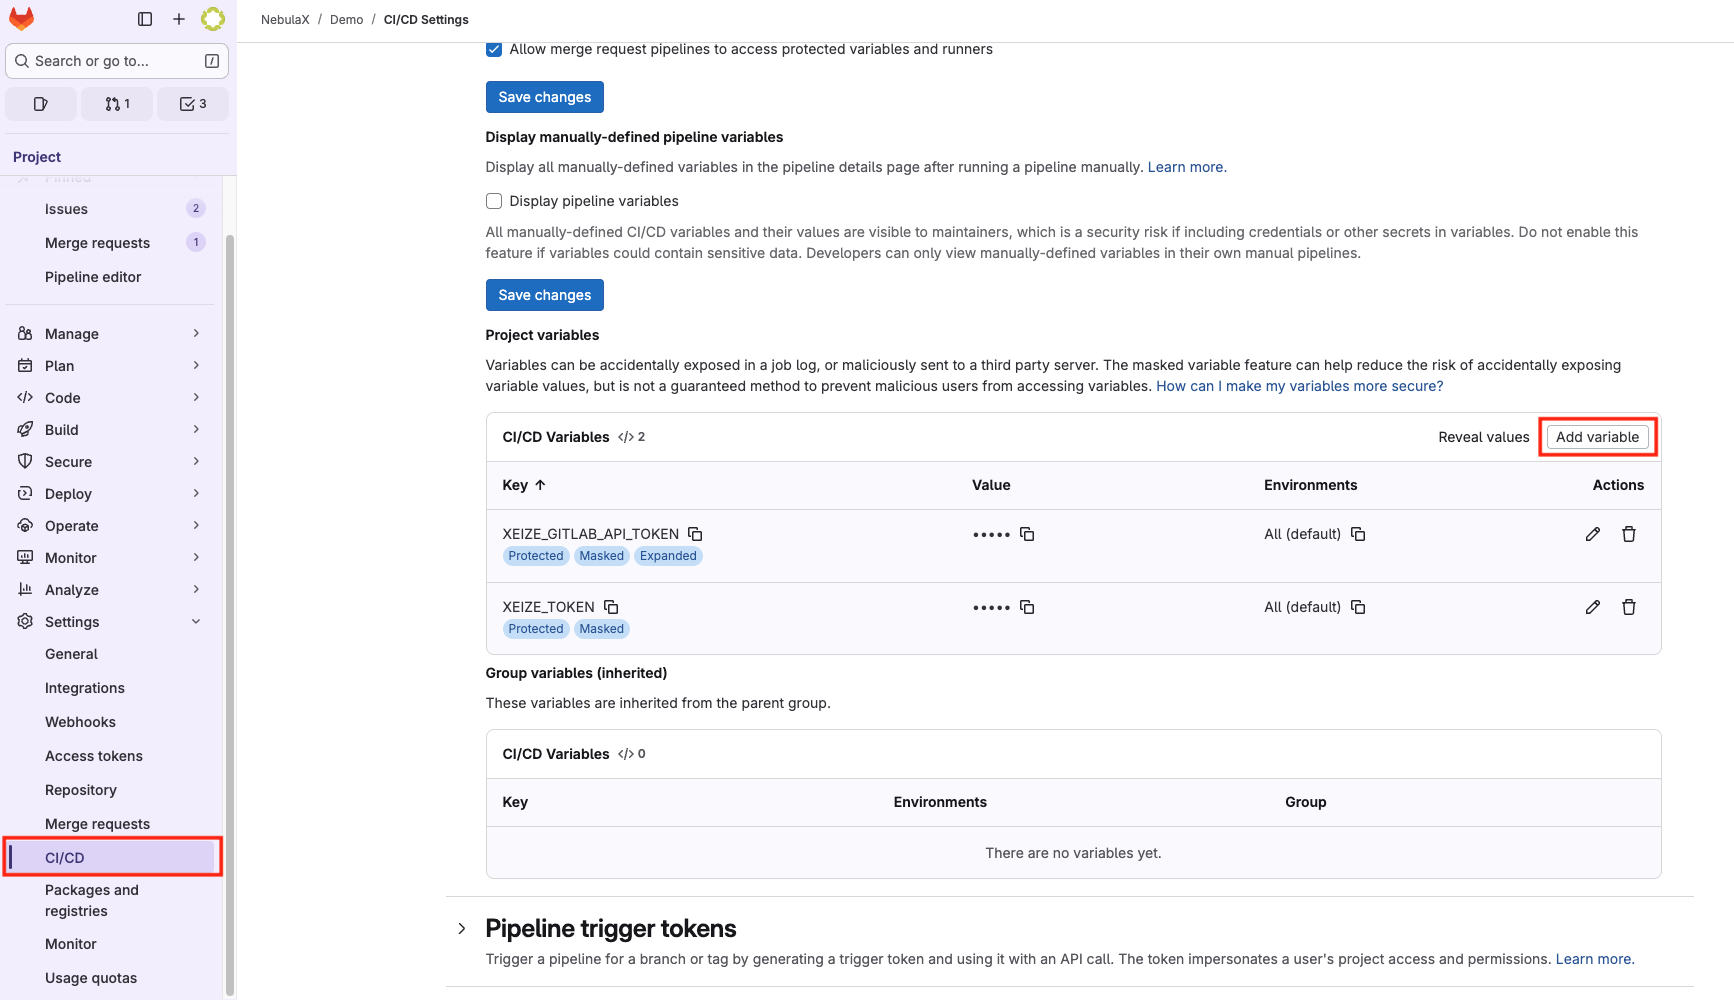
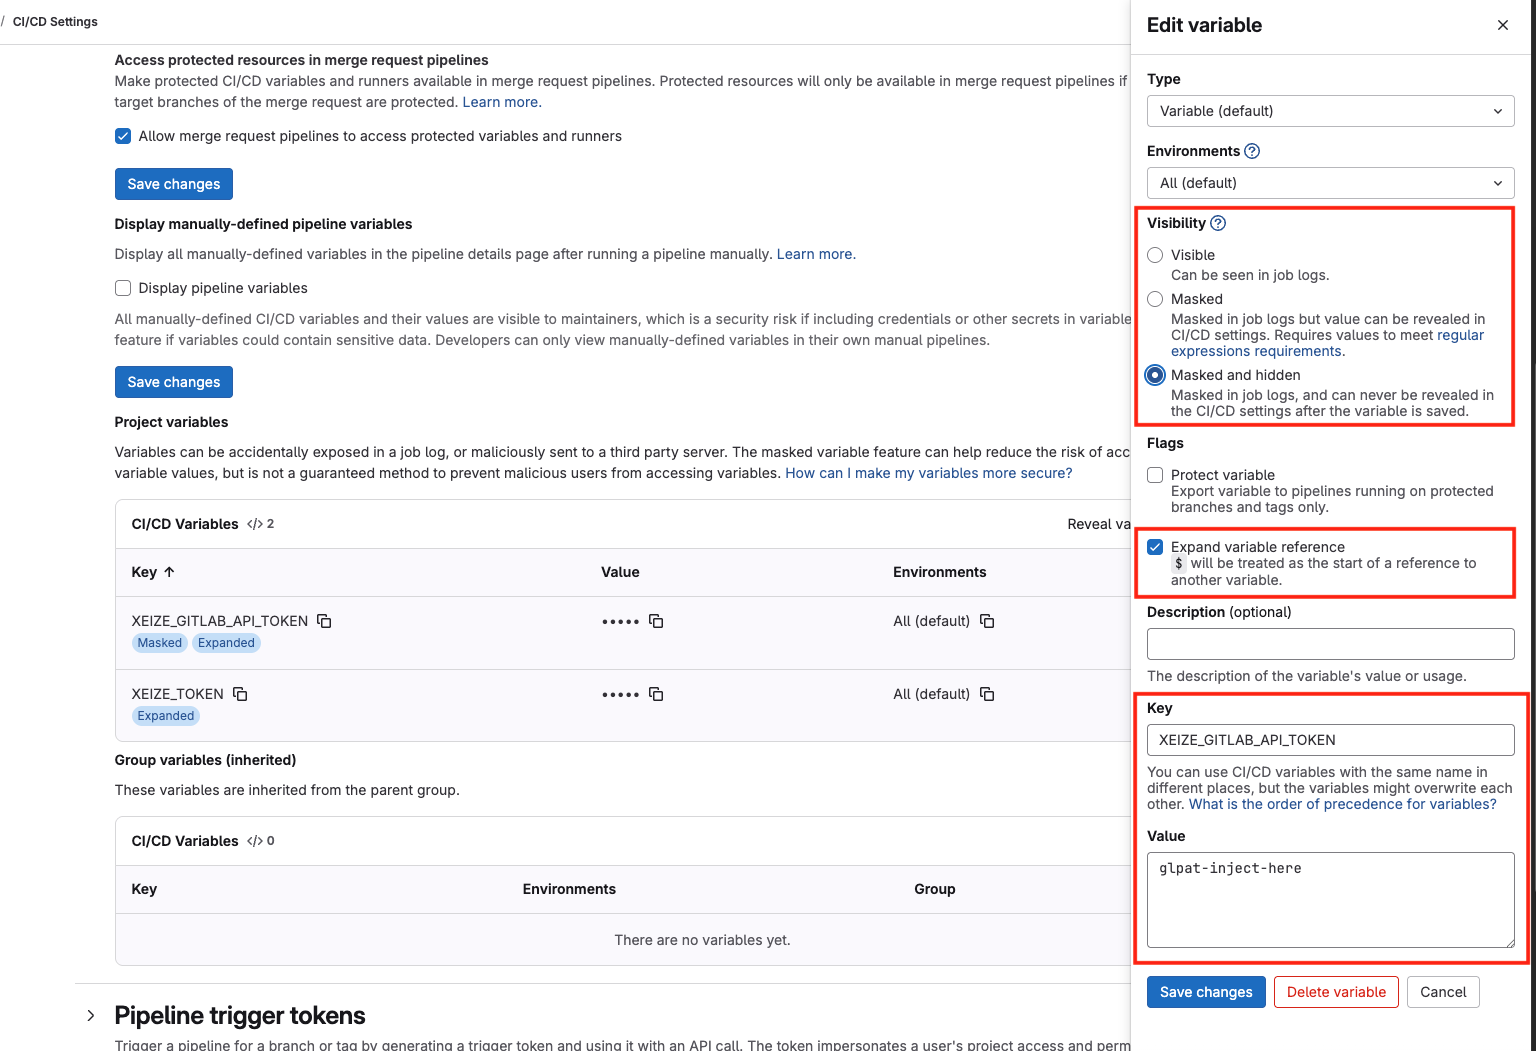
Add XEIZE_TOKEN and XEIZE_GITLAB_API_TOKEN as CI/CD variables for GitLab Workflow.
Open Settings > CI/CD to add the variables.
- api
2. Add the GitLab workflow
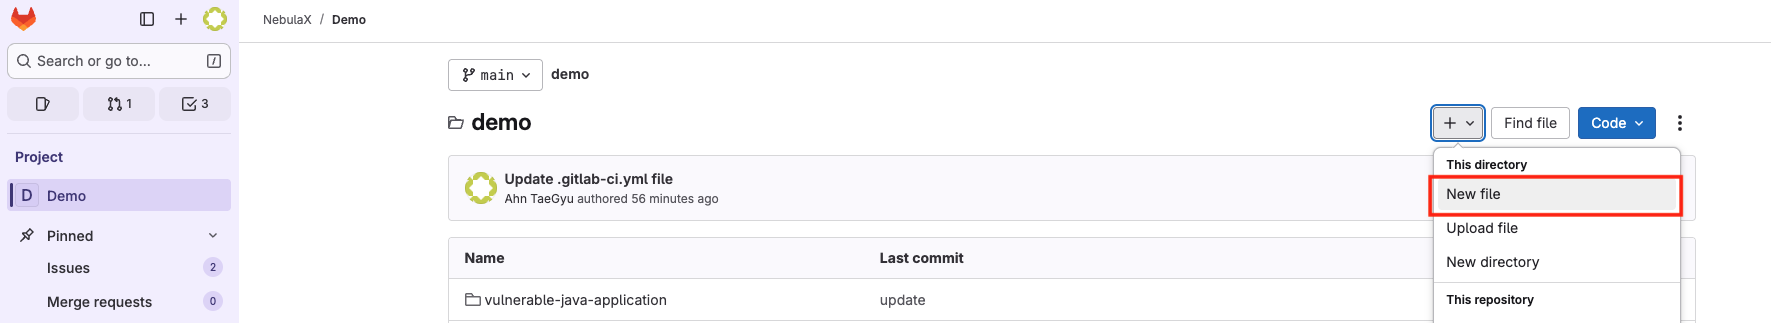
Select New file from the + menu to create a file.
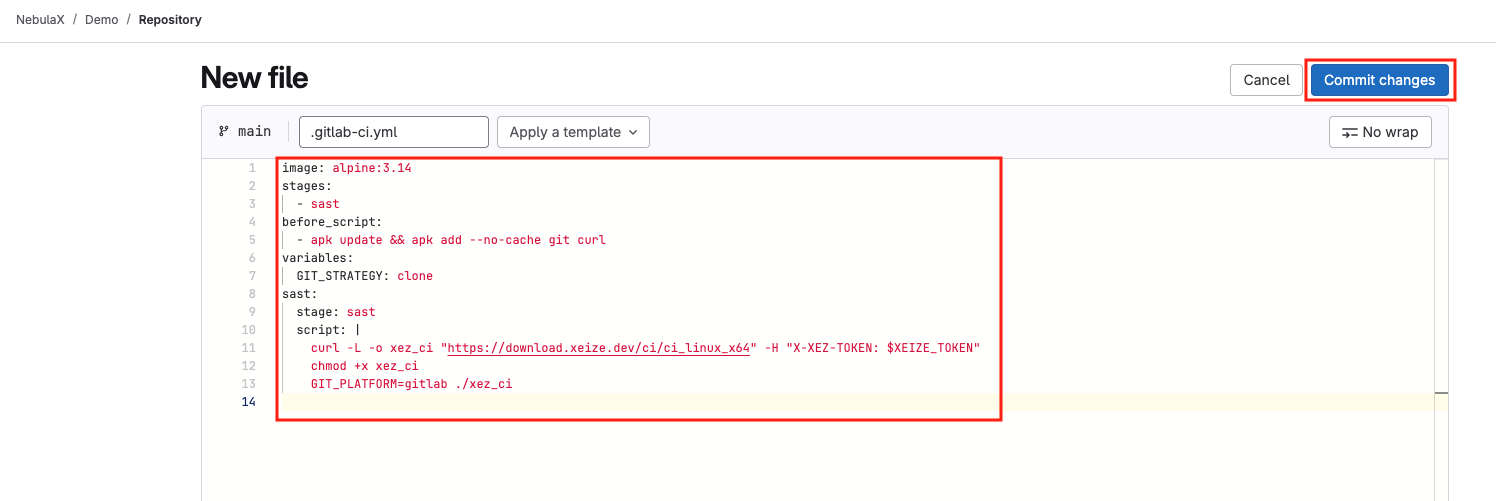
Add the configuration and select Commit changes to save and enable the GitLab pipeline.
Use the configuration on the GitLab Workflow page.
3. Verify with an MR
Clone the repository
Clone the repository containing the GitLab pipeline, using its actual URL in place of the example git clone https://gitlab.com/....
Create a branch
Prepare the merge request in your terminal.
- Run
cd repositoryto enter the cloned directory, replacingrepositorywith its actual name. - Run
git checkout -b pr-testto create thepr-testbranch. - Create the following intentionally vulnerable files.
vuln_crypto.py
python
# Unsafe Crypto Algorithm + Hardcoded key
from Crypto.Cipher import DES
ENCRYPTION_KEY = b"weak_key"
cipher = DES.new(ENCRYPTION_KEY, DES.MODE_ECB)
vuln_exec.py
python
# Unsafe Flask RCE
from flask import Flask, request

app = Flask(__name__)

@app.route('/exec')
def unsafe_exec():
    code = request.args.get('code')
    eval(code)
    return "Dangerous Code executed"
- After creating the files, run:
text
git add .
git commit -m "add tests"
git push origin pr-test
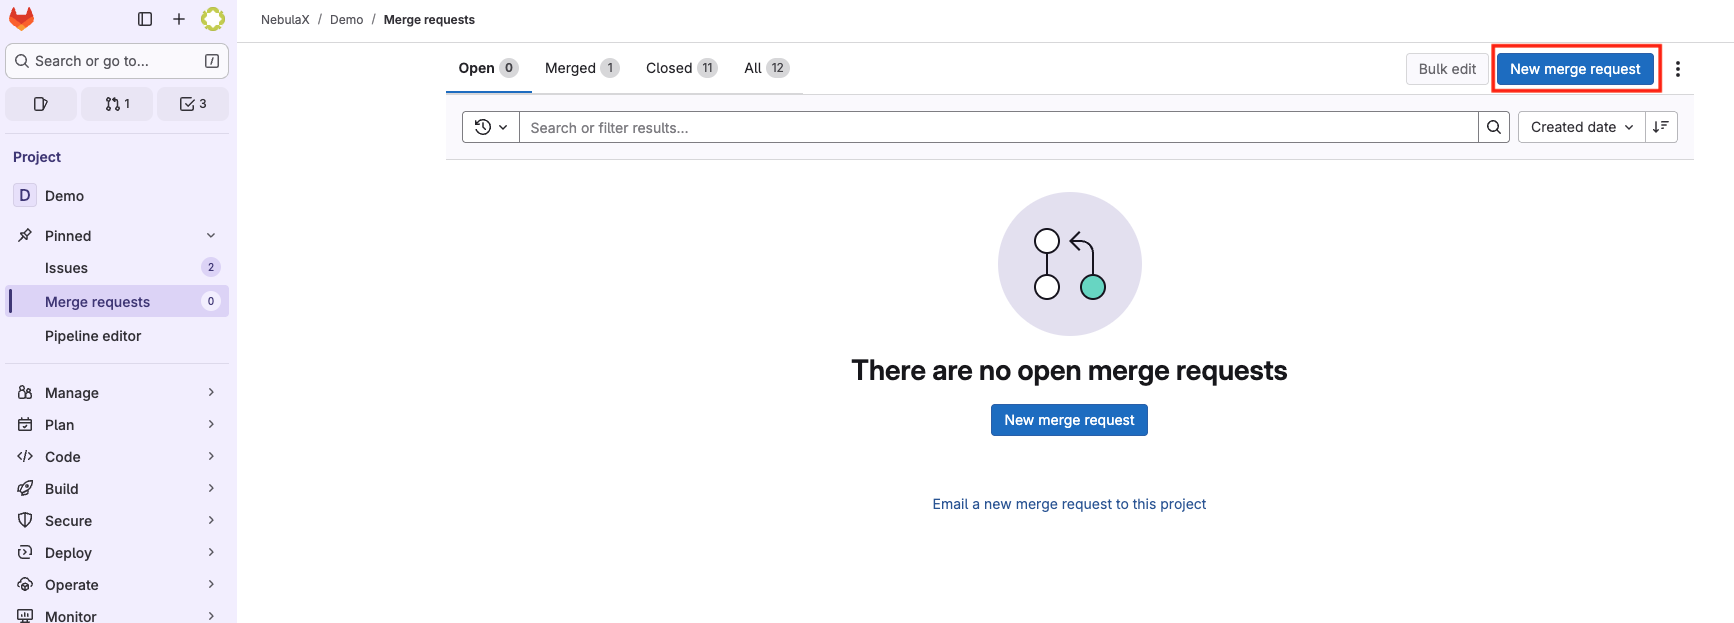
- Return to the project containing the GitLab workflow and select
New merge request.
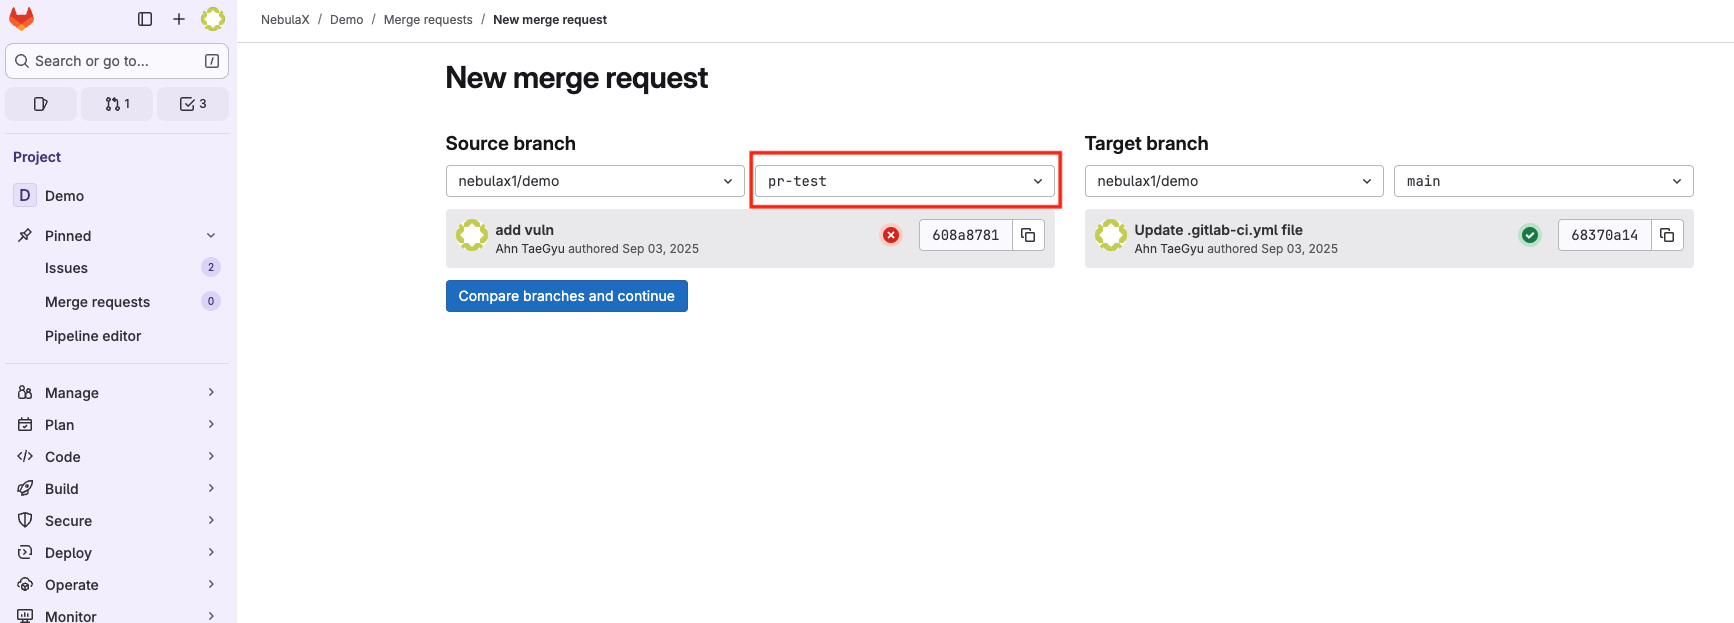
Select pr-test, then choose Compare branches and continue.
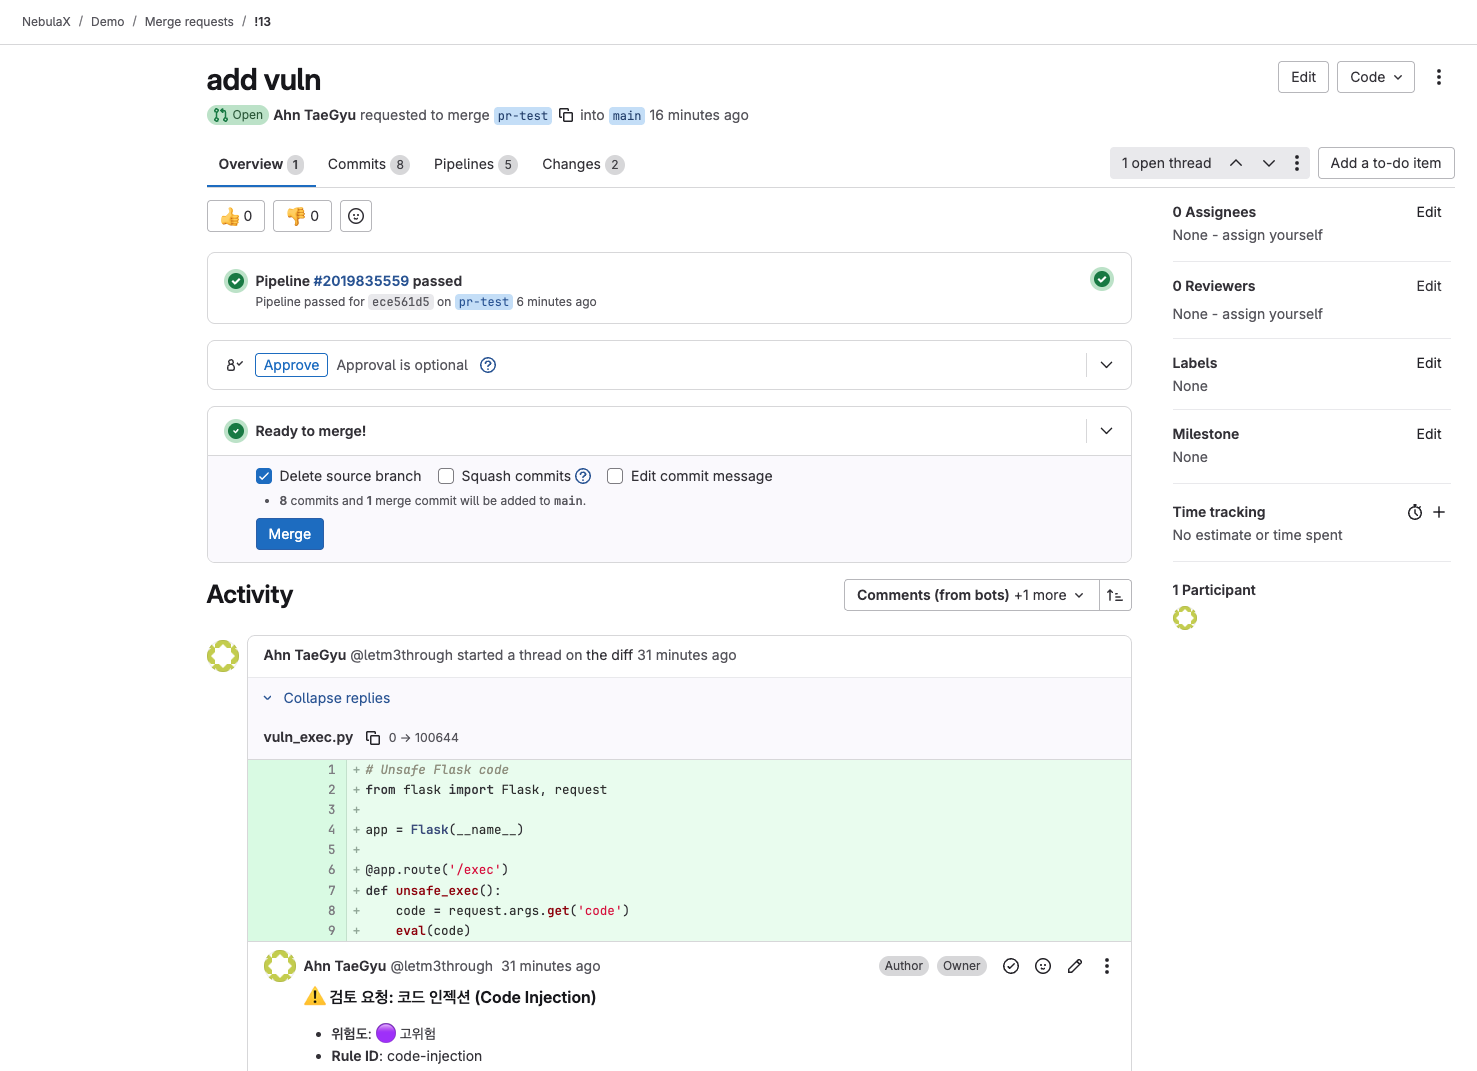
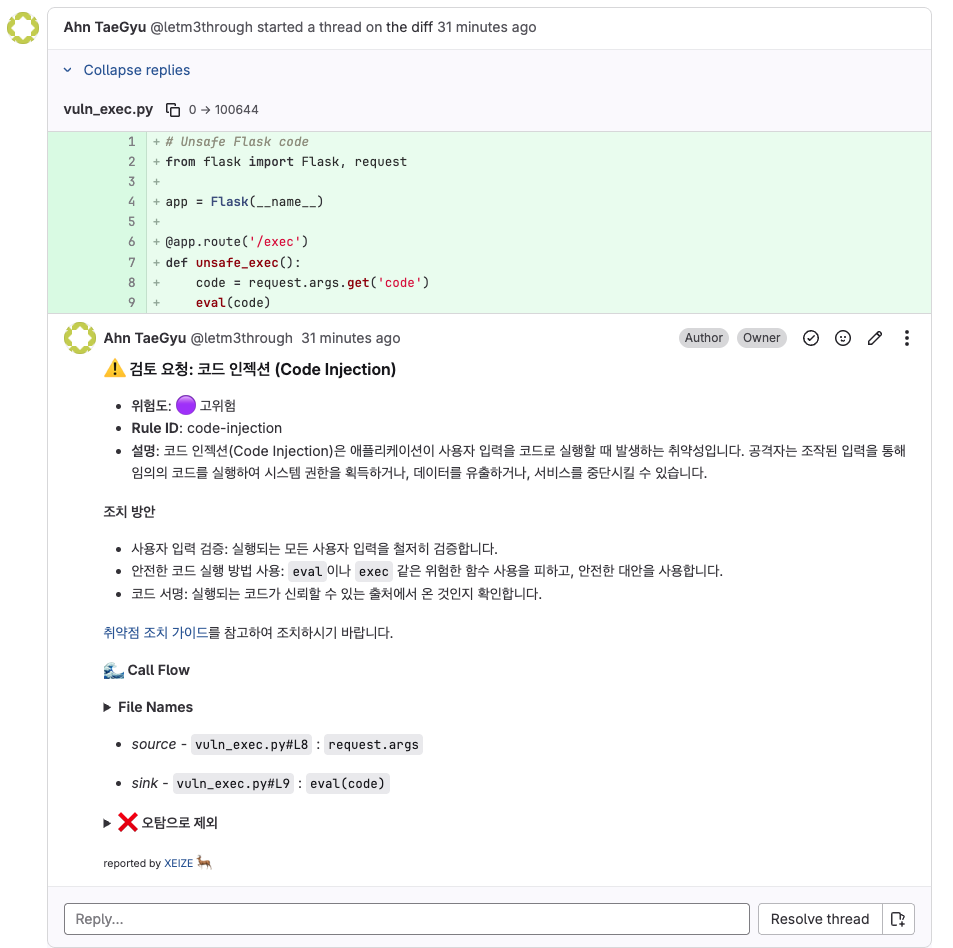
- Check that comments appear as shown below.