
1. Create an Okta app integration
Sign in to Okta and open Admin Console > Applications > Create App Integration.
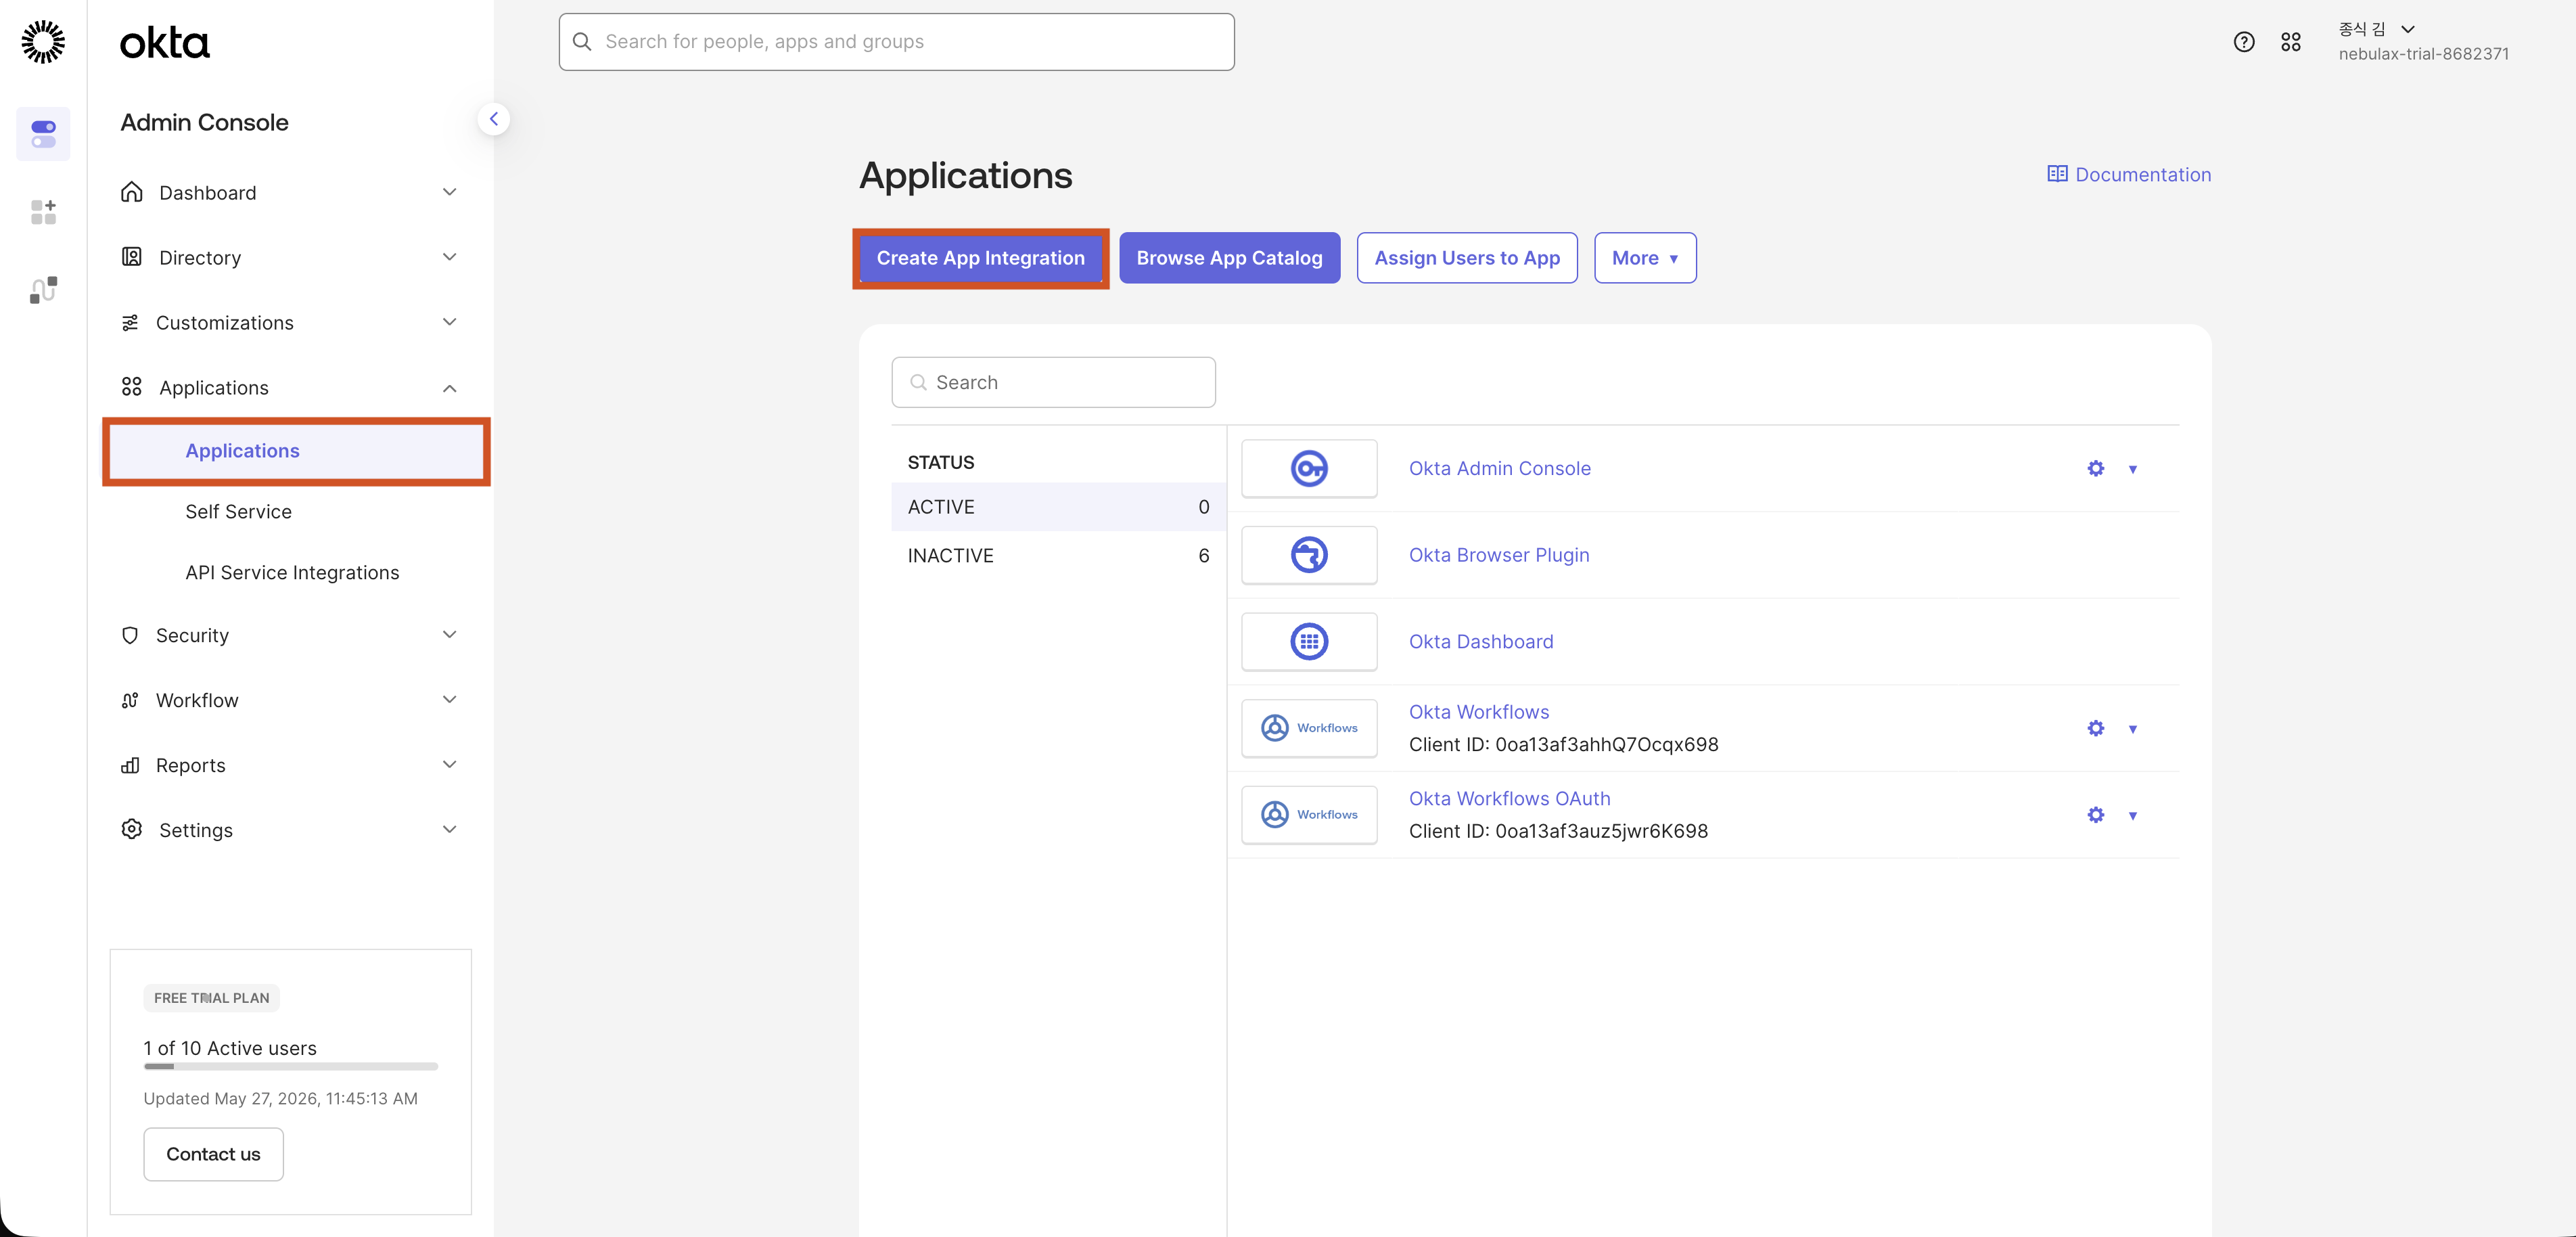
Select SAML 2.0 as the sign-in method.
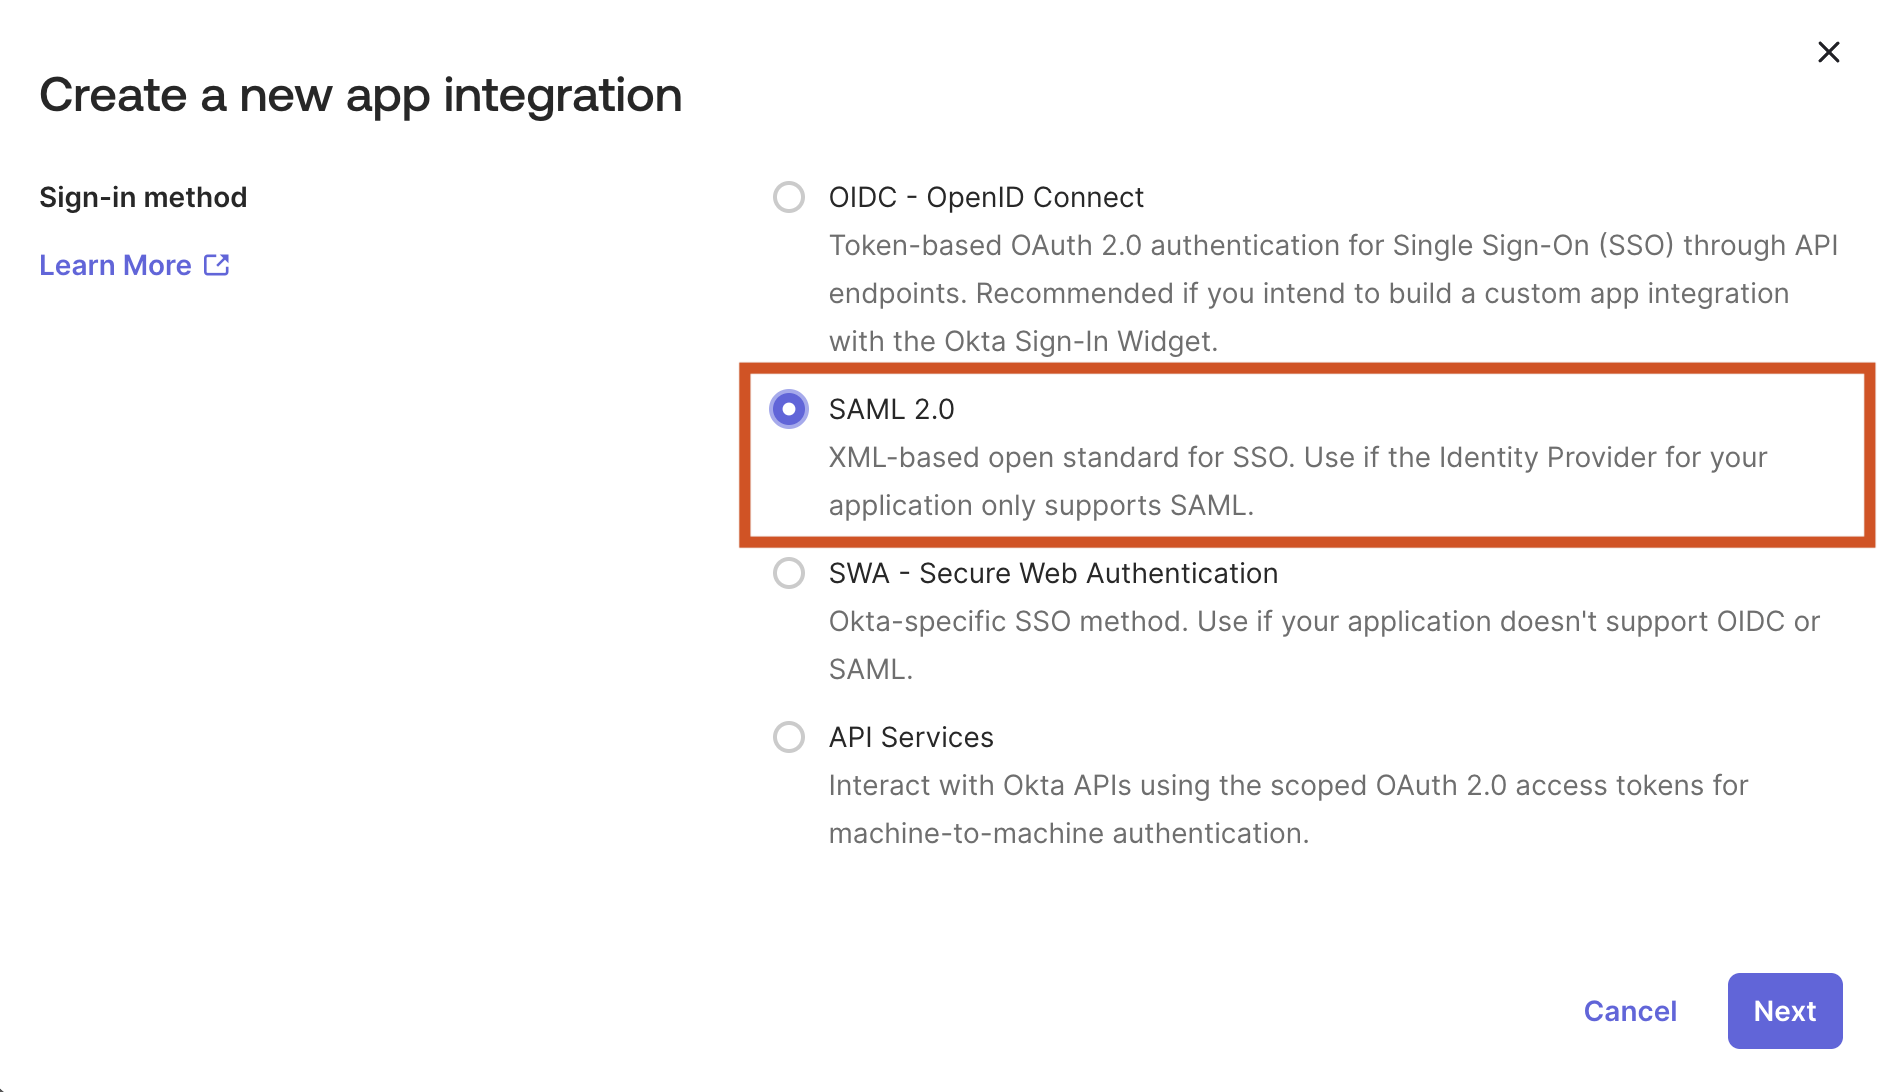
2. Set the app name
Enter a name for the SAML app you will use with XEIZE.
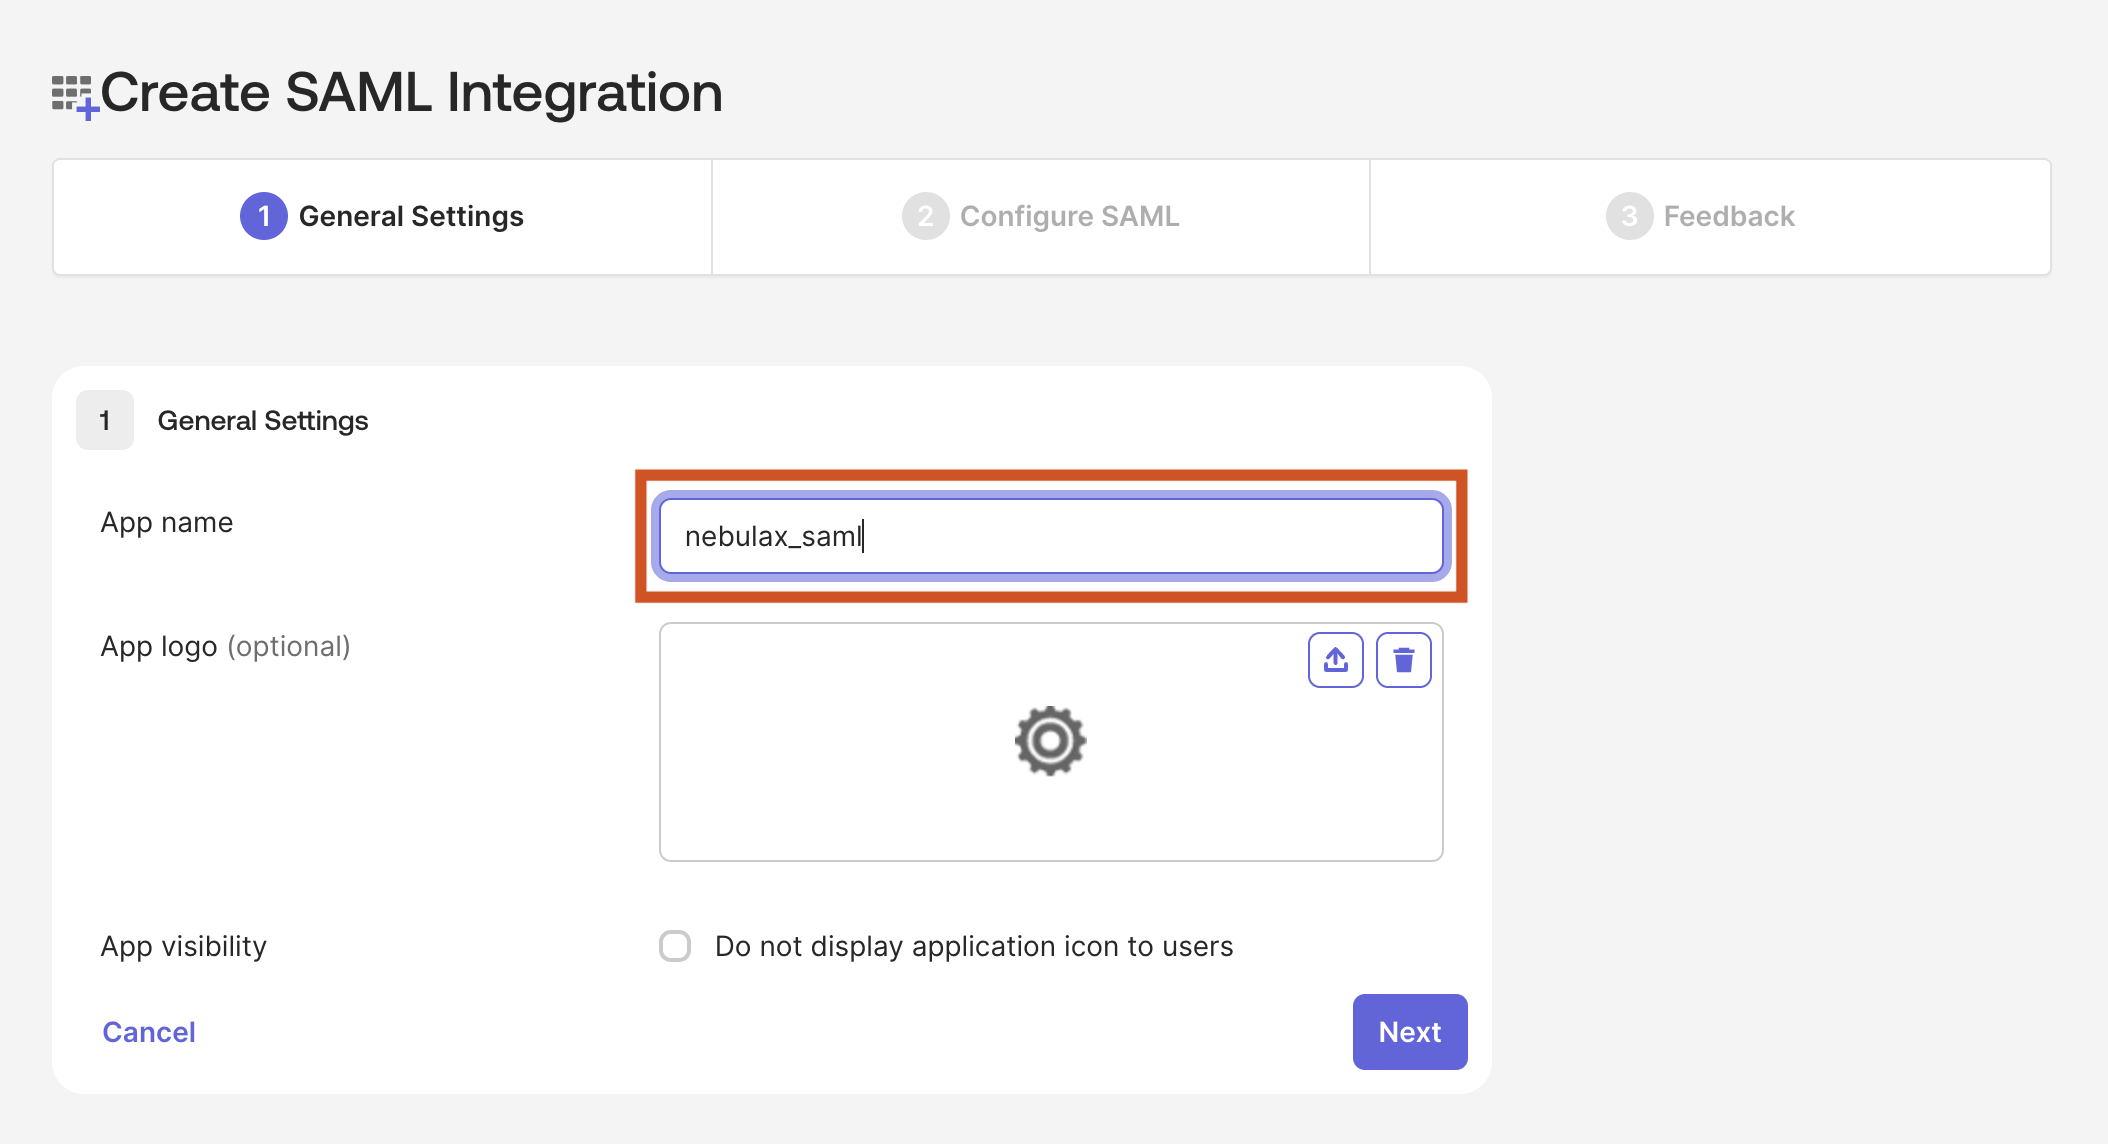
3. Find the XEIZE SAML values
On the XEIZE SSO integration page, find and copy SAML ACS 회신 URL (SAML ACS reply URL) and SP 식별자 (엔티티 ID) (SP entity ID).
4. Configure SAML in Okta
Enter the values copied from XEIZE on the Okta SAML settings screen.
| Okta setting | XEIZE setting |
|---|---|
| Single sign-on URL | SAML ACS 회신 URL (SAML ACS reply URL) |
| Audience URI (SP Entity ID) | SP 식별자 (엔티티 ID) (SP entity ID) |
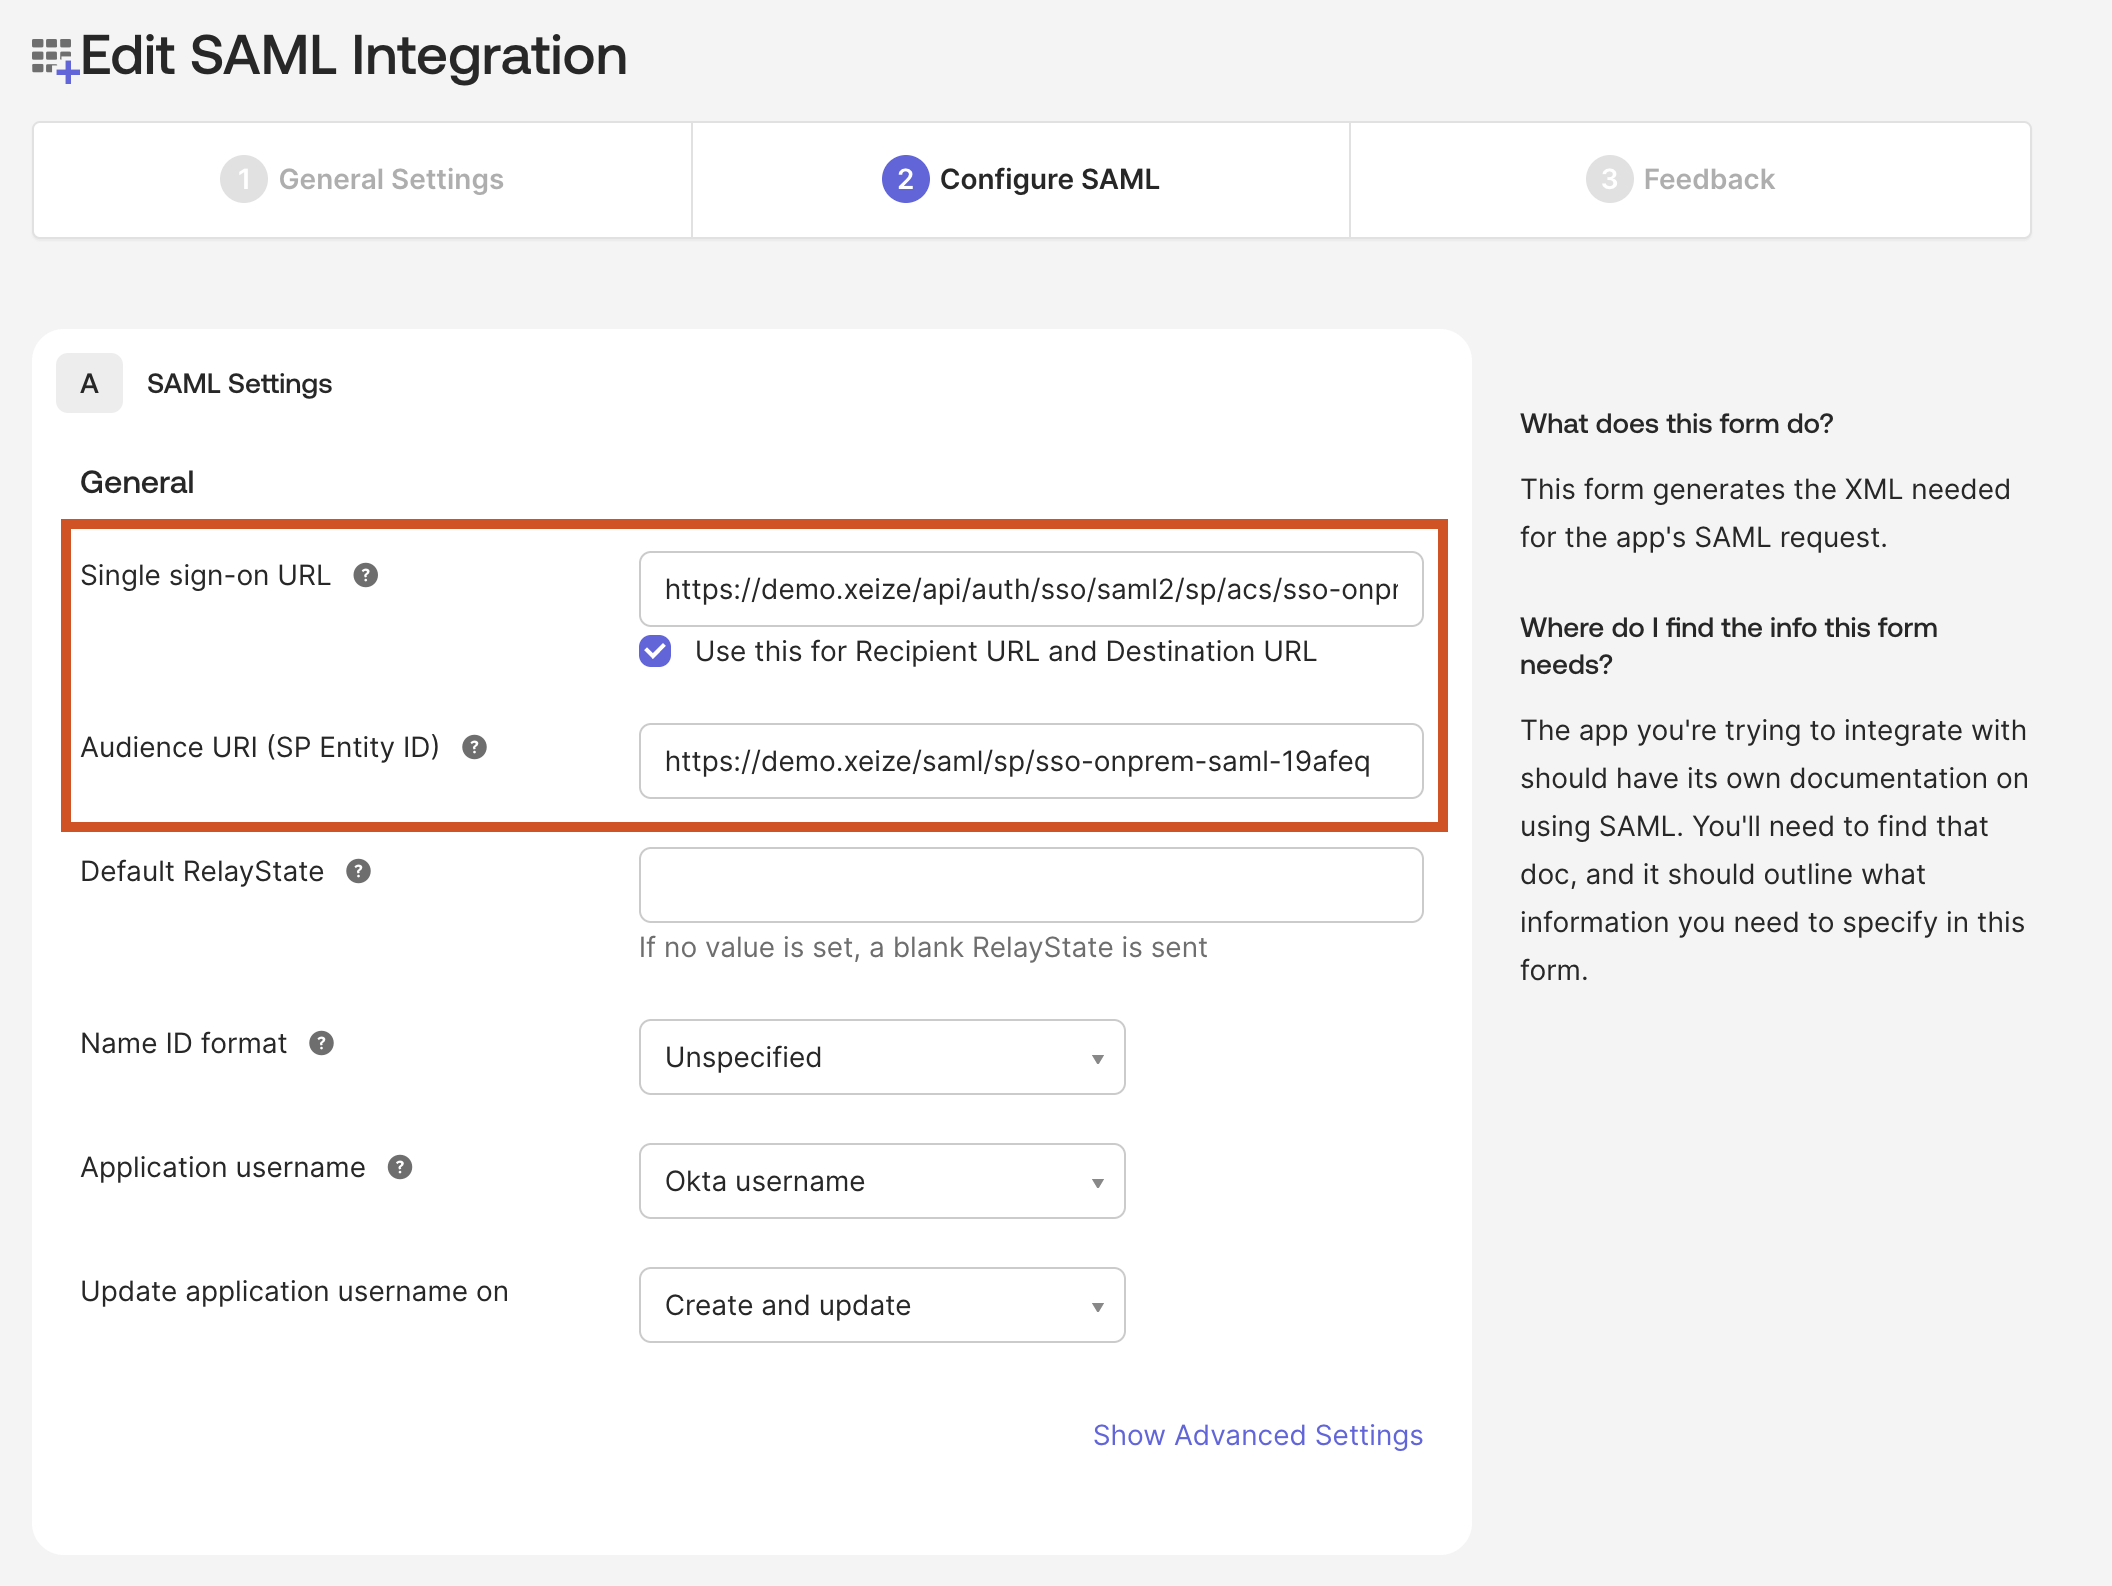
Set other fields as required by your organization's policies. Click Next, then Finish to complete registration.
5. Copy the IdP Metadata URL
After registering the SAML app, copy the generated Metadata URL.
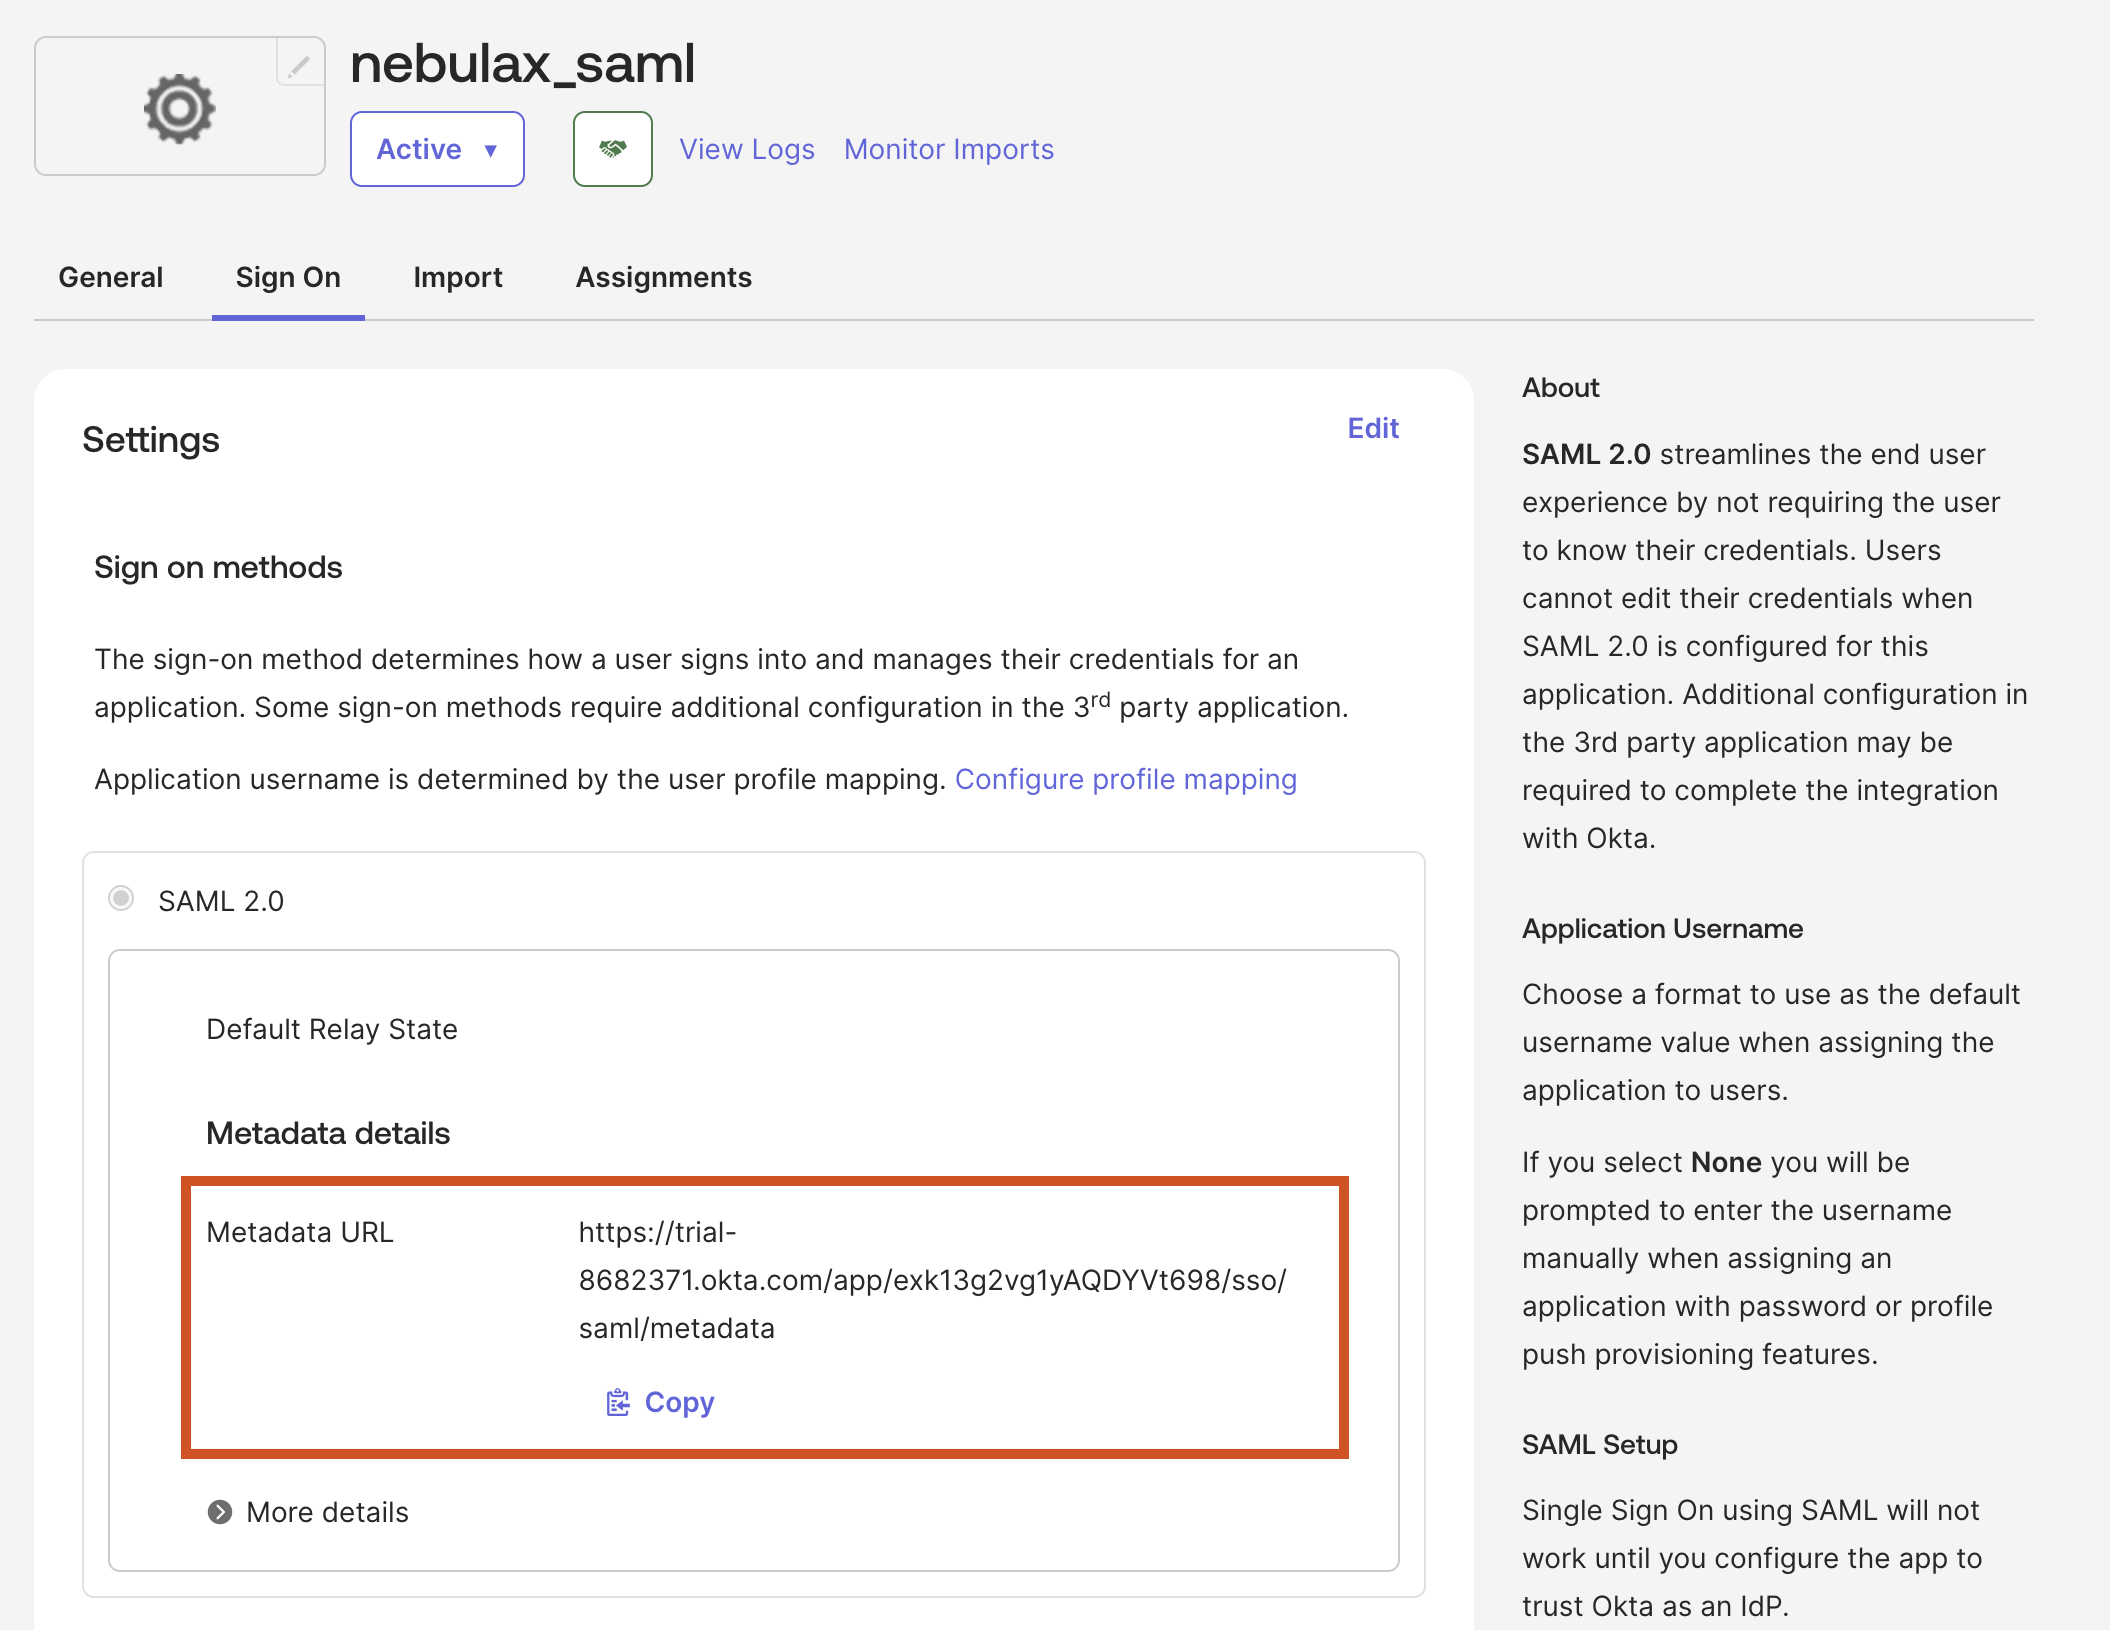
6. Register the Metadata URL in XEIZE
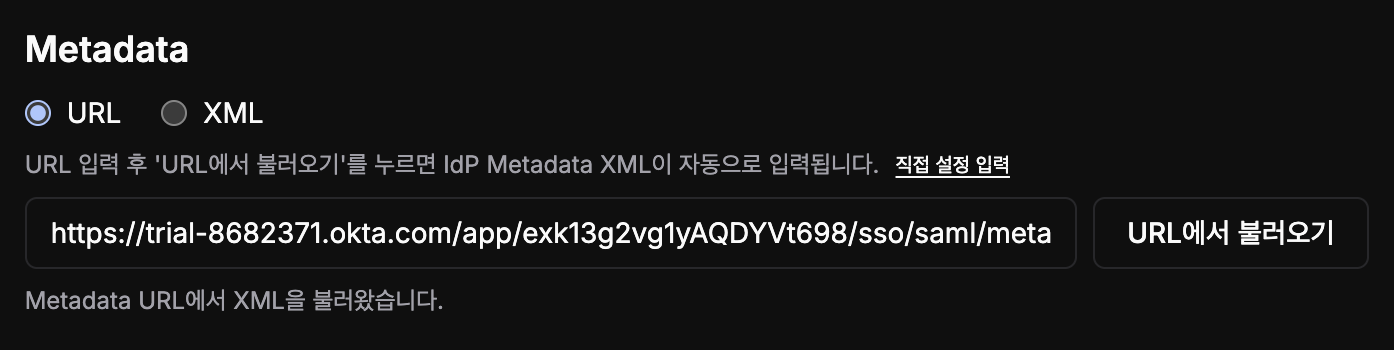
Paste the copied Metadata URL into XEIZE's Metadata URL field, then click URL에서 불러오기 (load from URL).
The required information is parsed automatically from the Metadata URL.
7. Assign users
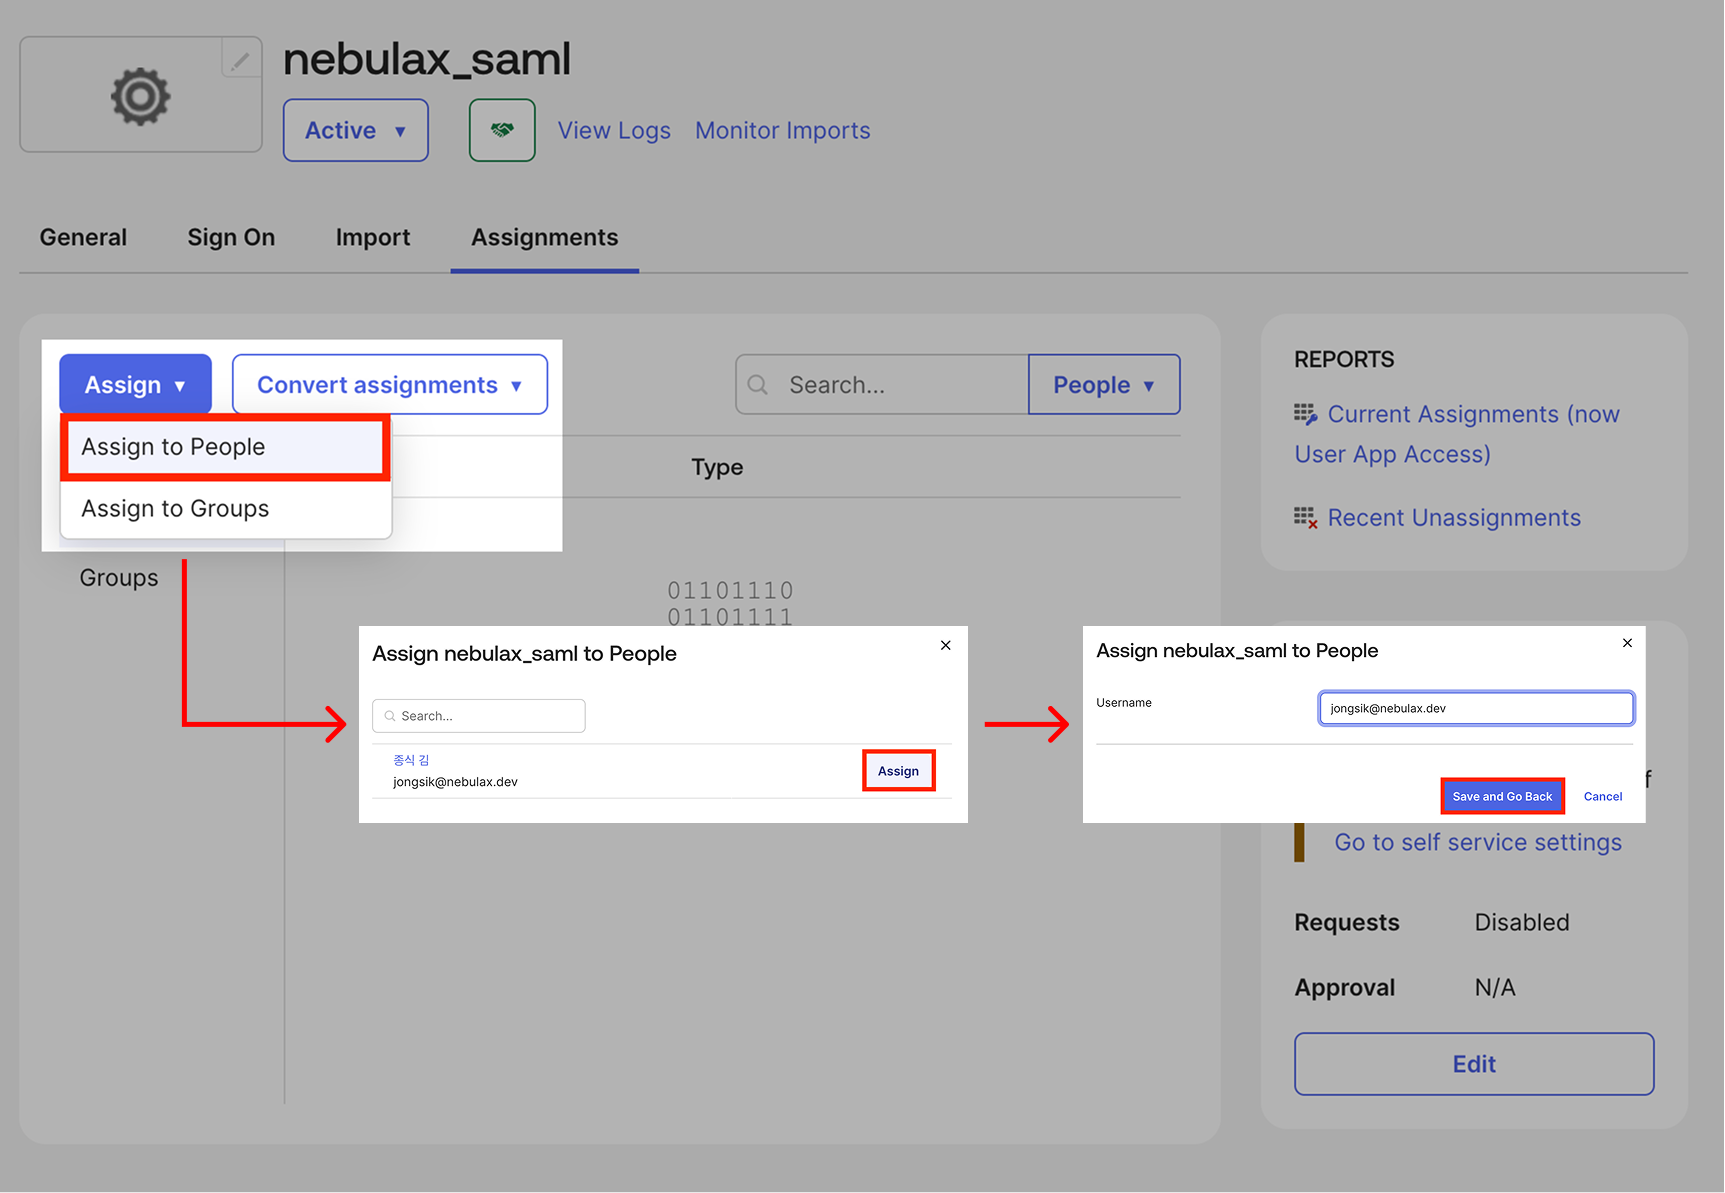
In the Okta SAML app's Assignments tab, select Assign > Assign to People.
Select the accounts that should have access through SAML, then click Assign to add them.
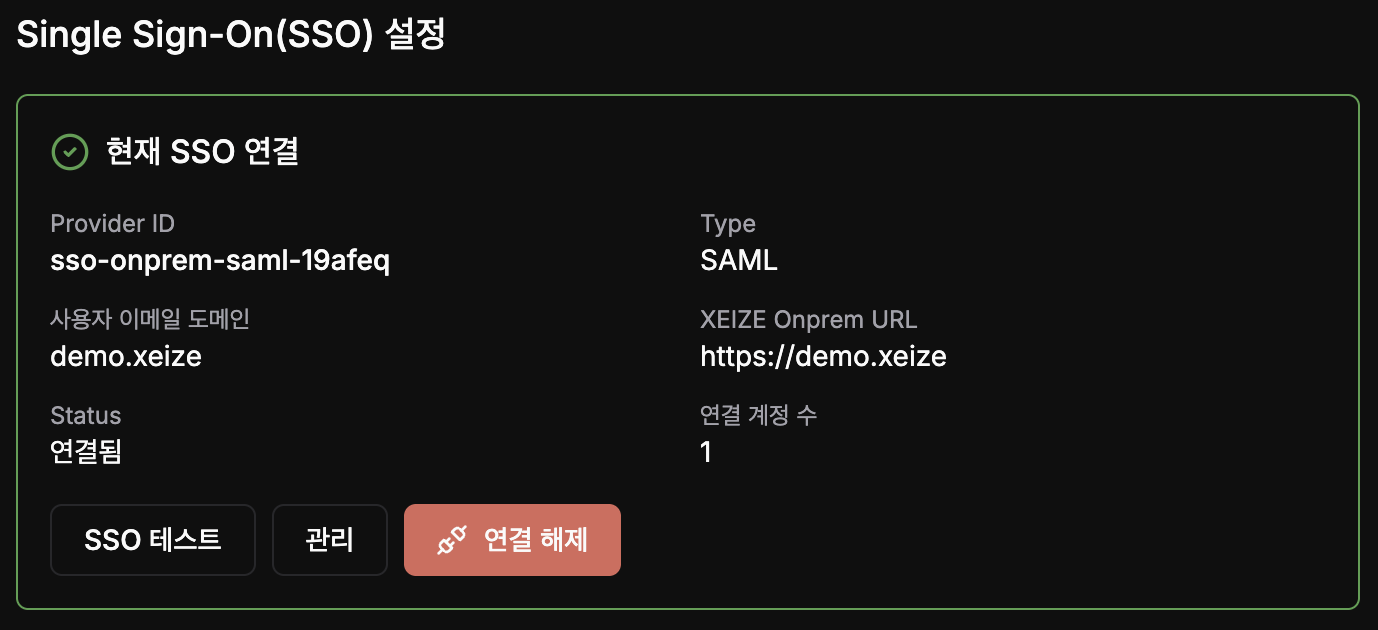
8. Test sign-in
After setup, check that SSO sign-in works.
Notes
If SSO sign-in does not work, check the following:
- The user is assigned to the Okta app.
- The
Metadata URLregistered in XEIZE is correct. SAML ACS 회신 URL(SAML ACS reply URL) is entered exactly in Okta'sSingle sign-on URL.SP 식별자 (엔티티 ID)(SP entity ID) is entered exactly in Okta'sAudience URI (SP Entity ID).- The user's email or identifier matches the XEIZE account information.
For more about Okta SAML configuration, see Okta SAML app integrations.