
1. Create an OAuth client
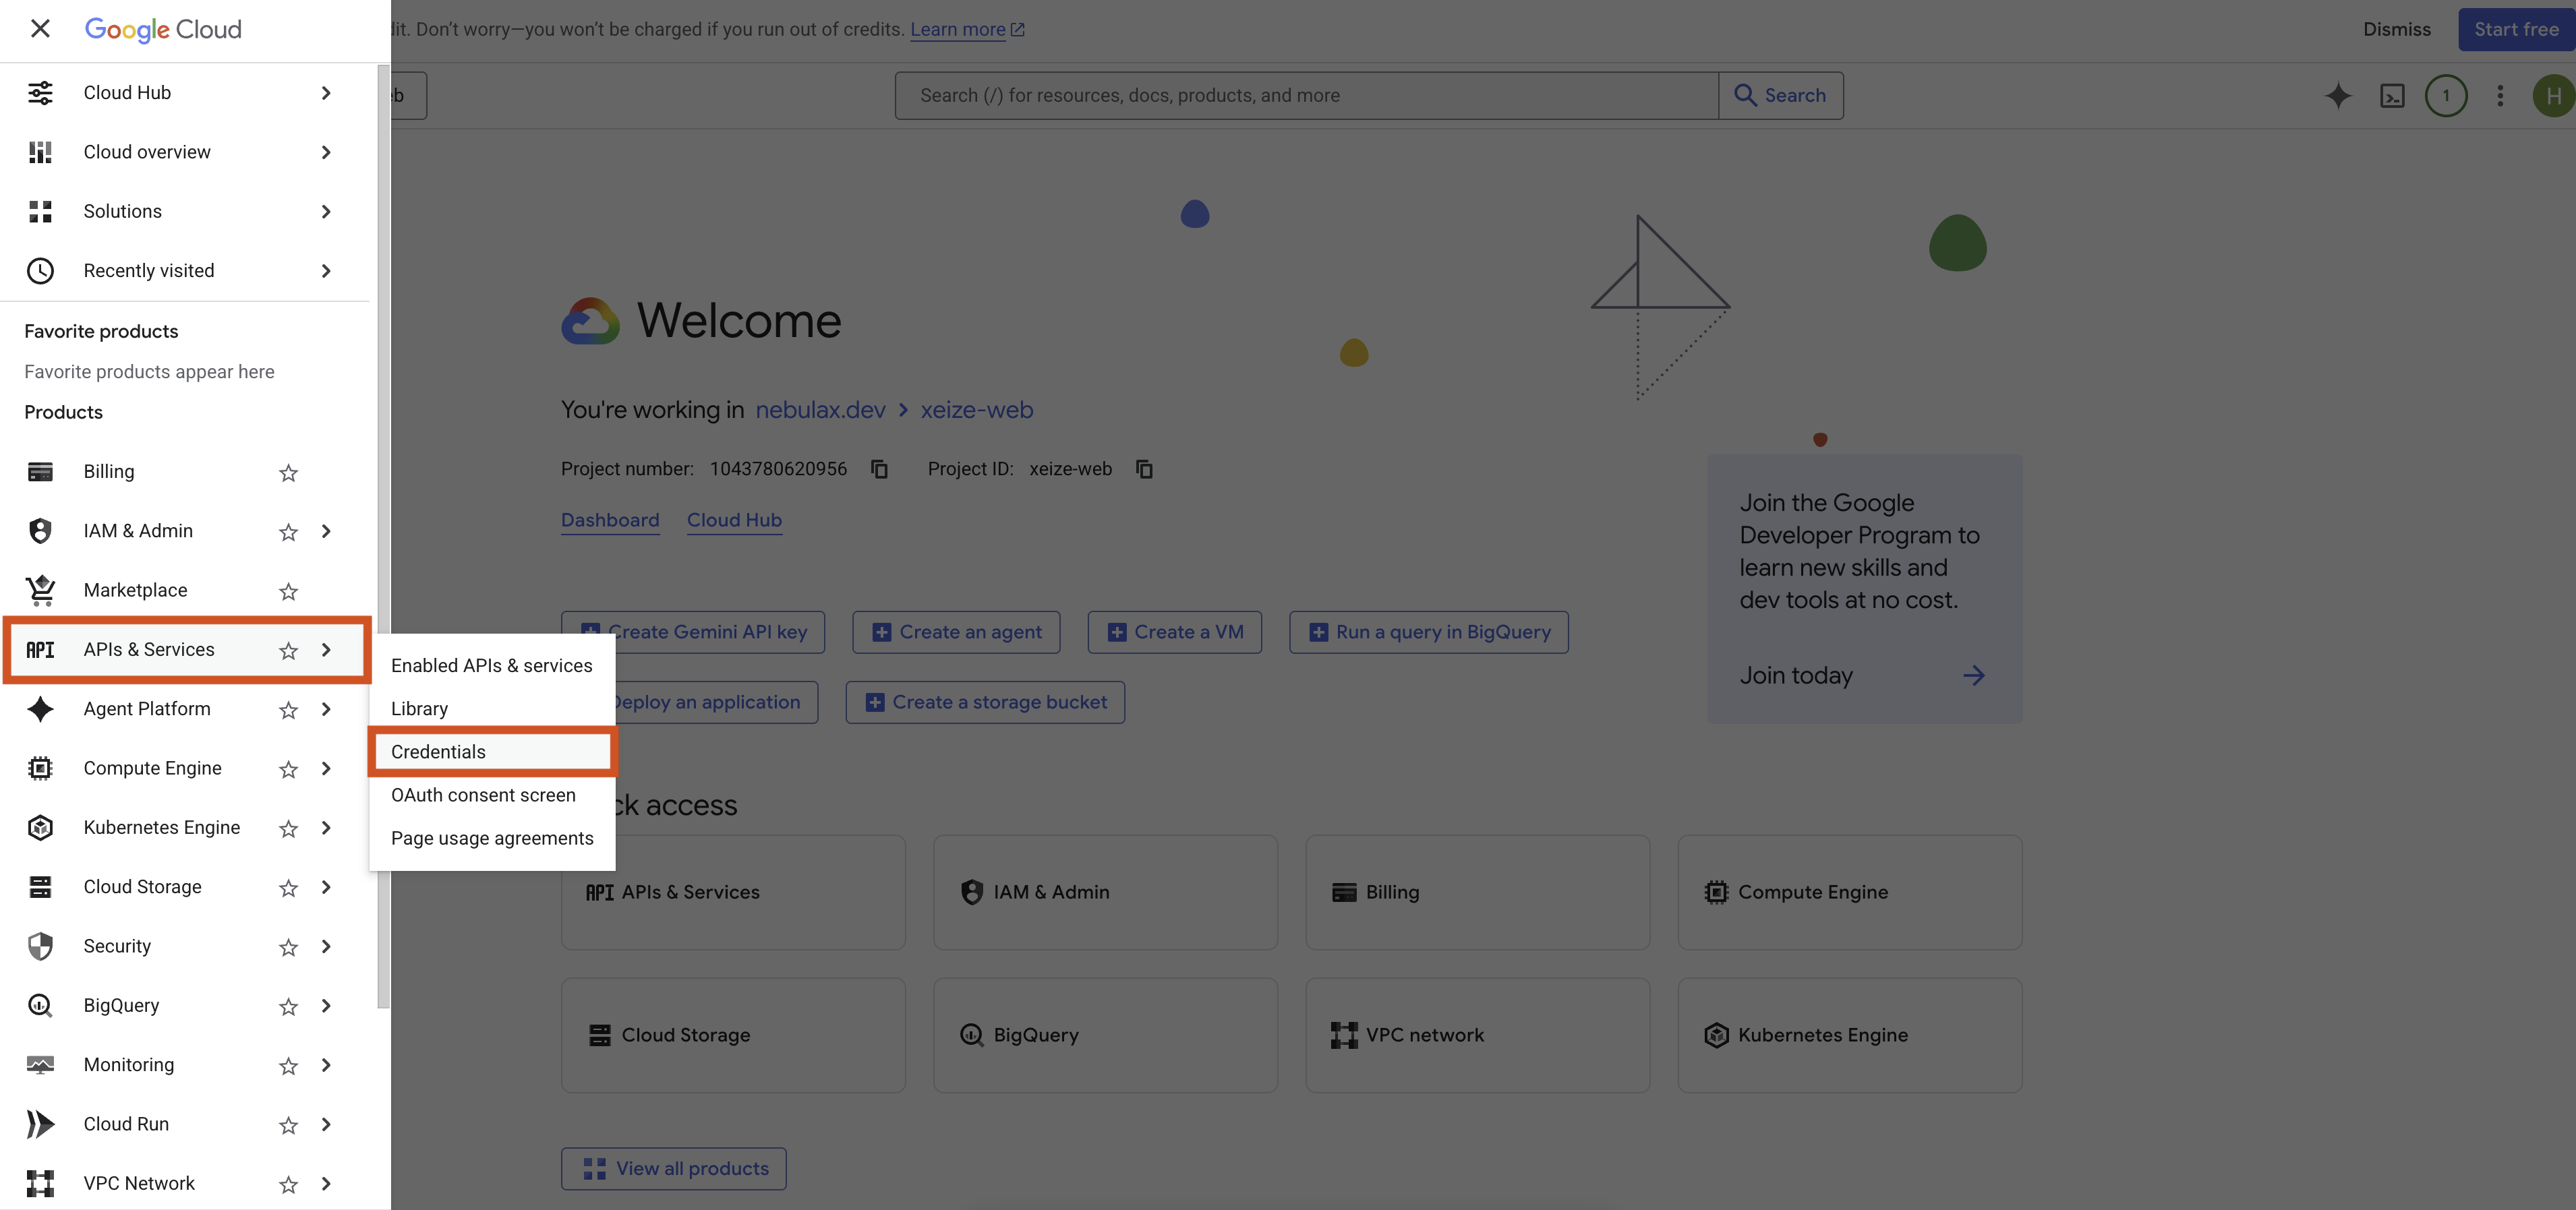
Sign in to Google Cloud Console and open APIs & Services > Credentials from the left sidebar.
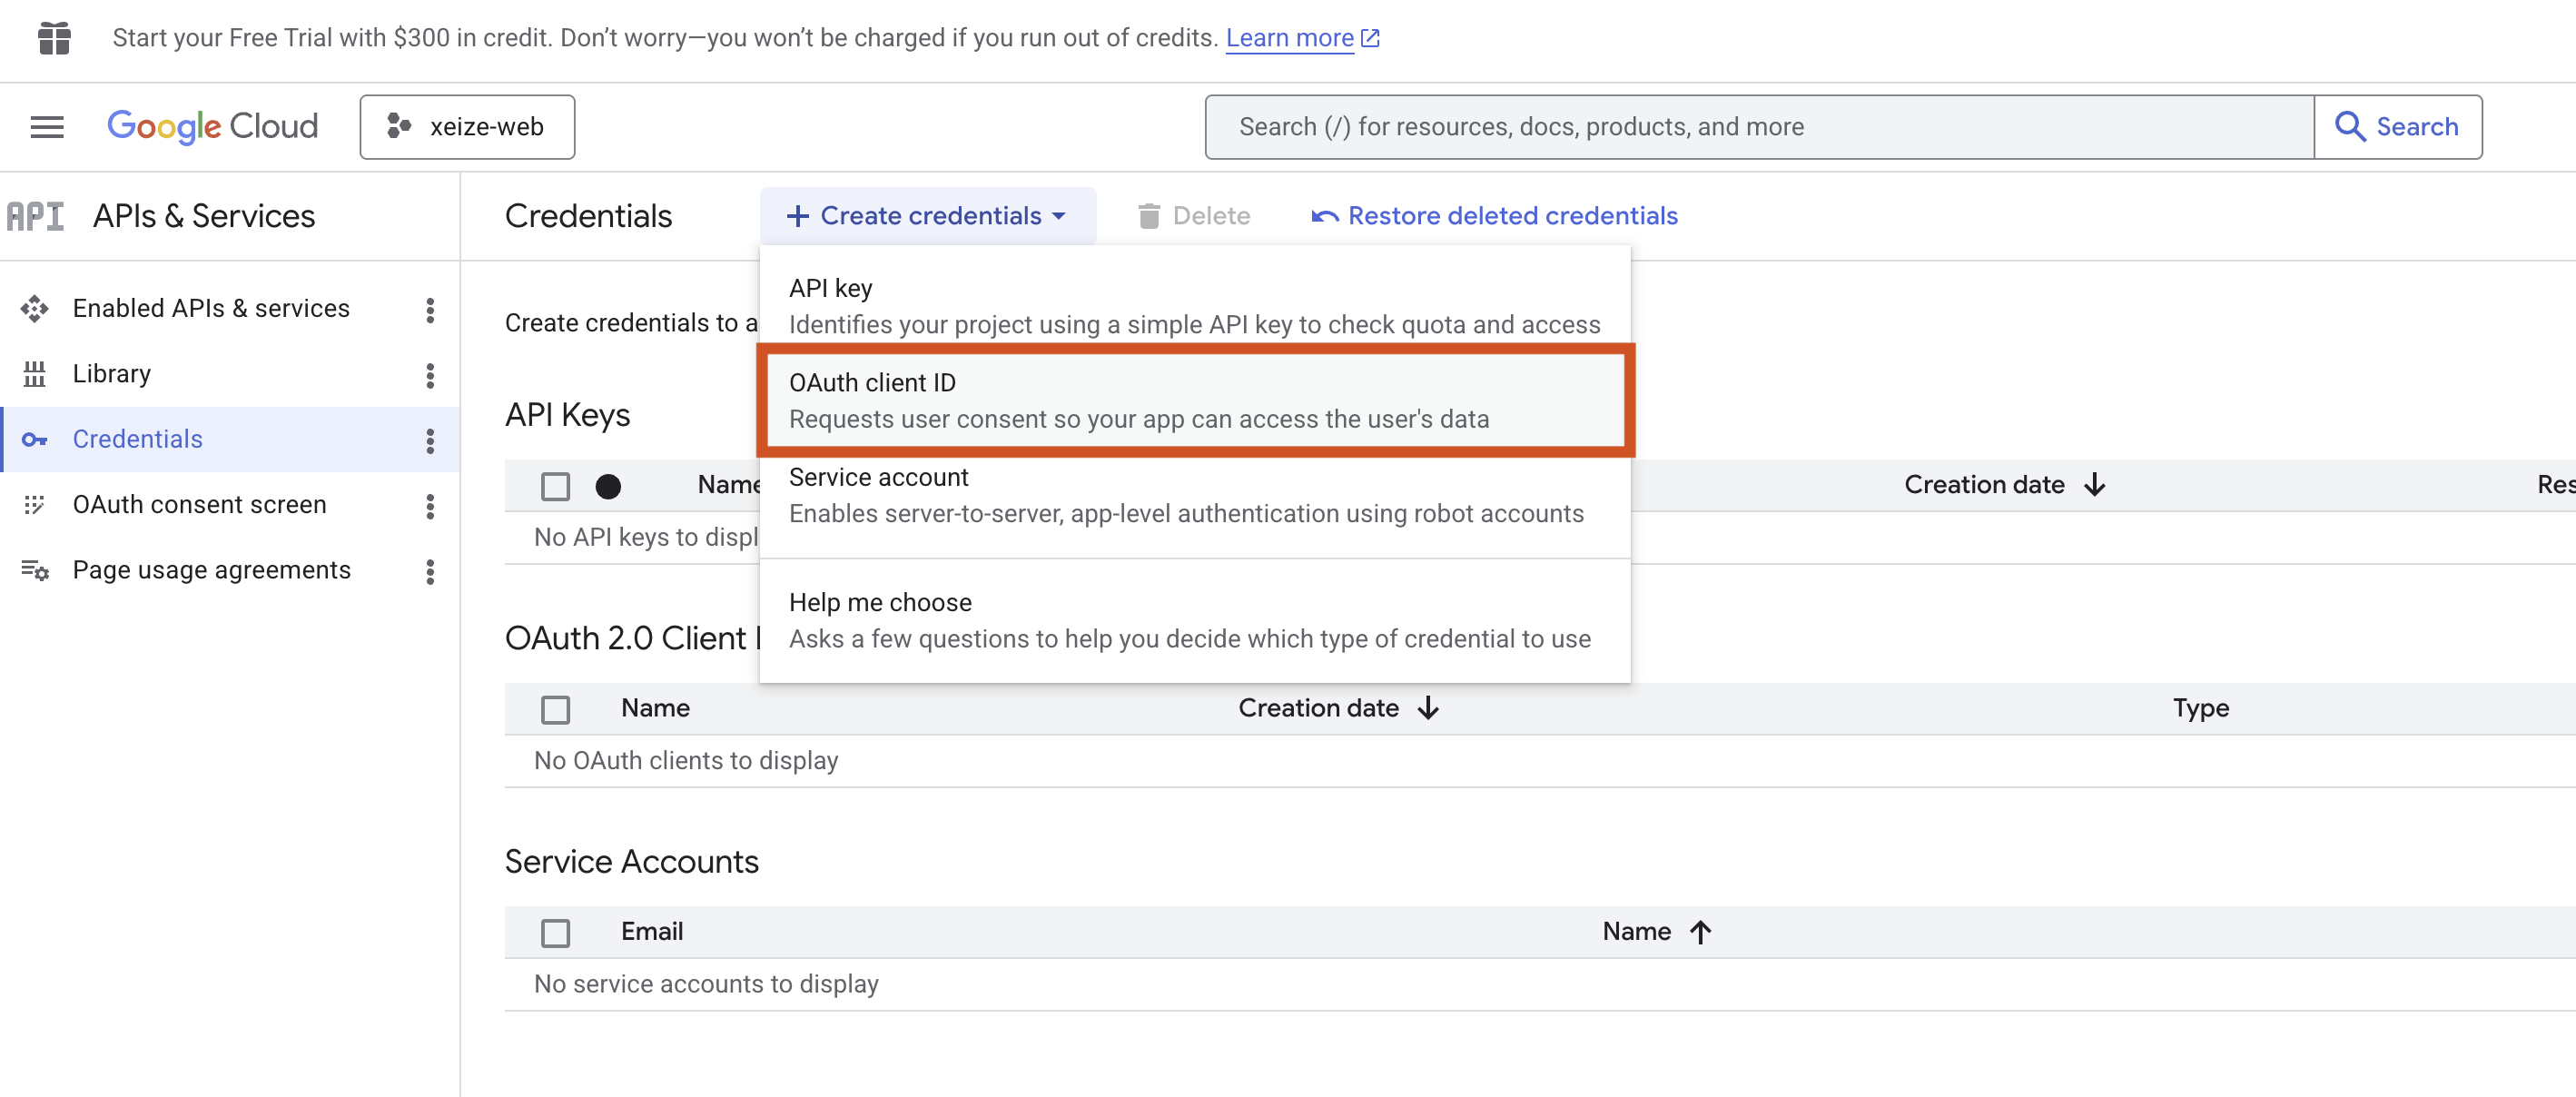
Click Create credentials > OAuth client ID to start creating the application.
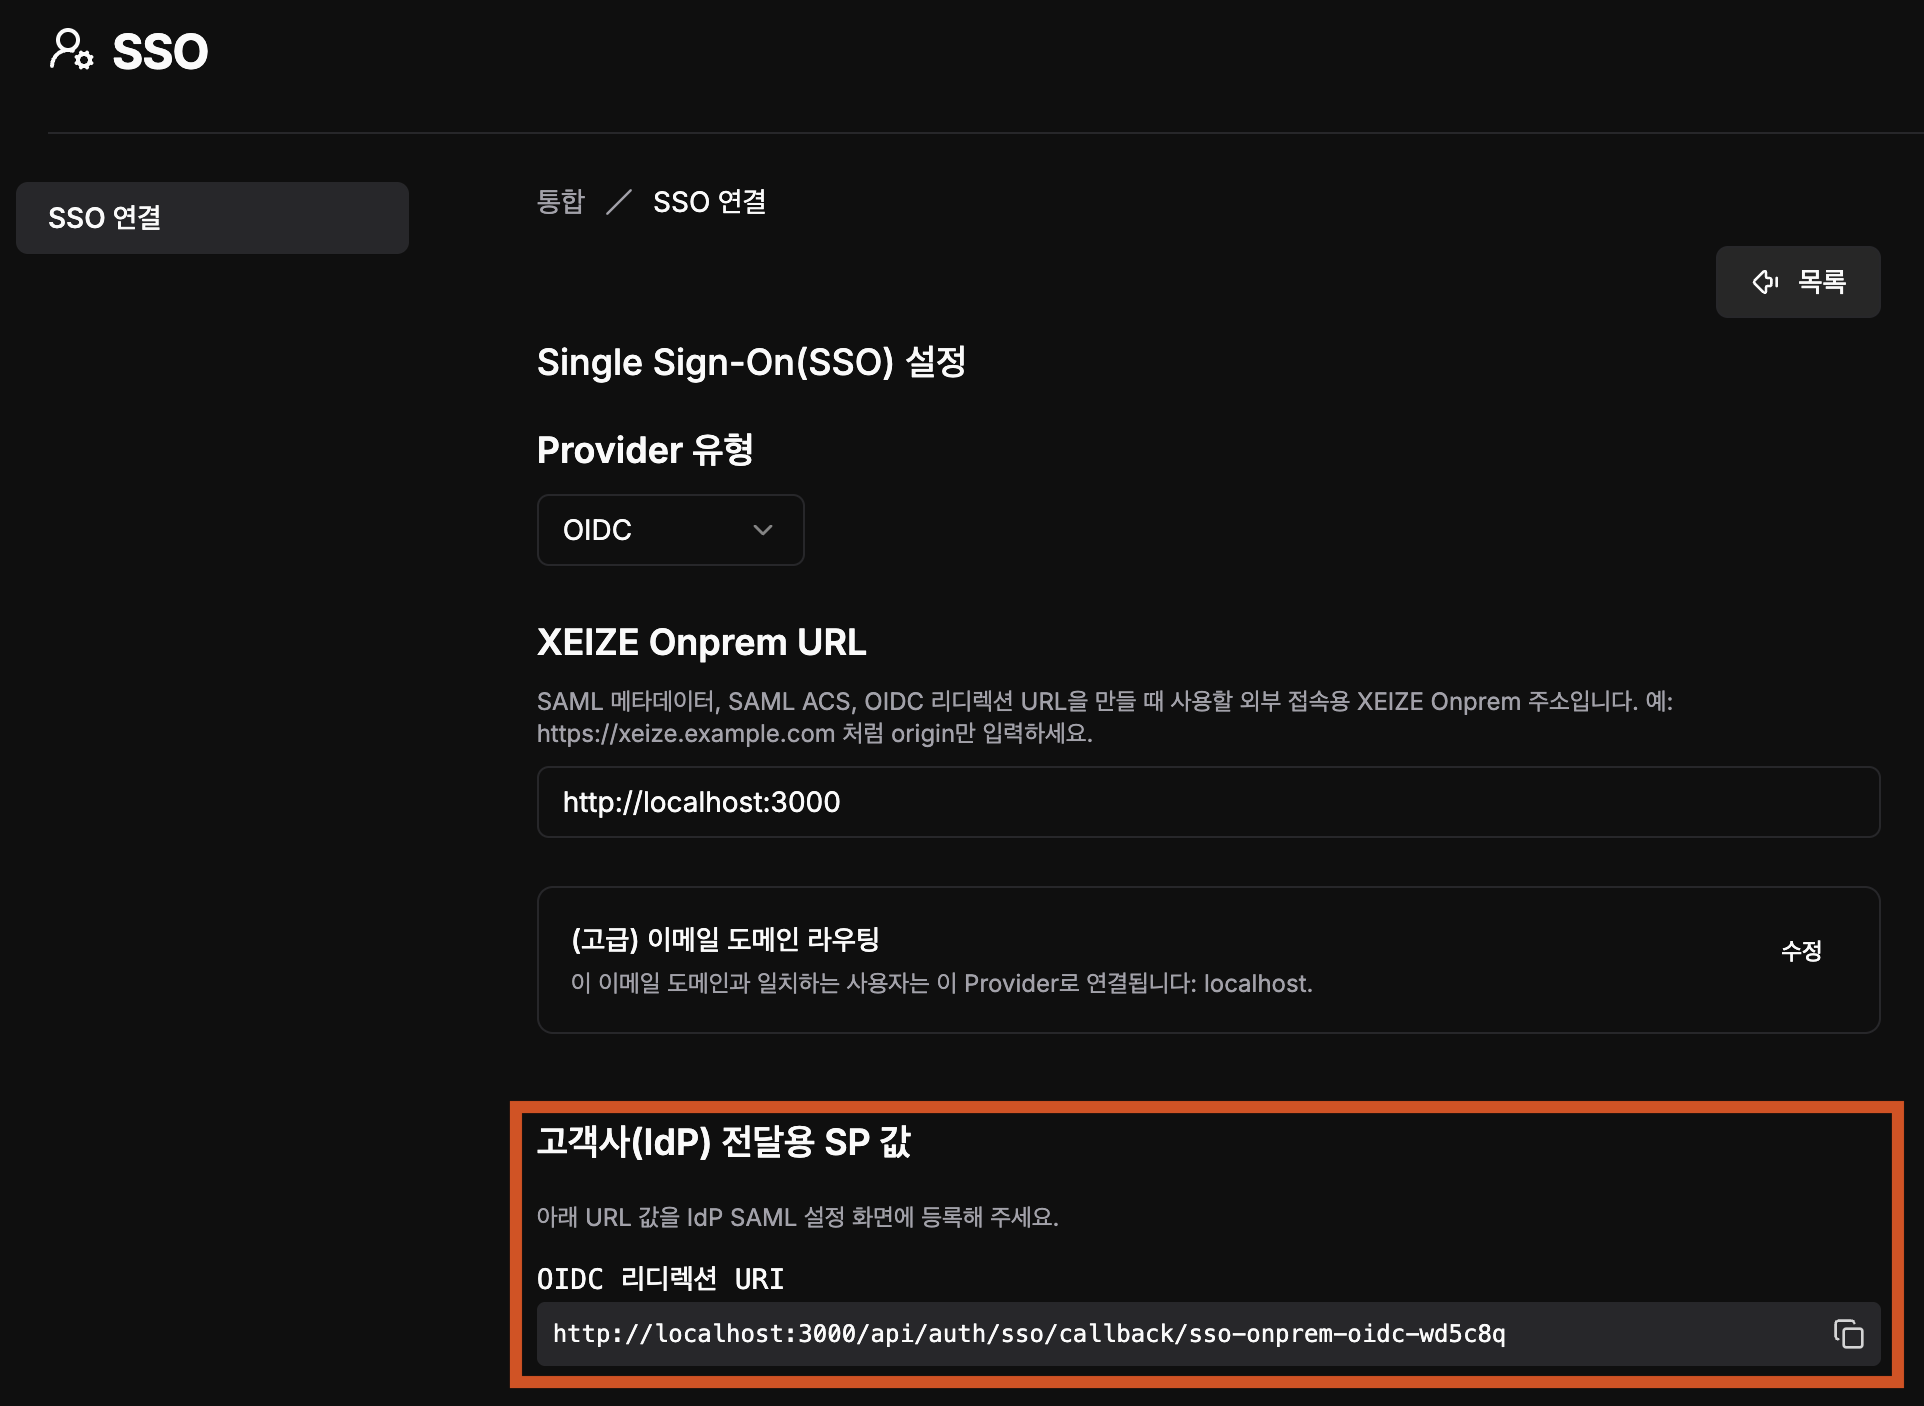
2. Find the XEIZE OIDC information
In the XEIZE SSO integration settings, find and copy OIDC 리디렉션 URI (OIDC redirect URI).
3. Configure the Google OAuth client
Enter the values copied from XEIZE in the Google OAuth client settings.
| Google setting | Value |
|---|---|
| Application type | Web application |
| Name | The application name to use for XEIZE |
| Authorized redirect URIs | The OIDC redirect URI |
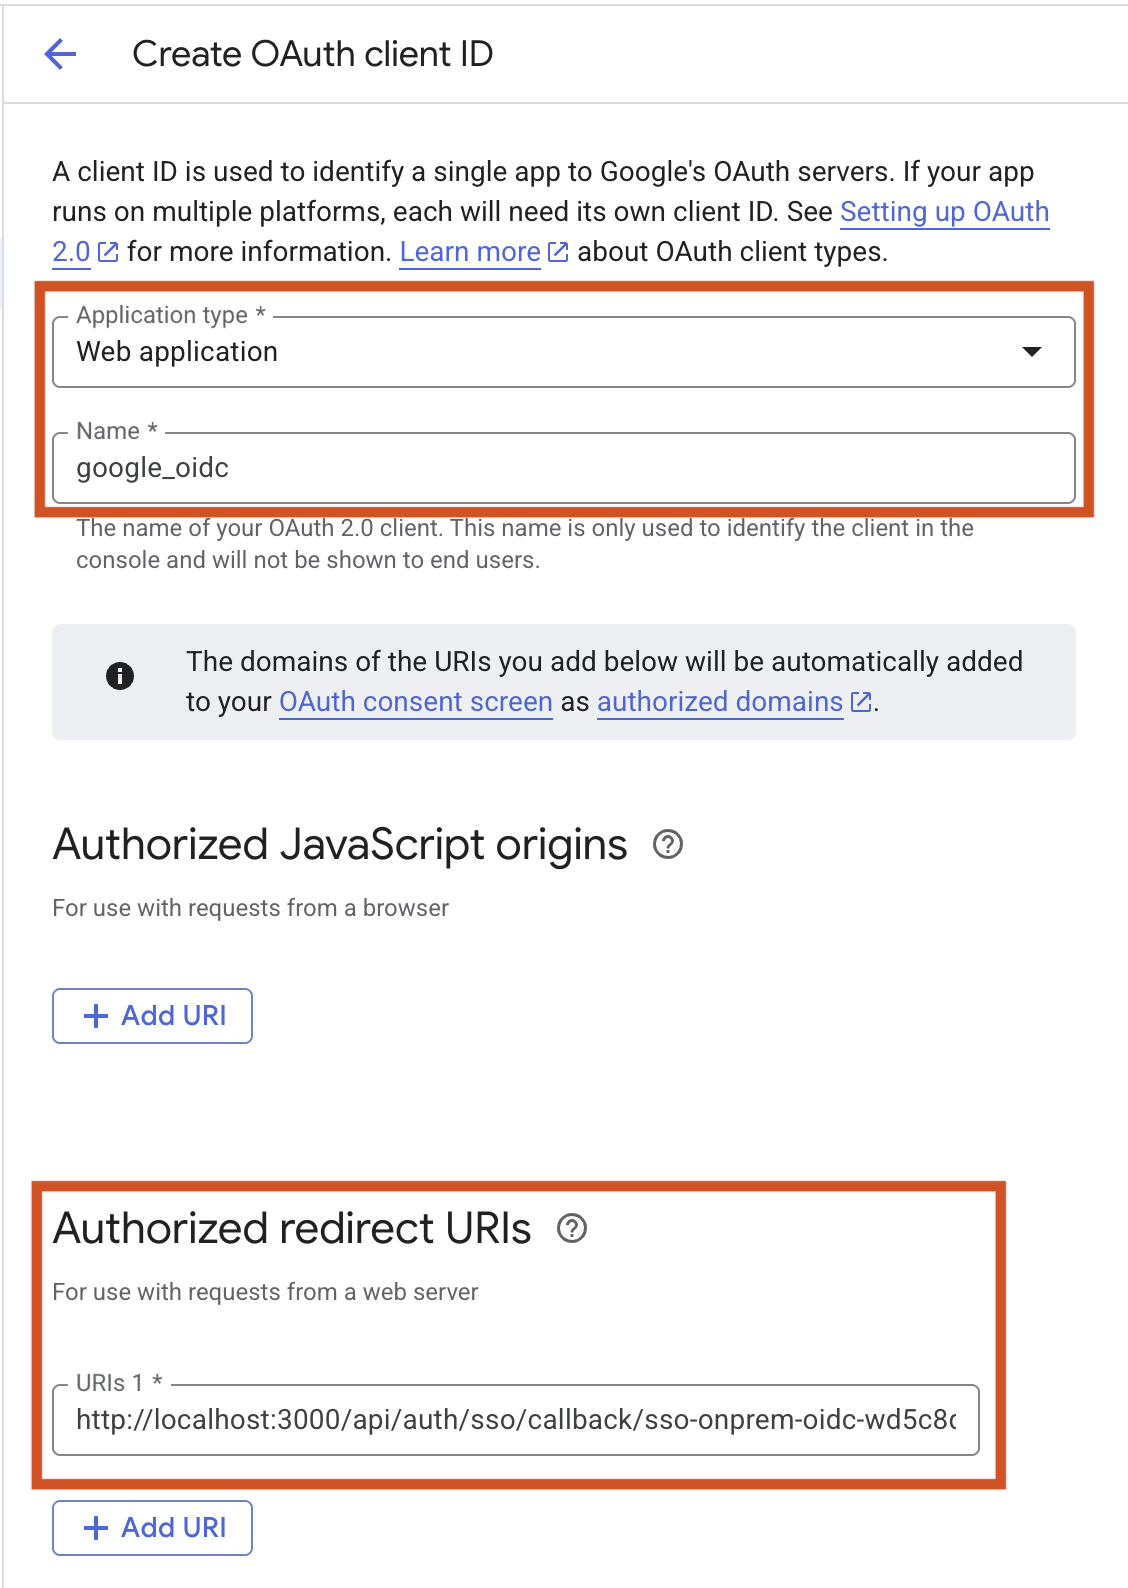
Click Create after entering the values.
4. Configure OIDC in XEIZE
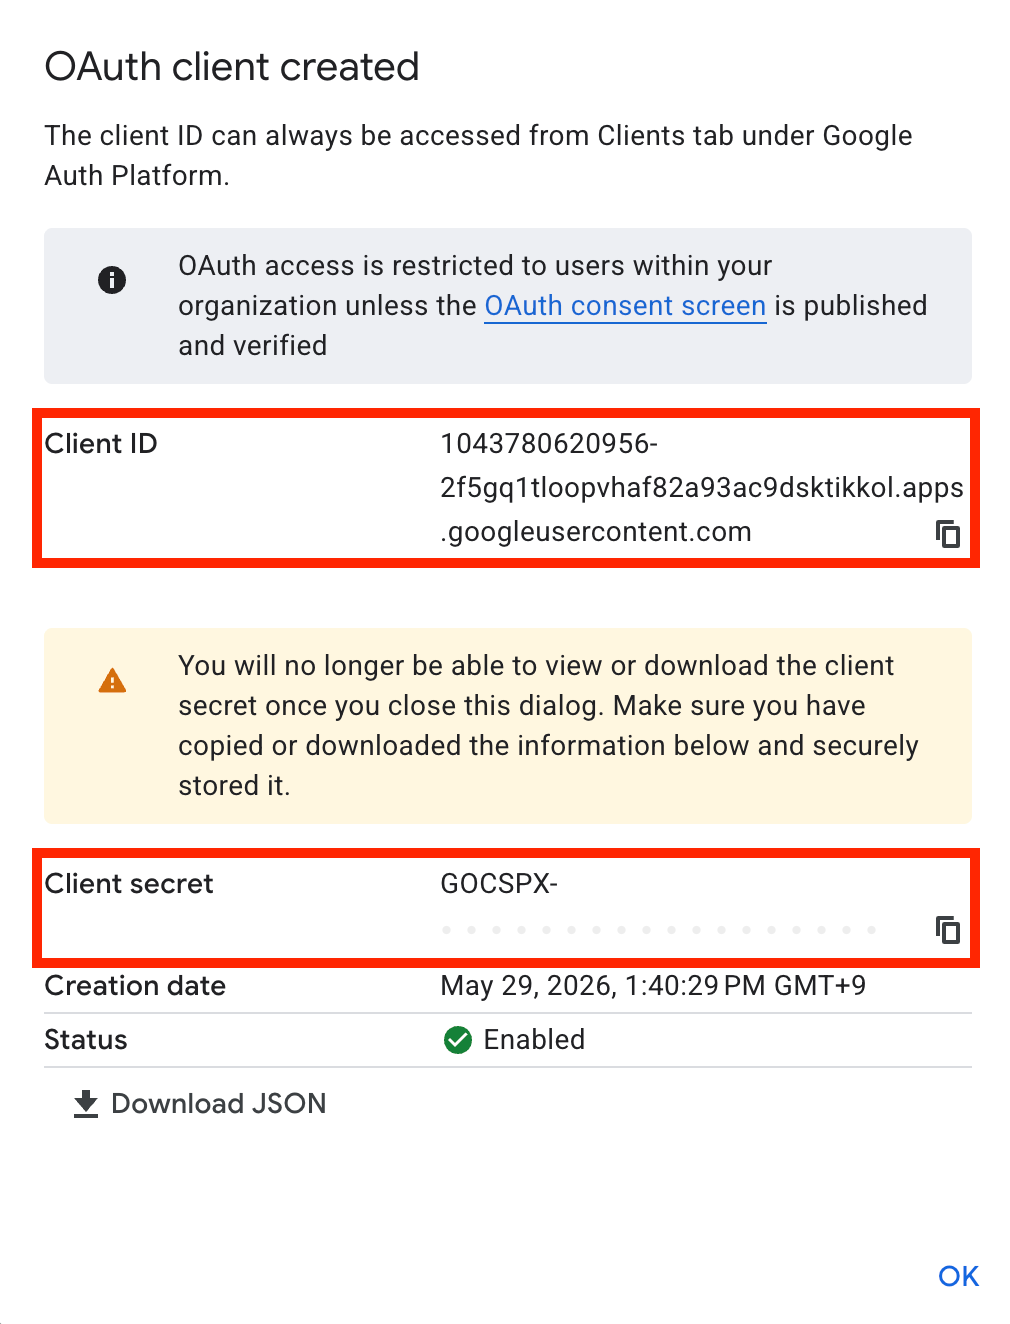
Copy the new OAuth client’s Client ID and Client Secret from Google Console.
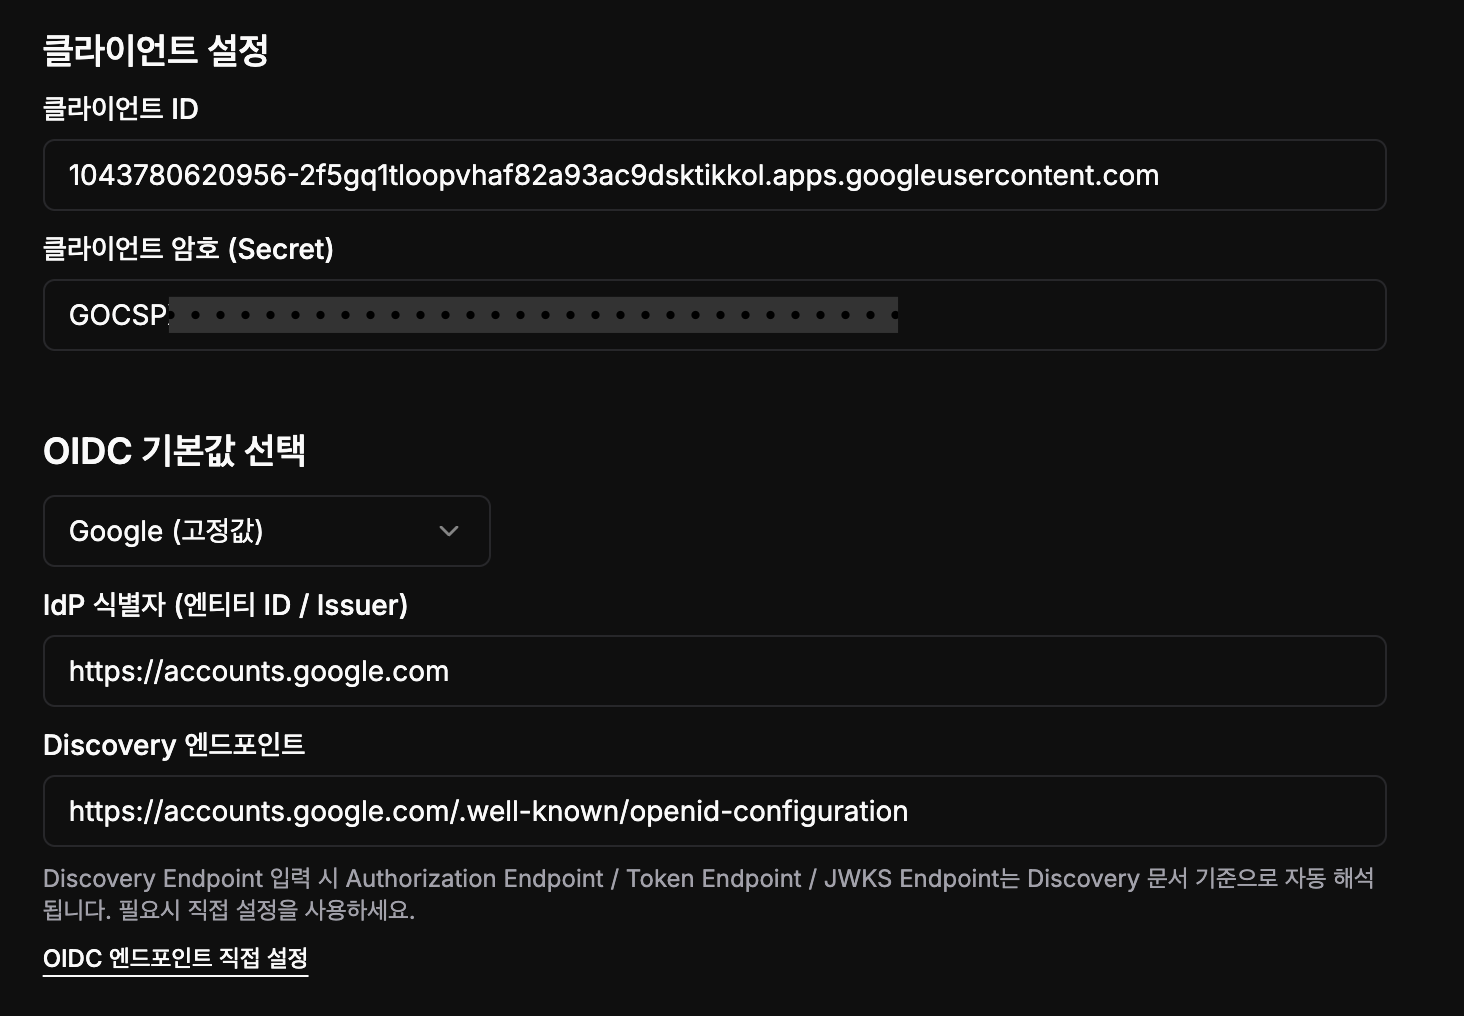
Enter them in 클라이언트 ID (client ID) and 클라이언트 암호 (Secret) (client secret) in the XEIZE SSO integration settings.
Select Google (고정값) (fixed values) in the OIDC preset selector. Keep Google’s fixed values unchanged.
5. Test sign-in
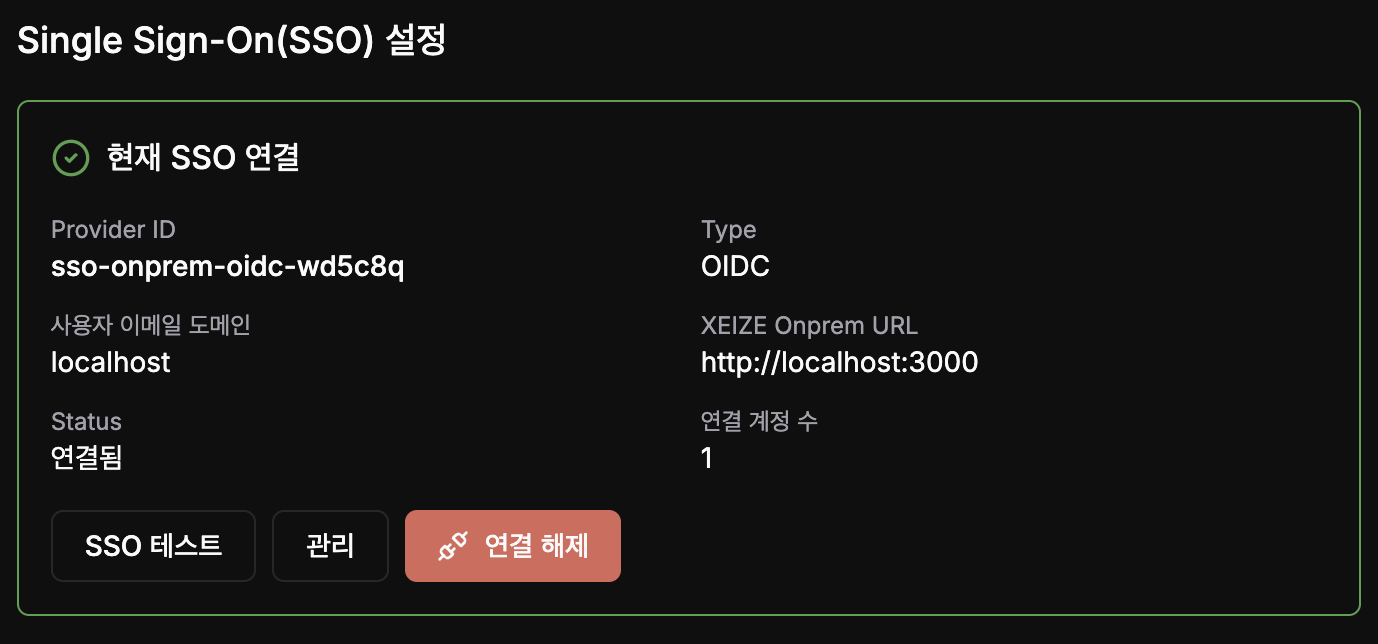
After completing the setup, check that SSO sign-in works.
Reference
If SSO sign-in does not work, check the following:
- The Google OAuth client’s
Authorized redirect URIsmust match the XEIZE OIDC redirect URI. - Verify the client ID and client secret entered in XEIZE.
- Check that the user’s email address or identifier matches their XEIZE account information.
For more information about Google OIDC, see OpenID Connect.