
This guide explains how to configure OIDC SSO with Okta's org authorization server. Use the domain and account details for your own environment instead of the example values in the screenshots.
1. Create an Okta app integration
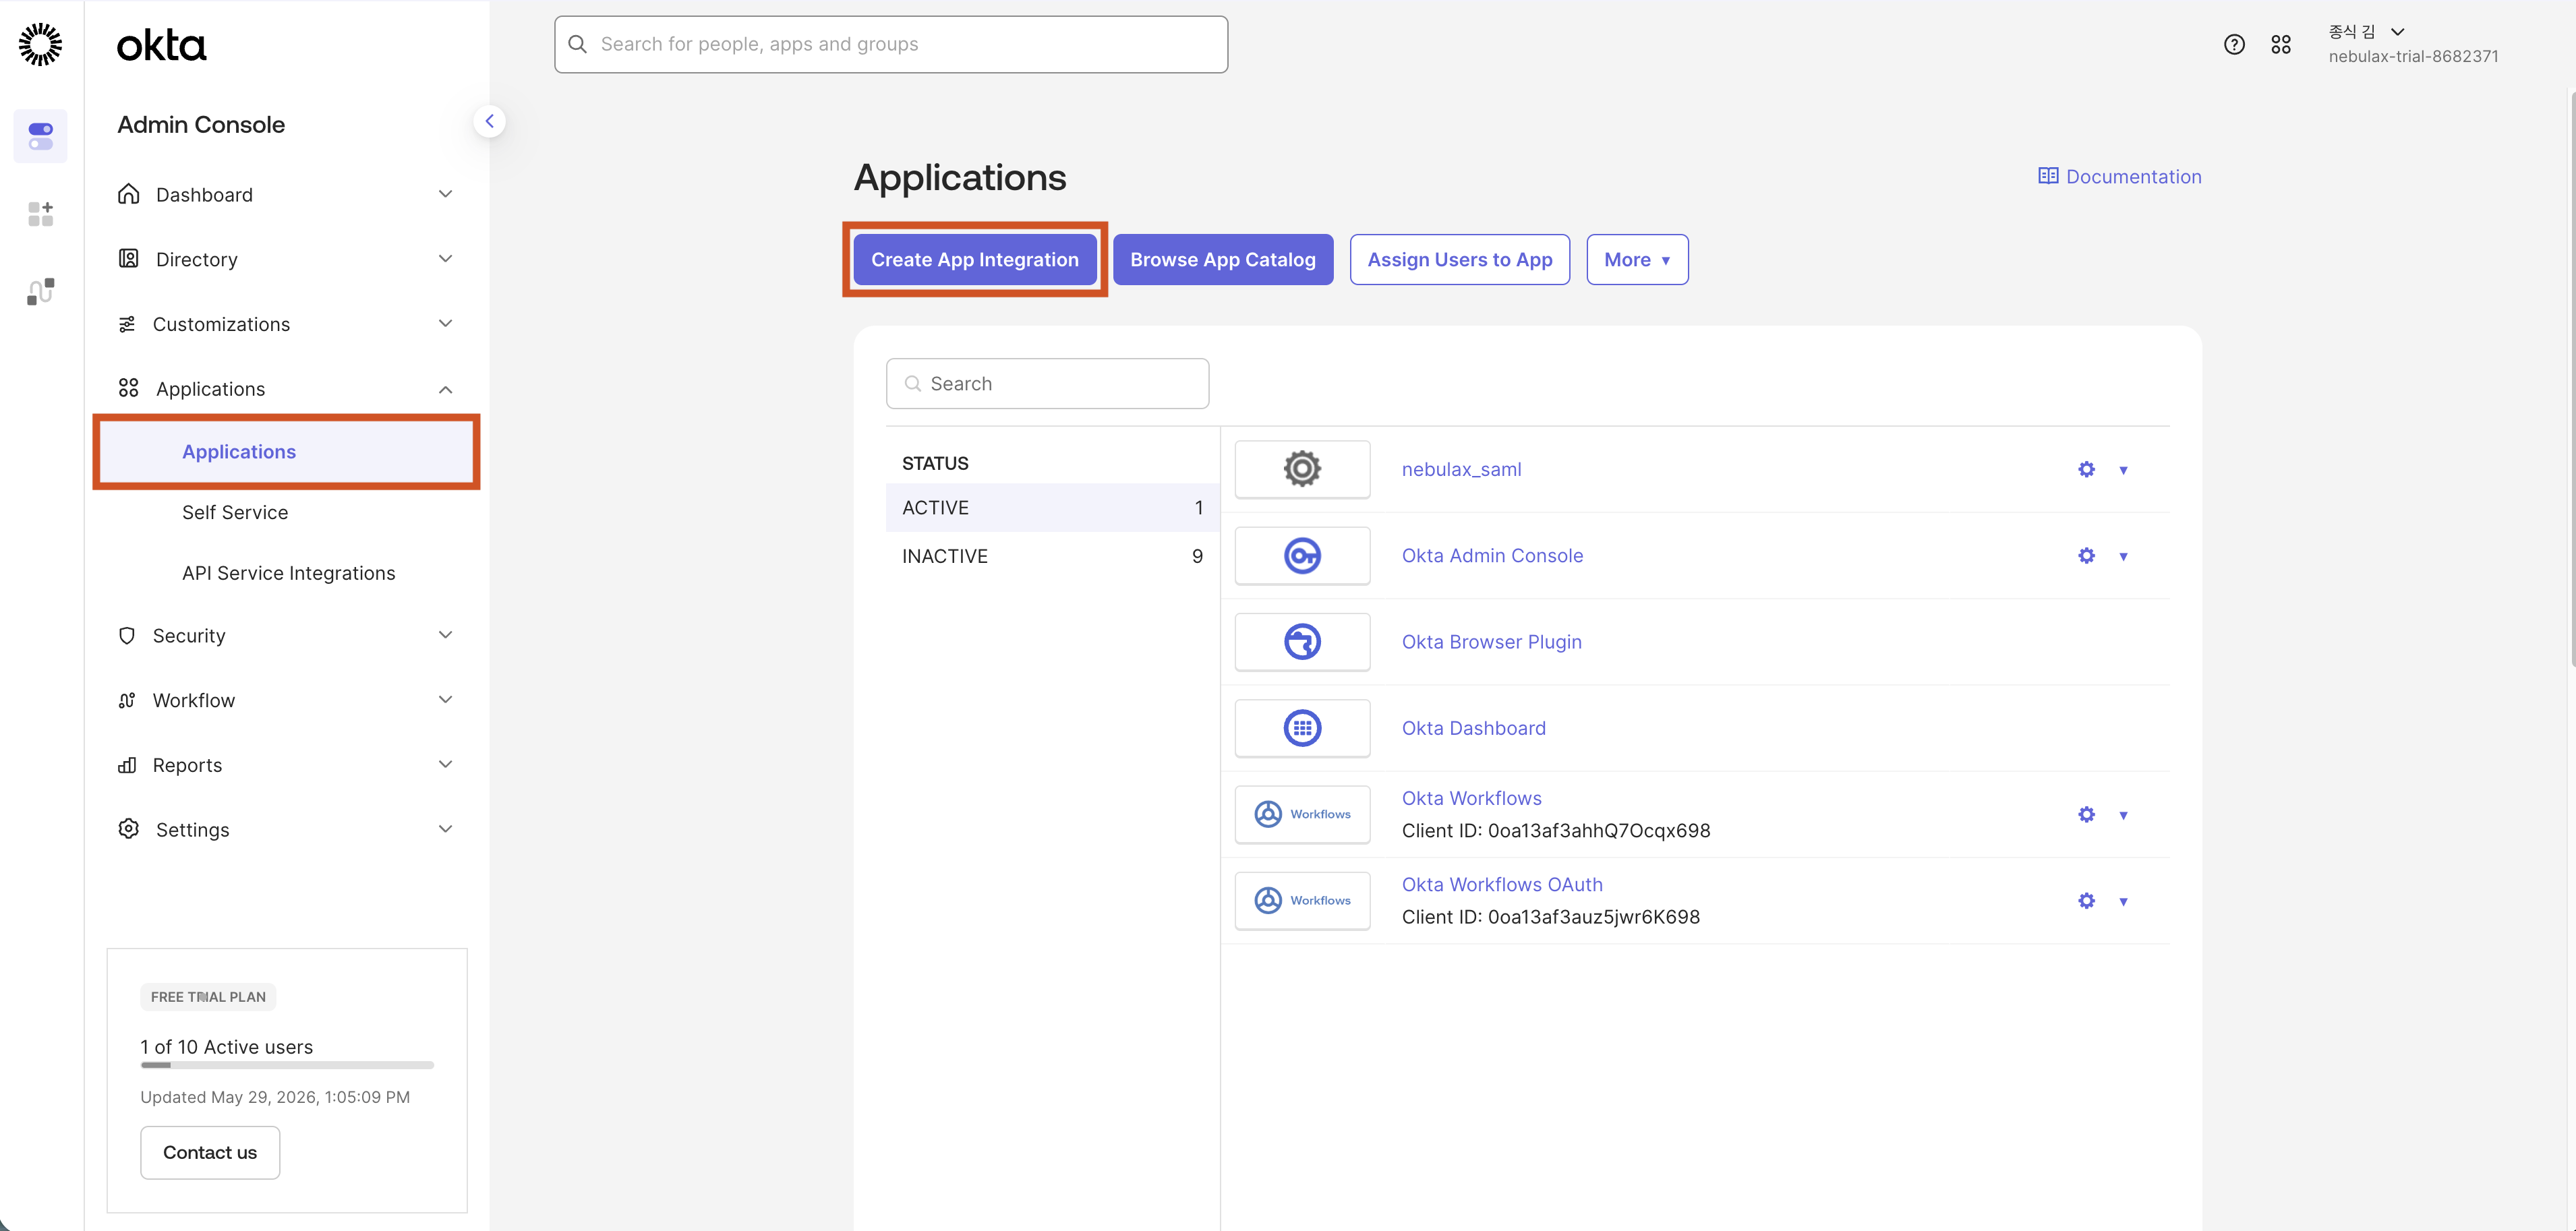
Sign in to Okta, go to Admin Console > Applications > Applications, and select Create App Integration.
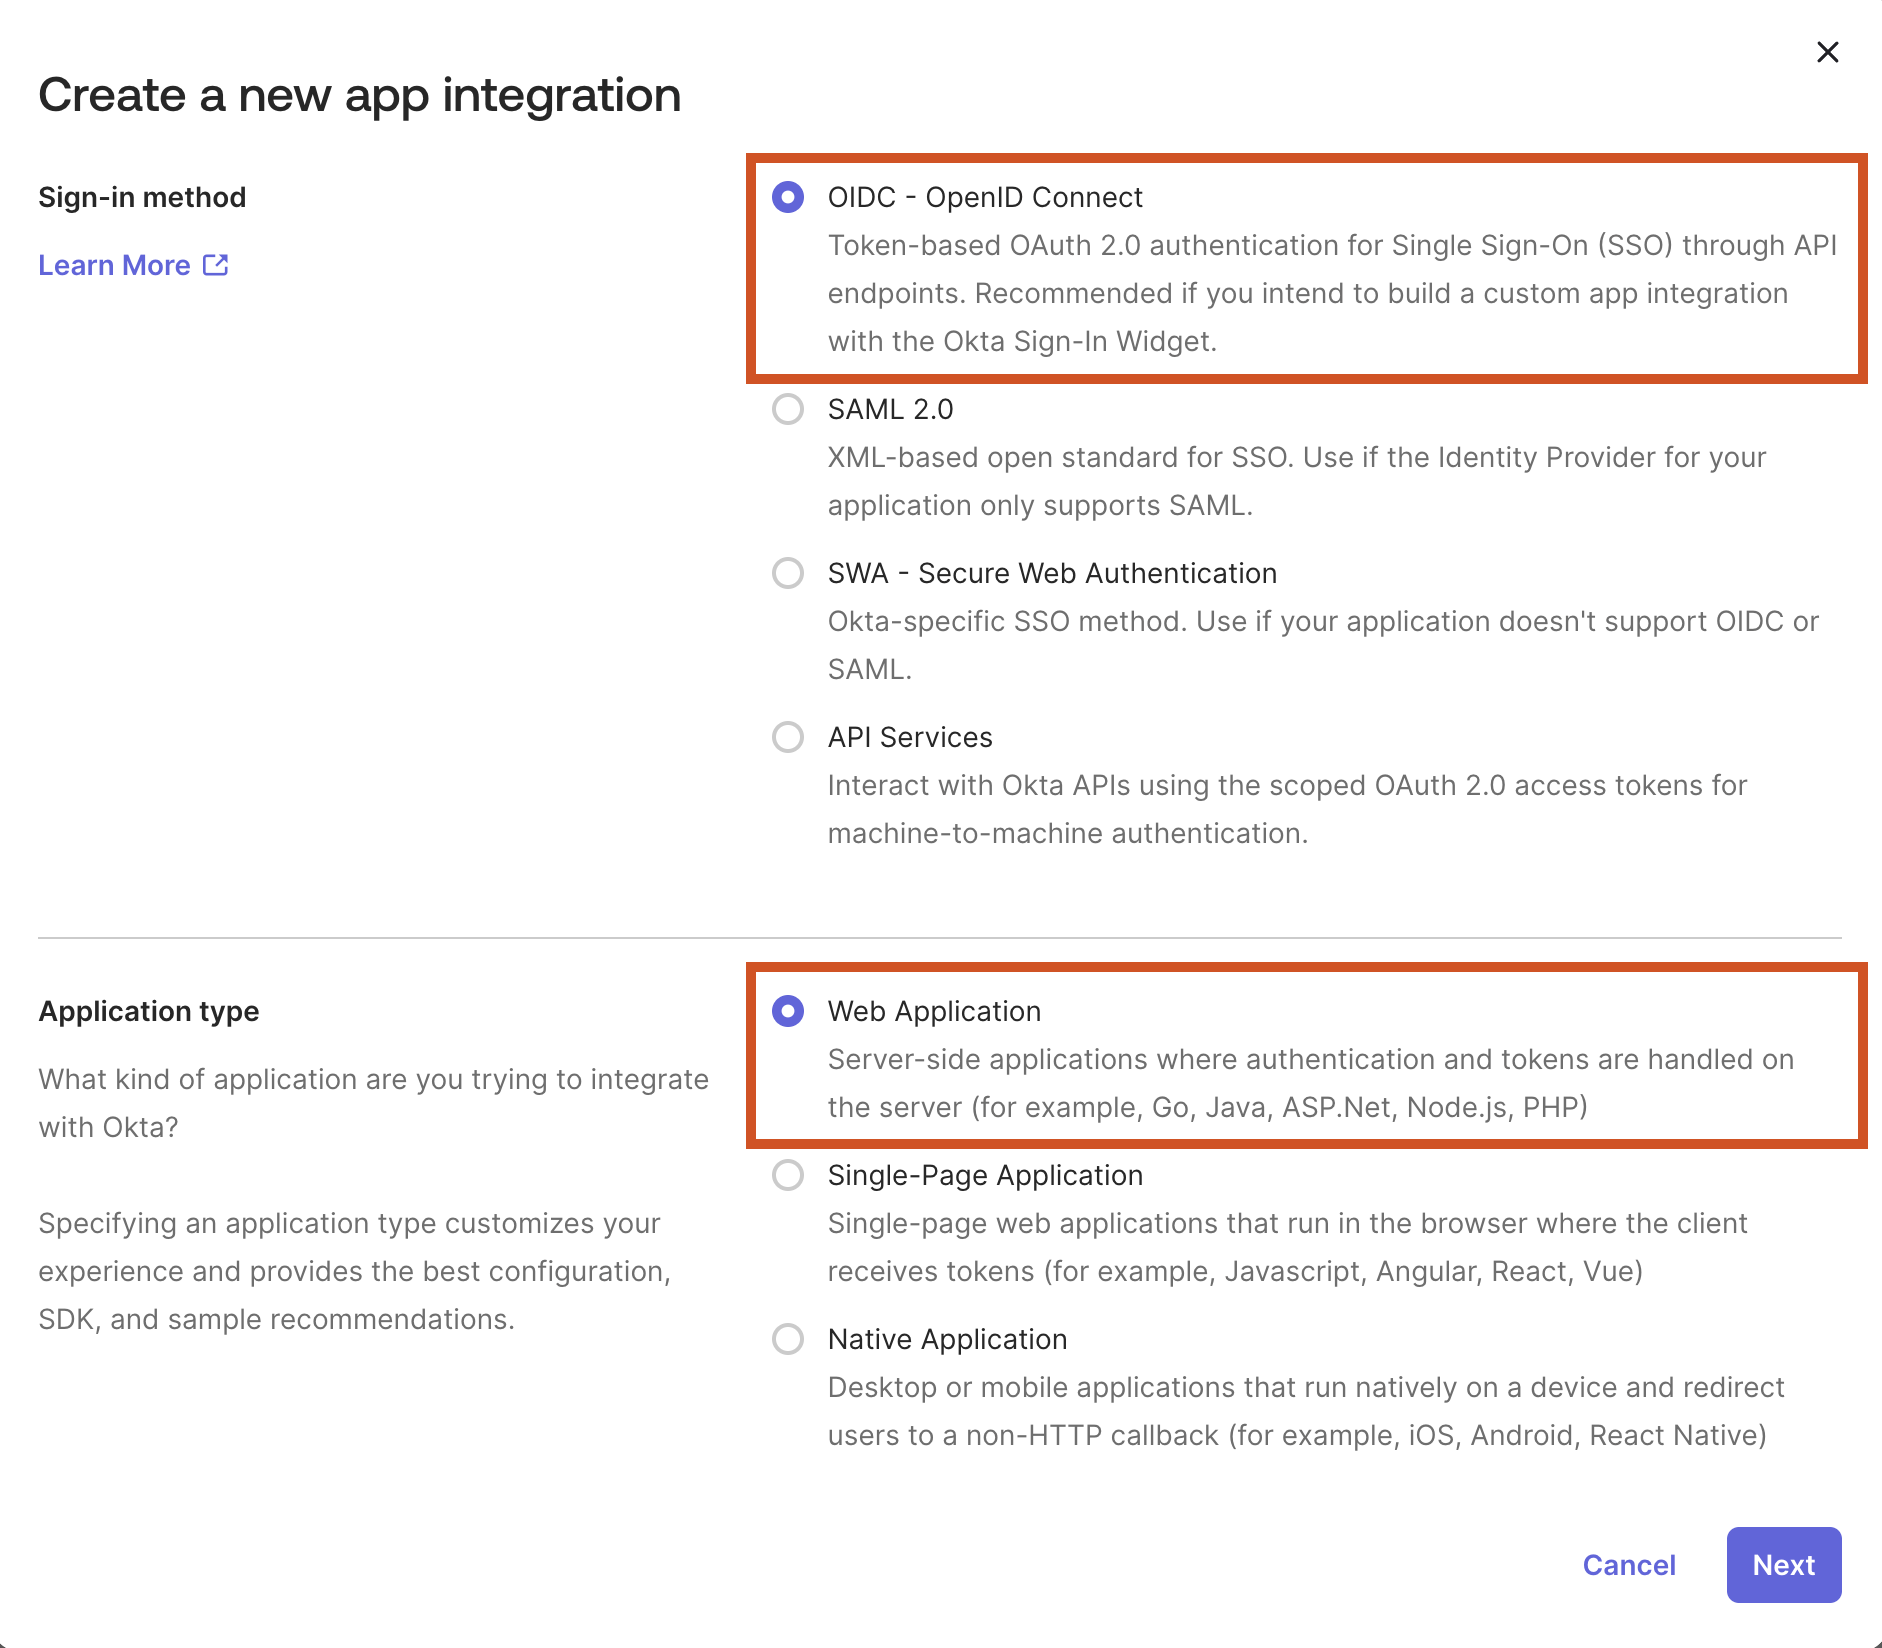
For Sign-in method, select OIDC - OpenID Connect. For Application type, select Web Application.
2. Get the XEIZE OIDC details
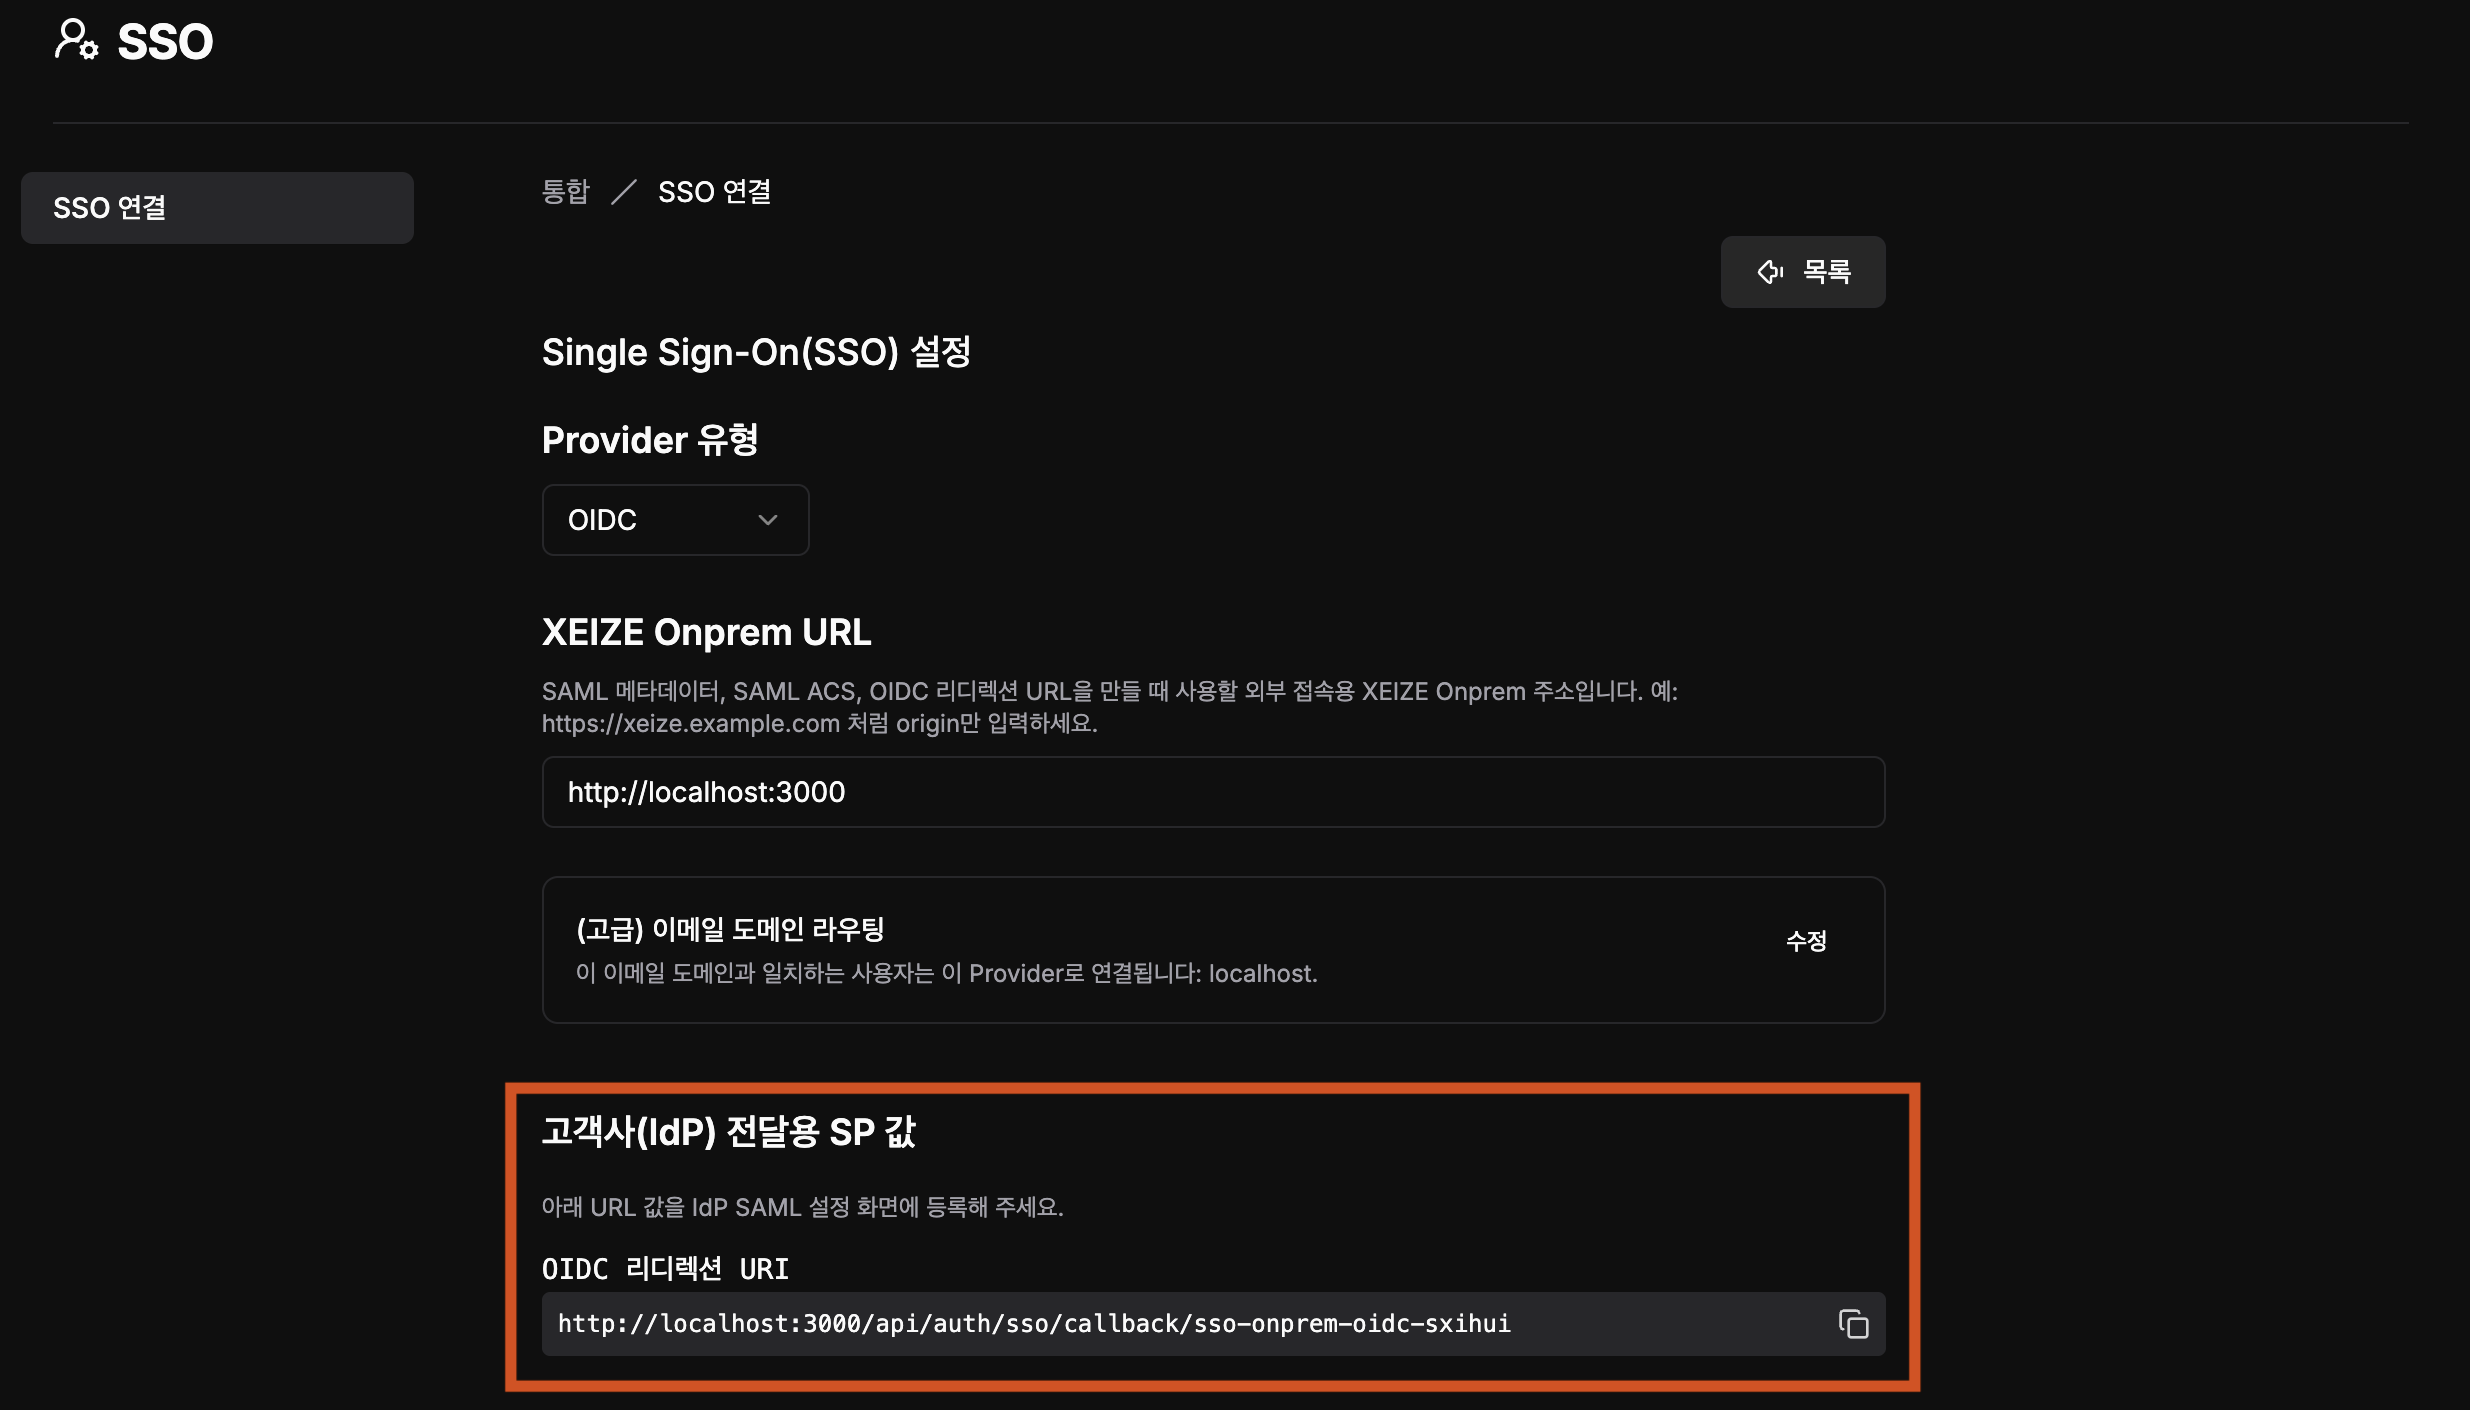
On the XEIZE SSO configuration page, verify that XEIZE Onprem URL is the actual address users will visit. Then copy the generated OIDC redirect URI, labeled OIDC 리디렉션 URI in the Korean interface shown. Do not copy the screenshot's localhost address into a production configuration.
3. Configure the Okta web app integration
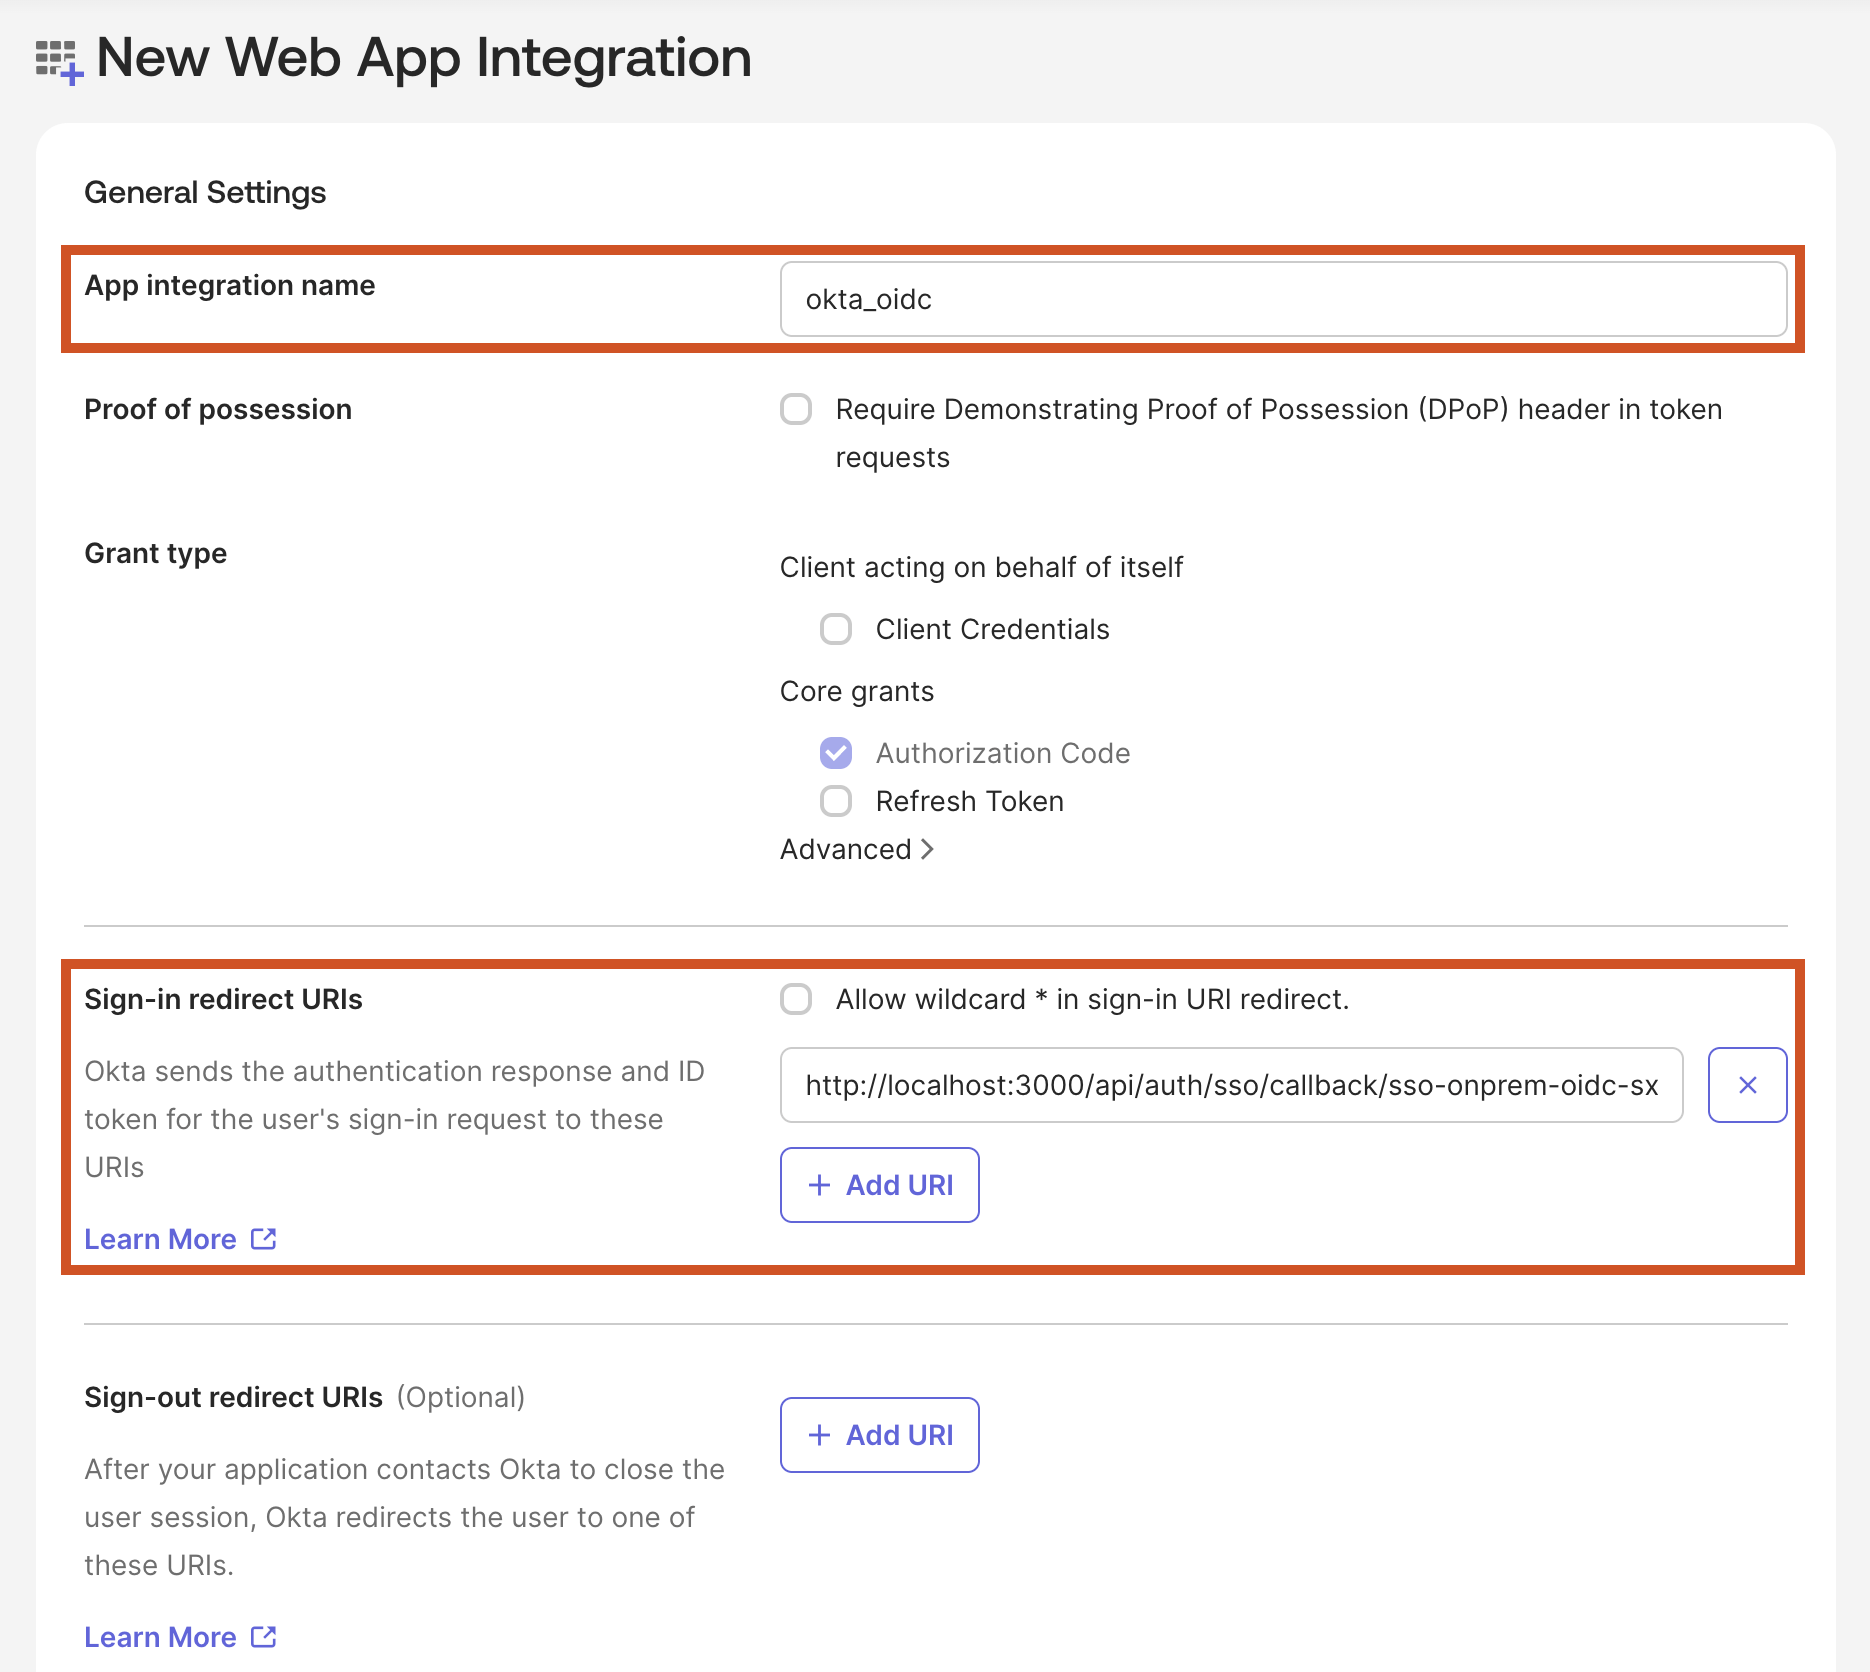
On the Okta Web App Integration setup page, enter an App integration name for XEIZE.
Paste the OIDC redirect URI you copied into Sign-in redirect URIs, then continue configuring the integration.
Configure access for your environment.
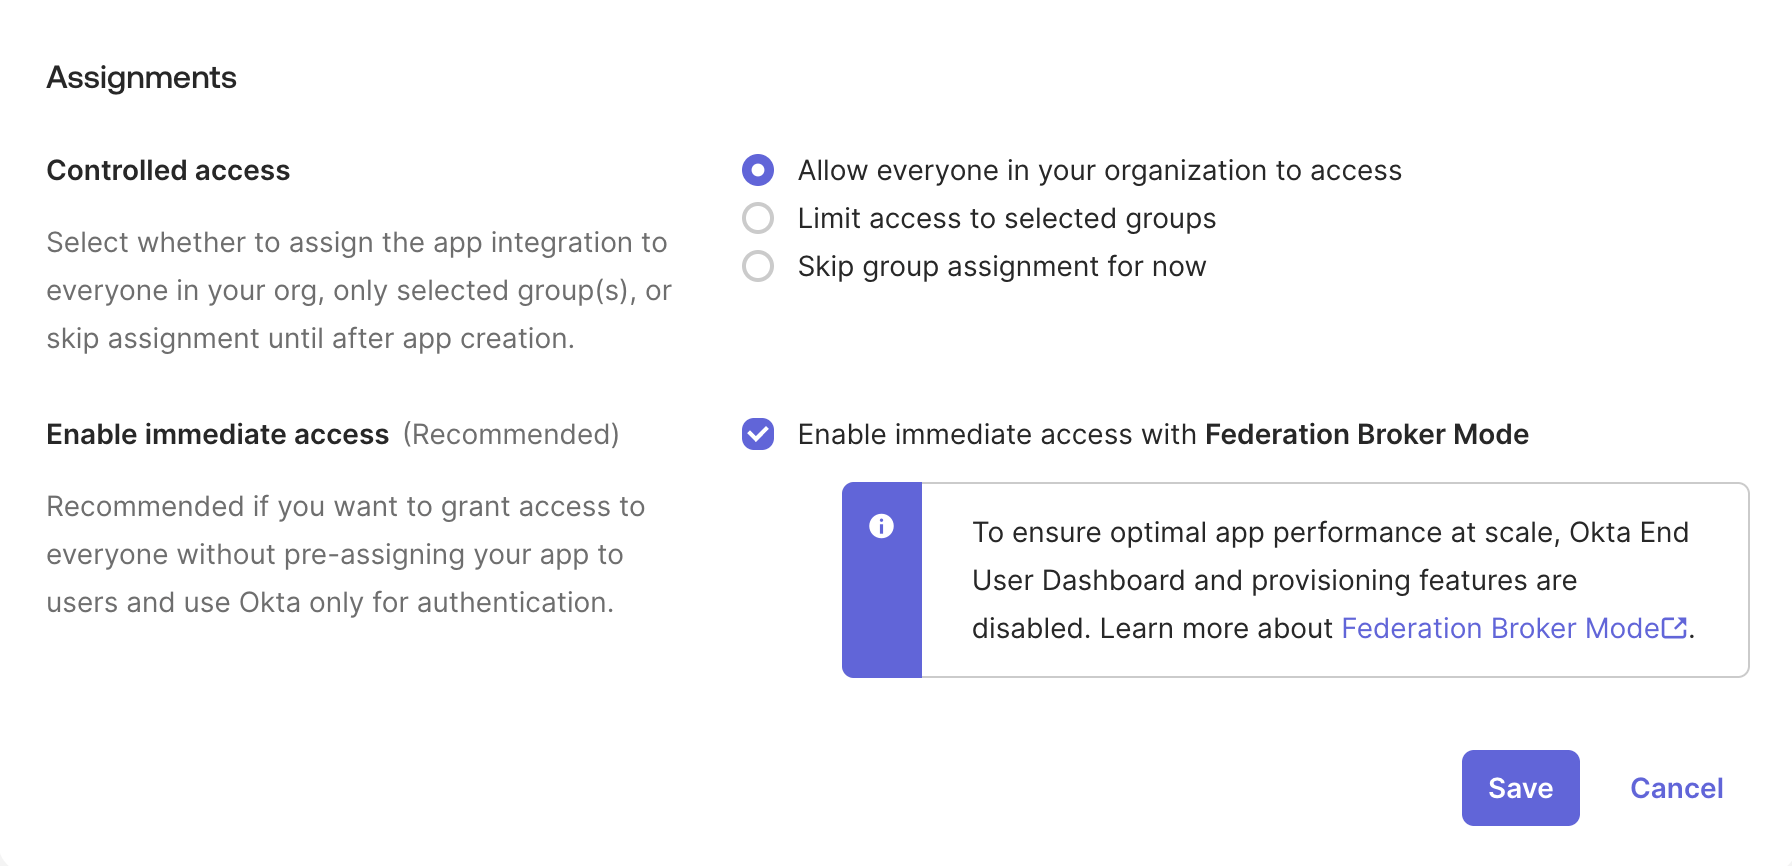
| Access option | Meaning |
|---|---|
| Allow everyone in your organization to access | Allows all users in the Okta organization to access the app. |
| Limit access to selected groups | Restricts access to the selected groups. |
| Skip group assignment for now | Defers group assignment until later. |
When you have finished configuring the app, select Save.
4. Get the Okta OIDC details
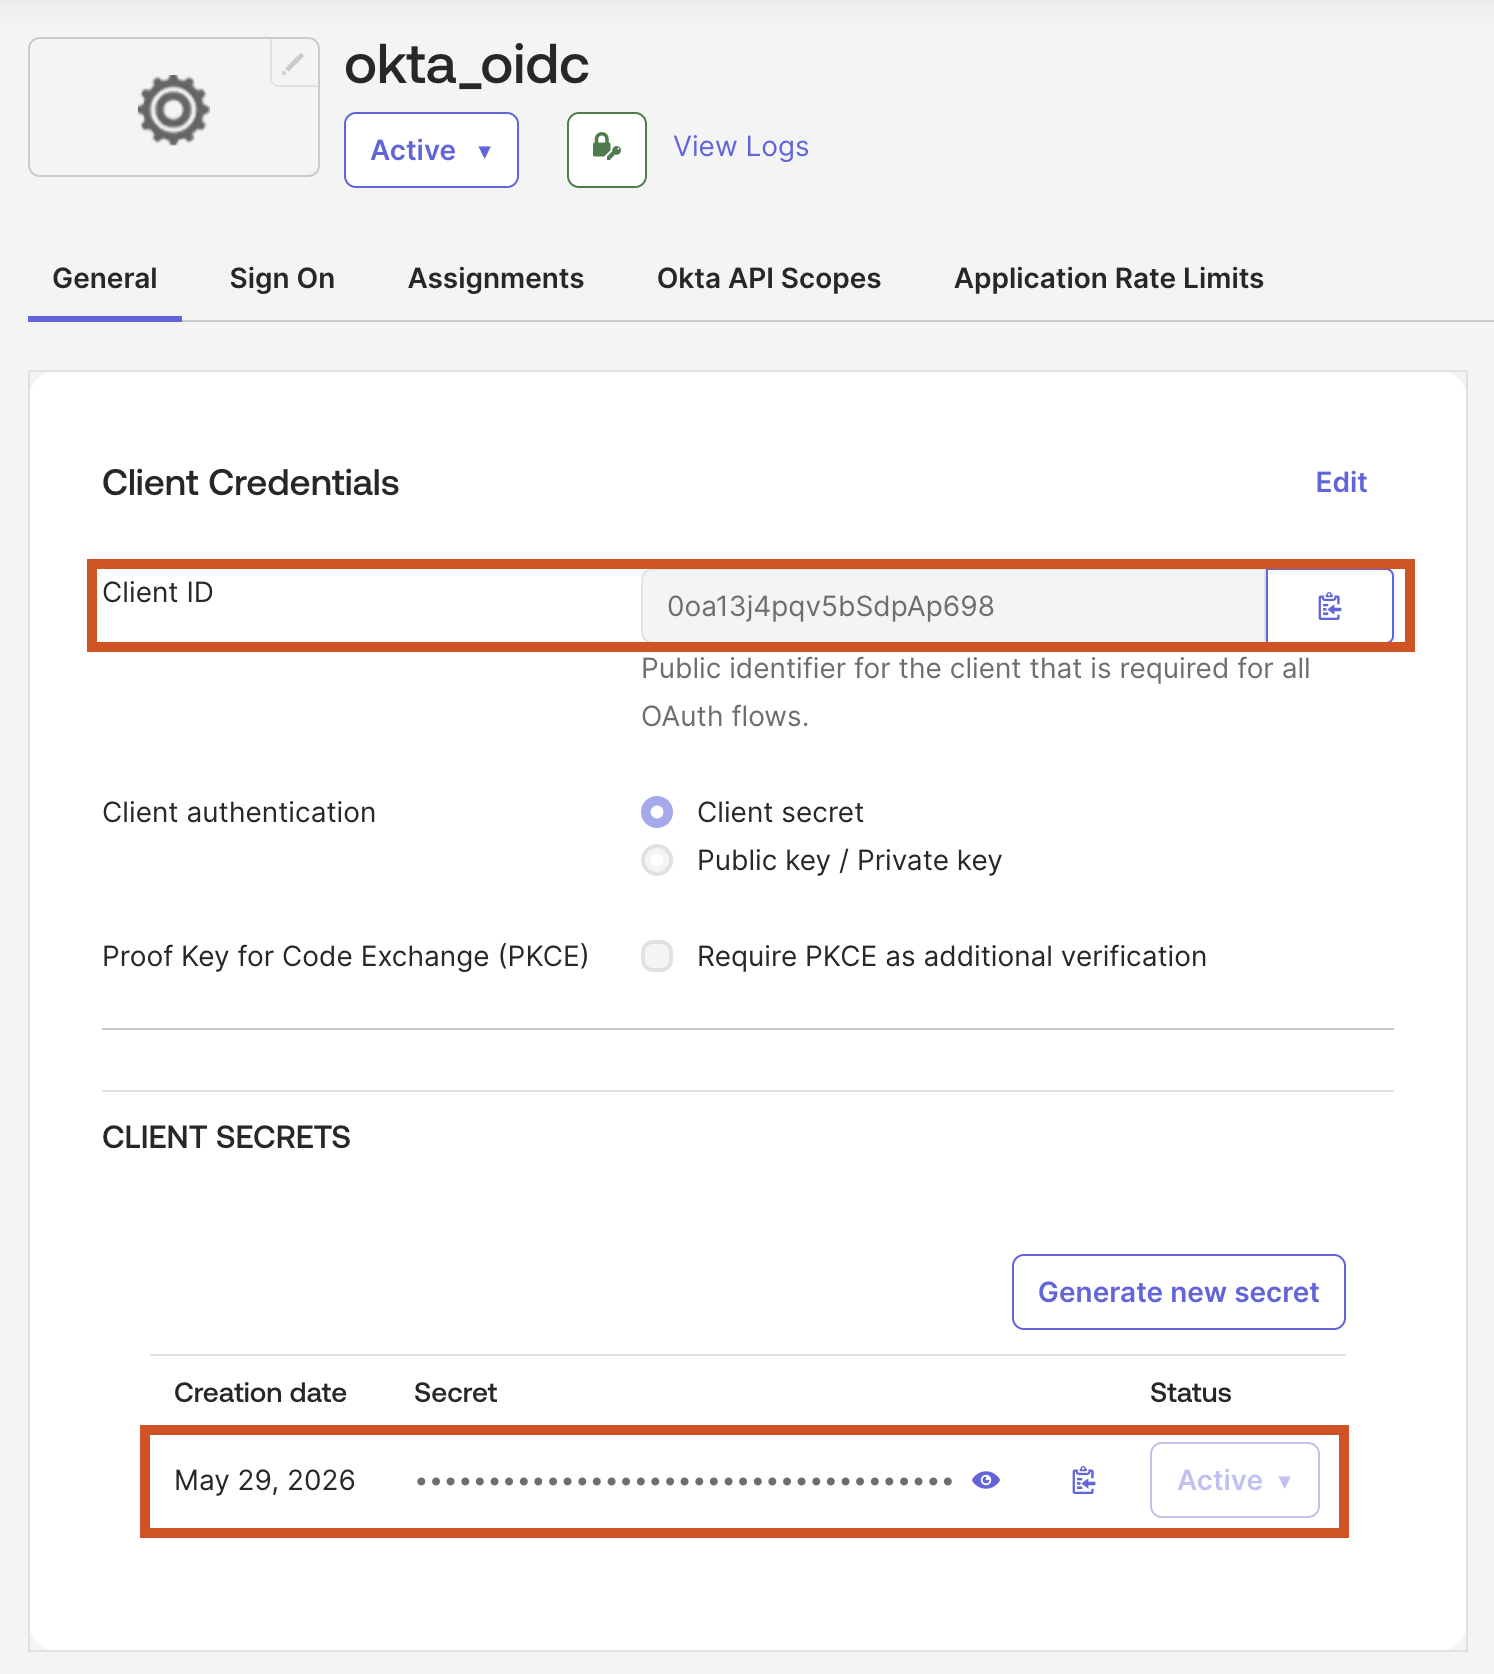
On the Okta App Integration settings page, copy the Client ID and Client Secret.
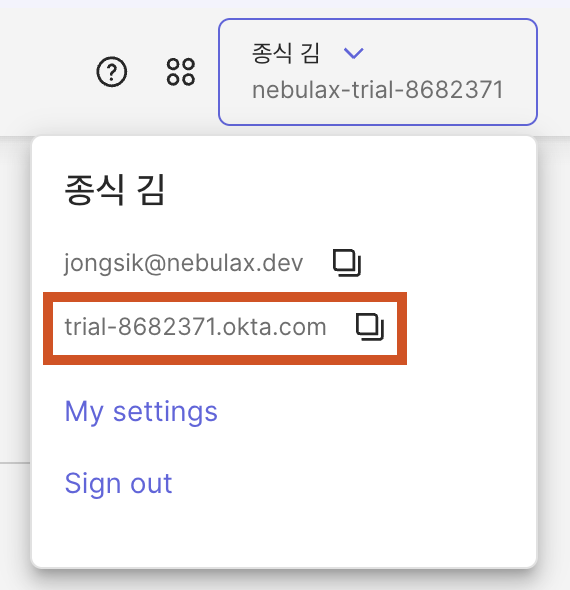
Open the account menu in the upper-right corner and copy your Okta Domain.
5. Configure OIDC in XEIZE
On the XEIZE SSO configuration page, enter the client ID and client secret. The Korean labels shown are 클라이언트 ID and 클라이언트 암호 (Secret).
In the OIDC preset selector, labeled OIDC 기본값 선택, choose the Okta template, shown as Okta (템플릿). Replace {your-okta-domain} in both the issuer and discovery endpoint with the Okta Domain you copied. Insert only the hostname in this placeholder. For example, the domain example.okta.com gives an issuer of https://example.okta.com.
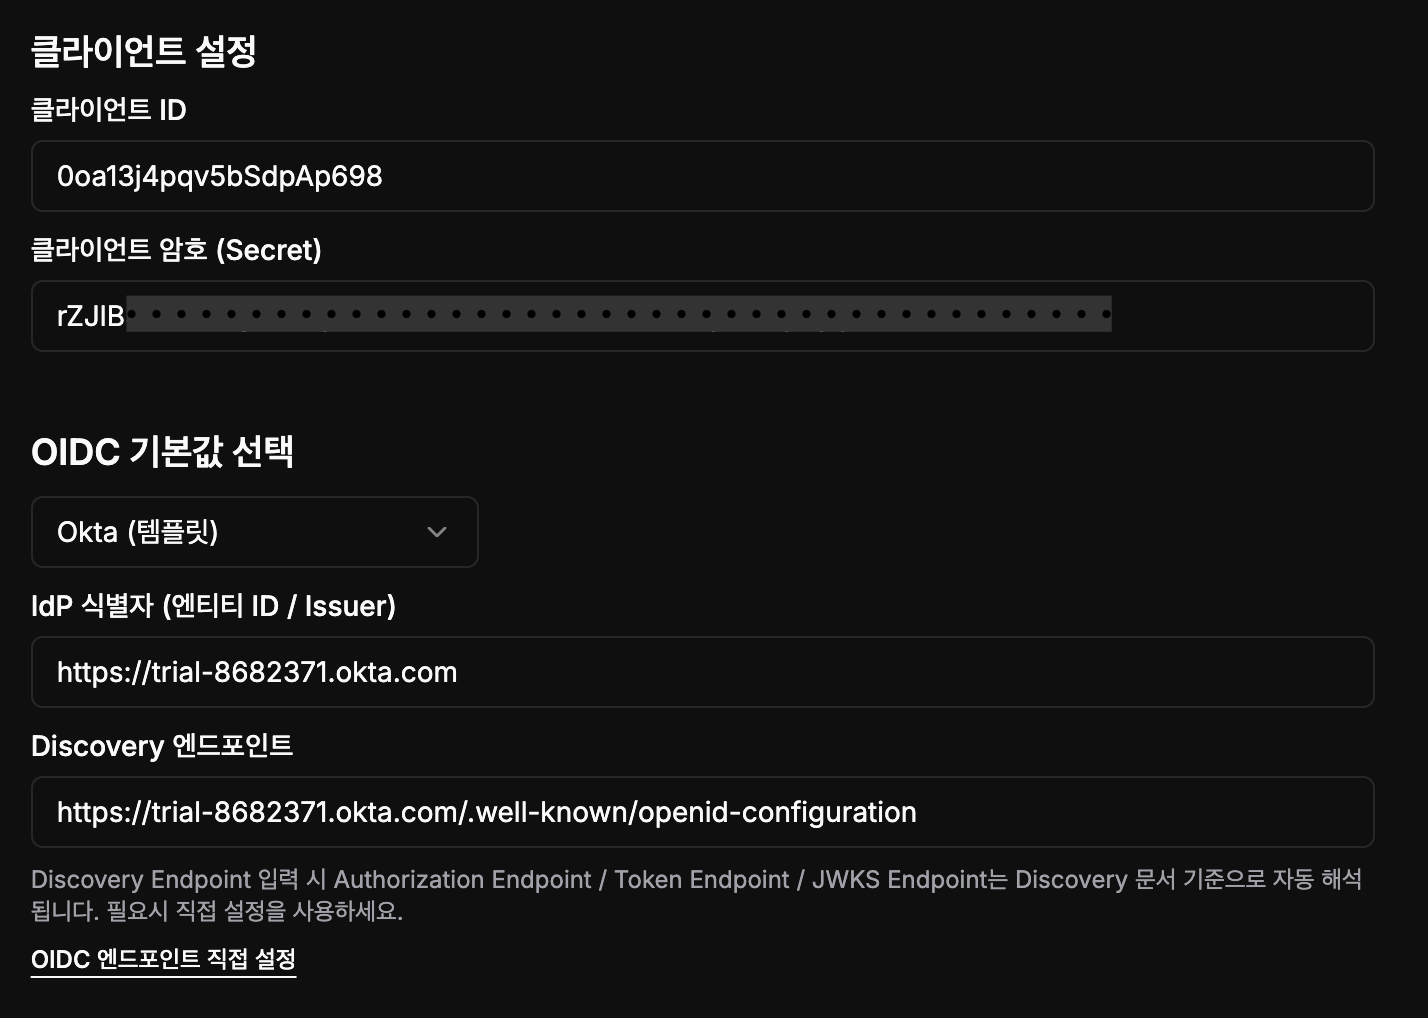
The template's discovery endpoint is https://{your-okta-domain}/.well-known/openid-configuration. A custom authorization server has different issuer and discovery addresses; if you use one, configure its actual values. Check your entries and save the XEIZE settings.
6. Test sign-in
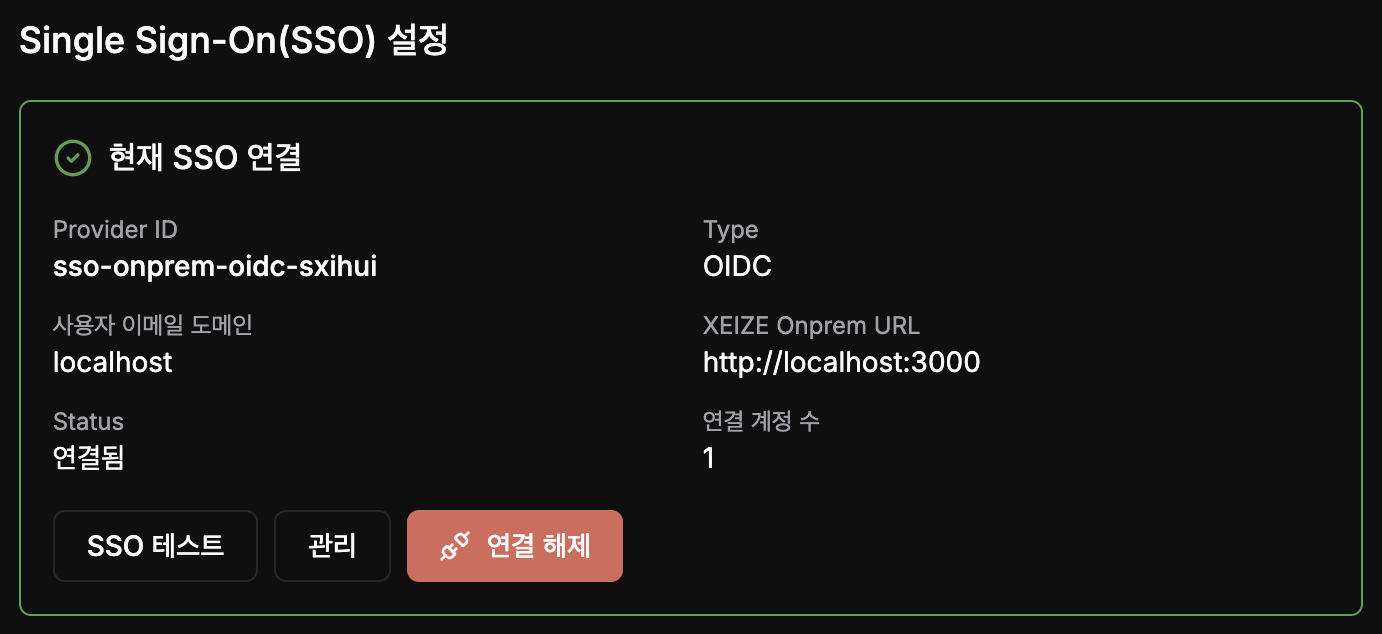
After saving the configuration, select the SSO test button, labeled SSO 테스트, and verify that an account with access can sign in successfully.
Troubleshooting and references
If SSO sign-in does not work, check the following:
- The Sign-in redirect URIs registered in the Okta App Integration must match the OIDC redirect URI from XEIZE.
- Verify the client ID and client secret saved in XEIZE.
- Make sure the Okta domain was inserted correctly in place of
{your-okta-domain}in the XEIZE OIDC settings. - Check that the user is allowed to access the Okta App Integration.
- Check that the user information sent by Okta, including the email address, meets XEIZE's account linking and registration policies.
For more information, see Okta OIDC app integrations.
For the address differences between org and custom authorization servers, see Okta Authorization servers.